
Loading story…
Microsoft has tracked Storm-2570, a ransomware affiliate active since April 2025, across the Qilin, DragonForce, Anubis, and BERT ransomware-as-a-service ecosystems. The actor has targeted organizations in North America and Europe across multiple sectors, retaining a consistent intrusion playbook despite rotating ransomware payloads: abuse of remote-management and tunneling software, credential theft, network reconnaissance, lateral movement through PsExec, RDP, and SMB, theft of NTDS.dit, Microsoft Defender tampering, cloud-based data theft, and encryption.
Organizations should investigate unauthorized RMM software, encrypted outbound tunnels, Defender configuration changes, directory-database access, and s5cmd or Rclone activity as potential precursor signals. Microsoft recommends maintaining Defender’s always-on protections and tamper protection, which locks critical antivirus controls and alerts on attempted changes; any necessary administrative override should be restricted to authorized, time-limited troubleshooting mode and reviewed through Defender telemetry, device timelines, and advanced hunting.
TTPs, infrastructure, and targeting history in one profile.
1 event from the most recent confirmed update back to the earliest known activity.
Microsoft Threat Intelligence has tracked Storm-2570 since April 2025. The affiliate has operated across the Qilin, DragonForce, Anubis, and BERT ransomware-as-a-service ecosystems, targeting organizations in North America and Europe and using credential theft, lateral movement, data exfiltration, Defender tampering, and ransomware deployment.
Vulnerabilities, threat actors, malware, products, organizations, and breaches Mallory has linked to this story.
See this adversary's TTPs, infrastructure, and targeting history, correlated against your exposure.
4 references tracked. Mallory keeps watching after this page renders.
microsoft.com
Open sourcelearn.microsoft.com
Open sourcelearn.microsoft.com
Open sourcelearn.microsoft.com
Open sourceMap indicators from this story to your assets and identify affected systems in minutes.
Every observed campaign, victim, and pivot linked to actors named in this story.
Malware, exploits, and IOCs connected to the activity described here.
YARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Get matching new stories delivered to your team as they break — not the next morning.
Ask questions about this story and take action on the answers.
Other stories Mallory is tracking that overlap on entities, sources, or topic labels.
Microsoft said threat actor **Storm-1175** is running high-tempo intrusions that exploit newly disclosed and, in some cases, previously unknown vulnerabilities in internet-facing systems to steal data and deploy **Medusa ransomware** within days or even 24 hours. The financially motivated group has heavily impacted healthcare organizations and also targeted education, professional services, and finance in Australia, the United Kingdom, and the United States. Since 2023, the actor has exploited more than 16 flaws across products including **Microsoft Exchange**, **PaperCut**, **Ivanti**, **ConnectWise ScreenConnect**, **JetBrains TeamCity**, **SimpleHelp**, **CrushFTP**, **GoAnywhere MFT**, **SmarterMail**, **SAP NetWeaver**, and **BeyondTrust**, with Microsoft also observing zero-day use against SmarterMail and GoAnywhere before public disclosure. After gaining access, Storm-1175 establishes persistence with new administrator accounts, web shells, and remote management tools, then moves laterally using LOLBins, **Impacket**, **PDQ Deployer**, and Cloudflare tunnels while stealing credentials from **LSASS**, `NTDS.dit`, `SAM`, and backup systems. Microsoft said the actor tampers with Microsoft Defender settings to reduce detection, uses **Bandizip** and **Rclone** for collection and exfiltration, and deploys Medusa through PDQ Deployer or Group Policy; the group has also shown interest in Linux targets such as vulnerable **Oracle WebLogic** servers. Microsoft urged organizations to reduce exposure of web-facing assets, patch quickly, enforce MFA on approved RMM tools, restrict local administrator rights, and enable protections such as **Credential Guard**, tamper protection, and Defender XDR attack disruption features.
Aug 18, 2026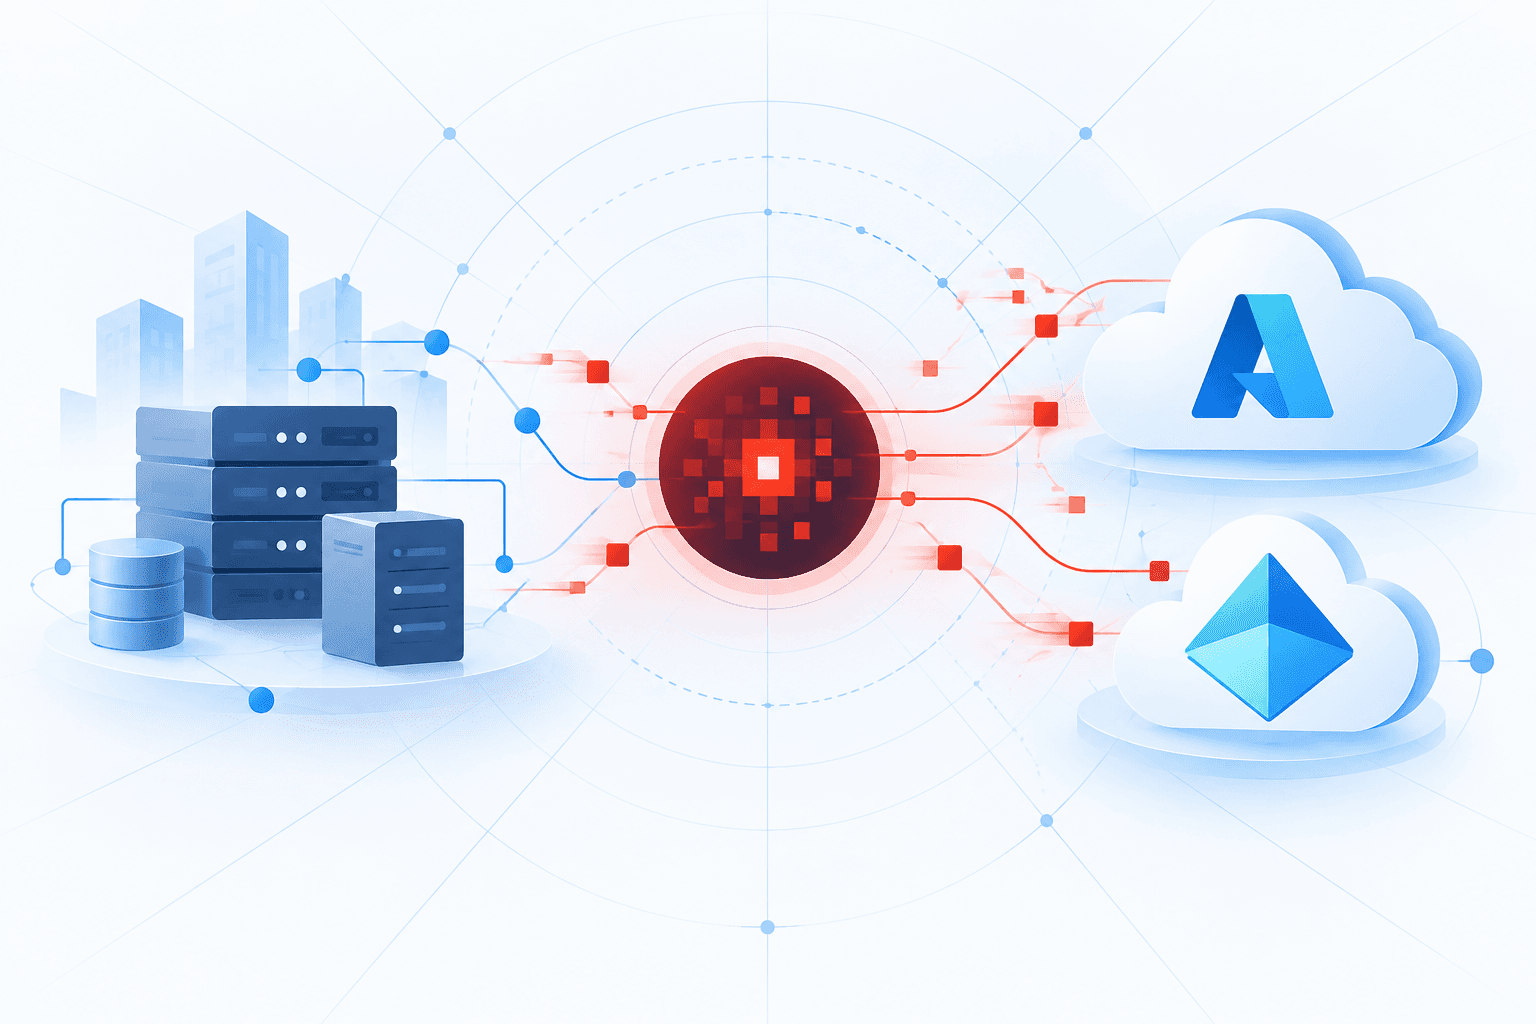
Embargo, also tracked as **Storm-0501** and G1053, is conducting double-extortion ransomware operations against organizations in technology, healthcare, manufacturing, and other sectors. The group steals data—frequently using Rclone to MEGA—before encrypting systems with ChaCha20 and Curve25519. Researchers assess it as a probable BlackCat/ALPHV successor or rebrand based on Rust-based tooling, leak-site similarities, timing, and reported cryptocurrency-wallet overlap, though direct organizational continuity remains unconfirmed. Its intrusion activity includes exploiting internet-facing vulnerabilities, purchasing or abusing credentials, compromising Active Directory, and using bring-your-own-vulnerable-driver techniques to terminate security products. Microsoft reported that Storm-0501 has expanded beyond on-premises encryption into cloud-focused extortion by pivoting from Active Directory into Microsoft Entra ID and Azure. In one enterprise intrusion, the actor abused an Entra Connect Sync server and an MFA-less synchronized Global Administrator account, established federation-based persistence with AADInternals, exposed Azure Storage, and exfiltrated data with AzCopy. The group then sought to destroy cloud storage and backups by removing locks and immutability controls; where deletion was prevented, it used customer-managed keys and encryption scopes to render blobs inaccessible and attempted to delete the associated keys. Embargo also uses MDeployer and MS4Killer for persistence and defense evasion, including Safe Mode services, scheduled tasks, registry changes, and the vulnerable `probmon.sys` driver before disabling recovery and encrypting victims’ files.
Sep 20, 2026
Storm-0249, an initial access broker previously known for selling access to compromised networks, has adopted advanced techniques to facilitate ransomware attacks. The group now leverages social engineering tactics such as ClickFix, which tricks users into executing malicious commands via the Windows Run dialog. These commands use legitimate utilities like `curl.exe` to download and execute fileless PowerShell scripts from spoofed Microsoft domains, ultimately deploying malicious MSI packages with SYSTEM privileges. The attack chain includes DLL sideloading, where a trojanized DLL is placed alongside legitimate EDR components (notably SentinelOne's `SentinelAgentWorker.exe`), allowing the attacker's code to run within trusted processes and evade detection. Once persistence is established, Storm-0249 abuses EDR tools to collect system information and maintain stealthy access, making detection and remediation challenging for defenders. This evolution in Storm-0249's tactics demonstrates a shift from mass phishing to highly targeted, stealthy operations that exploit trusted security software for malicious purposes. The abuse of EDR solutions not only enables the bypassing of traditional security controls but also provides a reliable foothold for ransomware deployment. Security researchers recommend implementing robust email filtering, monitoring for unusual use of legitimate utilities, and updating detection rules to identify these advanced techniques. Organizations are urged to review their EDR configurations and monitor for signs of DLL sideloading and unauthorized PowerShell activity to mitigate the risk posed by this threat actor.
Jun 29, 2026