Console Named-Pipe Injection Evades WriteProcessMemory Monitoring
Attack Tradecraft · 4 sources · Updated 1mo ago · First seen Sep 27, 2026
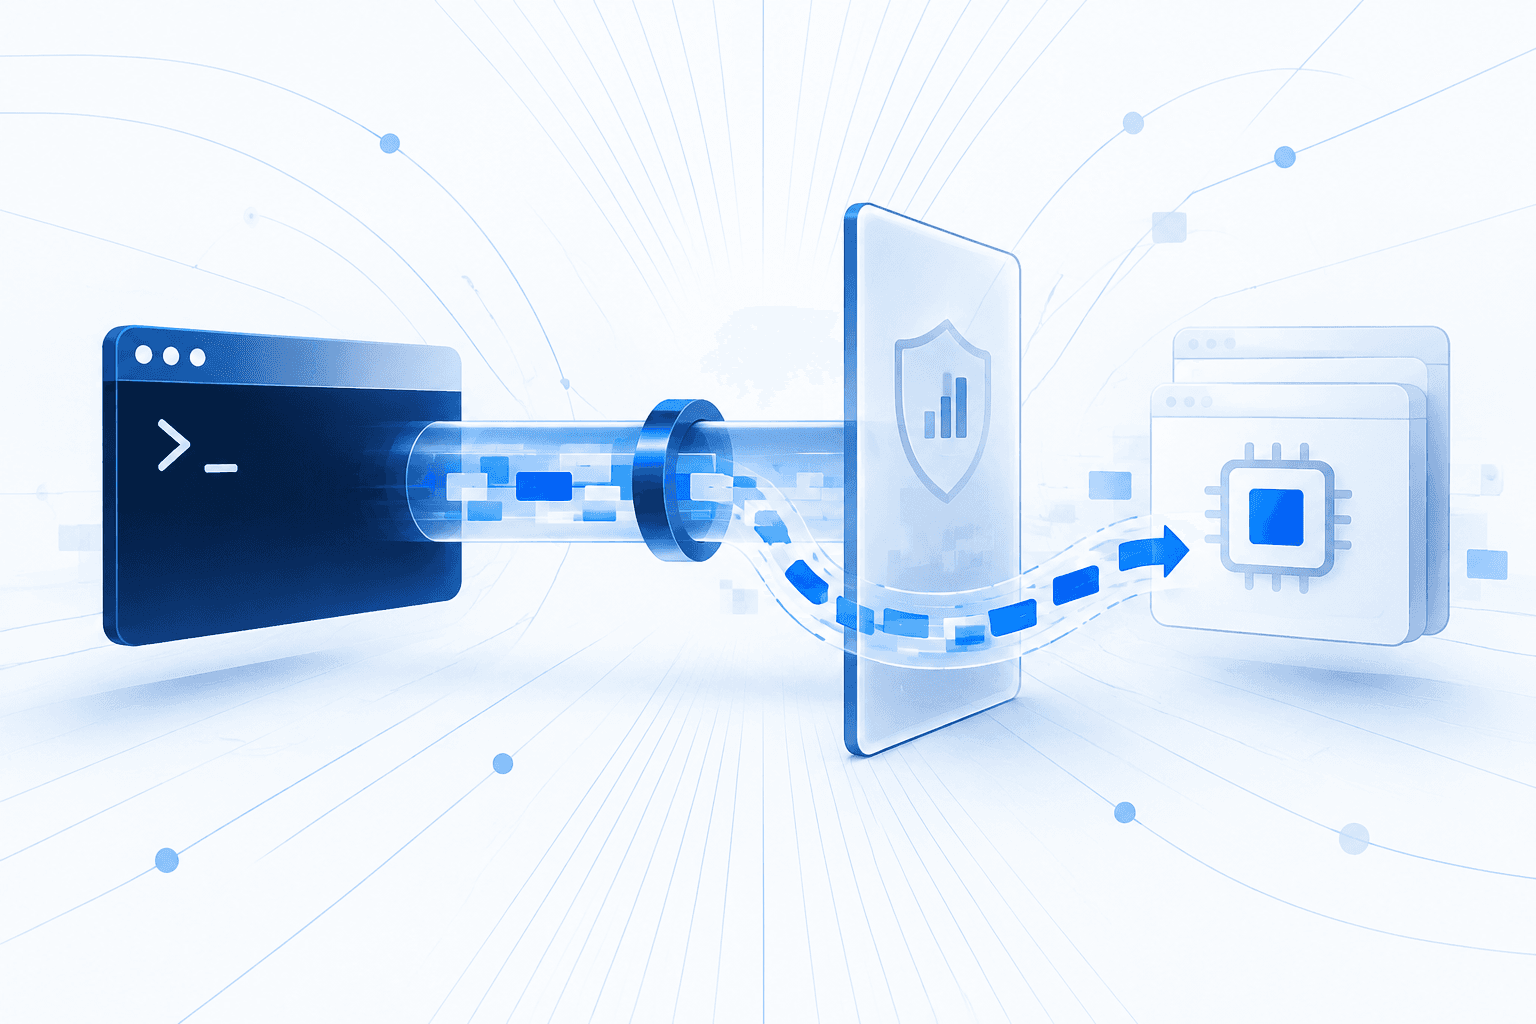
A newly published Windows process-injection technique, described as console named-pipe injection, places payload bytes into an interactive console child process through its standard-input named pipe rather than using the heavily monitored VirtualAllocEx and WriteProcessMemory APIs. The proof of concept launches a console application, sends bytes through standard input with WriteFile, identifies the resulting in-process buffer, changes its protection using VirtualProtectEx, and redirects a thread to execute the payload.
The technique is presented for authorized red-team and penetration-testing use, with no reported vulnerability, threat actor, malware campaign, or confirmed in-the-wild exploitation. Defenders should assess detections for remote VirtualProtectEx activity and unusual named-pipe read/write behavior involving console processes—particularly commonly abused binaries such as netsh.exe and nslookup.exe—rather than relying solely on alerts for cross-process memory allocation or WriteProcessMemory.