Mallory
← Back to News
identity-authentication-vulnerabilityai-platform-securitycredential-access-methodwidely-deployed-product-advisory

MCP Python SDK OAuth Discovery Flaw Exposes Credentials to Malicious Servers

Vulnerability Disclosure · 4 sources · Updated 2mo ago · First seen Sep 28, 2026
MCP Python SDK OAuth Discovery Flaw Exposes Credentials to Malicious Servers

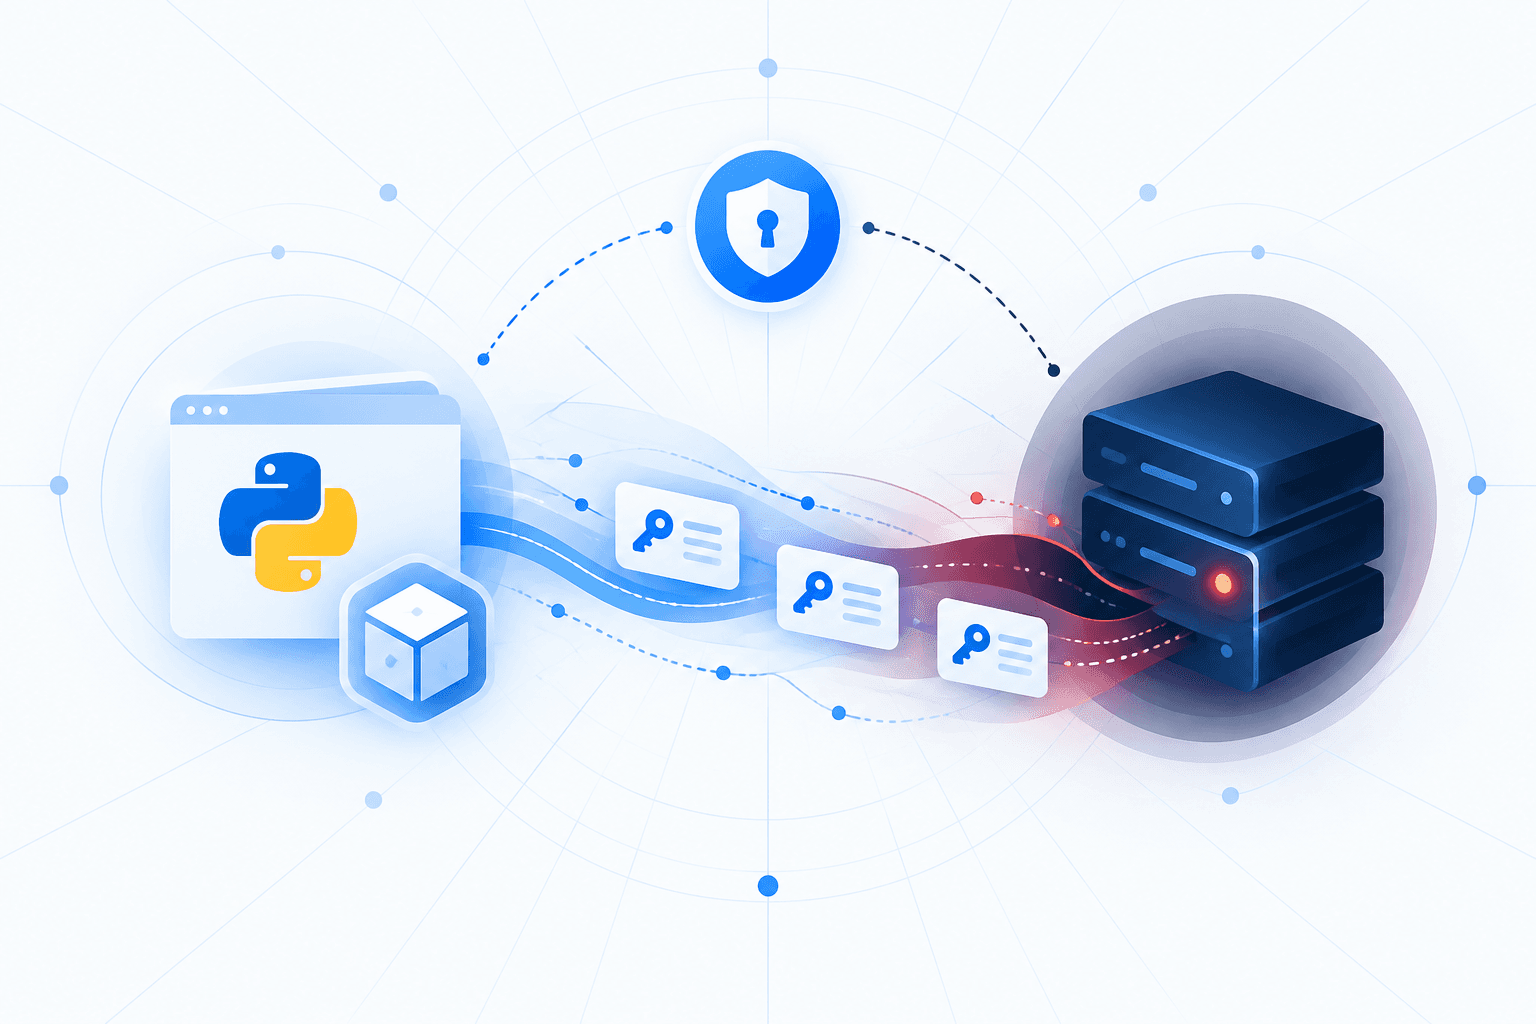
A high-severity OAuth credential-disclosure vulnerability in Anthropic's official Model Context Protocol (MCP) Python SDK can allow a malicious HTTP MCP server to capture OAuth client secrets, authorization codes, PKCE verifiers, and ultimately valid access tokens. The attack abuses authorization-server discovery: an attacker-controlled server returns a 404 for modern discovery to trigger a legacy fallback that does not validate the issuer, then supplies malicious authorization metadata or token endpoints while presenting a legitimate identity-provider login flow to the user.

The issue affects mcp versions 1.9.1 through 1.29.1 and 2.0.0 through 2.1.1, including OAuthClientProvider, ClientCredentialsOAuthProvider, and PrivateKeyJWTOAuthProvider configurations using vulnerable OAuth providers. It is fixed in versions 1.30.0 and 2.2.0; organizations should upgrade, explicitly bind machine-to-machine or pre-provisioned credentials to the expected issuer, remove legacy stored registrations, and rotate exposed client secrets and revoke potentially compromised tokens. No CVE or confirmed exploitation had been reported.
Do you run this?See affected versions and whether adversaries are exploiting it.
Check your exposure
Event timeline

How this story unfolded

Events from the most recent confirmed update back to the earliest known activity.

2 events
  1. Reported Sep 28, 20262mo ago

    OAuth credential-redirection flaw publicly disclosed

    Cycode and the MCP security advisory publicly disclosed a high-severity OAuth flaw in the MCP Python SDK. A malicious HTTP MCP server could exploit legacy discovery handling to route authorization codes, client secrets, and PKCE verifiers to attacker-controlled token infrastructure, enabling account takeover.

    MCP SDK OAuth Flaw Enabled Account Takeover (CVE Fix Inside)
  2. Reported Sep 28, 20262mo ago

    MCP Python SDK releases issuer-validation fixes

    Anthropic released MCP Python SDK versions 1.30.0 and 2.2.0, adding expected authorization-service determination, metadata rejection for mismatched providers, and credential binding. The releases addressed OAuth discovery weaknesses affecting HTTP clients using untrusted MCP servers.

    MCP SDK OAuth Flaw Enabled Account Takeover (CVE Fix Inside)
Linked entities

Related entities

Vulnerabilities, threat actors, malware, products, organizations, and breaches Mallory has linked to this story.

Open in app →

Organizations

1 linked
Anthropic
Do you run this?See whether adversaries are exploiting this yet, and where the affected versions run in your environment.
Check Your Exposure
Mallory platform

See the full picture, correlated to your attack surface.

This page covers what’s public. Mallory adds the parts that aren’t: which of your assets are affected, which threat actors are using it right now, and what to deploy next.

Exposure mappingMap indicators from this story to your assets and identify affected systems in minutes.
Threat actor evidenceEvery observed campaign, victim, and pivot linked to actors named in this story.
Associated malwareMalware, exploits, and IOCs connected to the activity described here.
Detection signaturesYARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Scheduled alertsGet matching new stories delivered to your team as they break, not the next morning.
AI threadsAsk questions about this story and take action on the answers.