TrustSink Rogue Entra MFA Provider Steals Passwords During Legitimate Sign-ins
Attack Tradecraft · 3 sources · Updated 2mo ago · First seen Sep 28, 2026
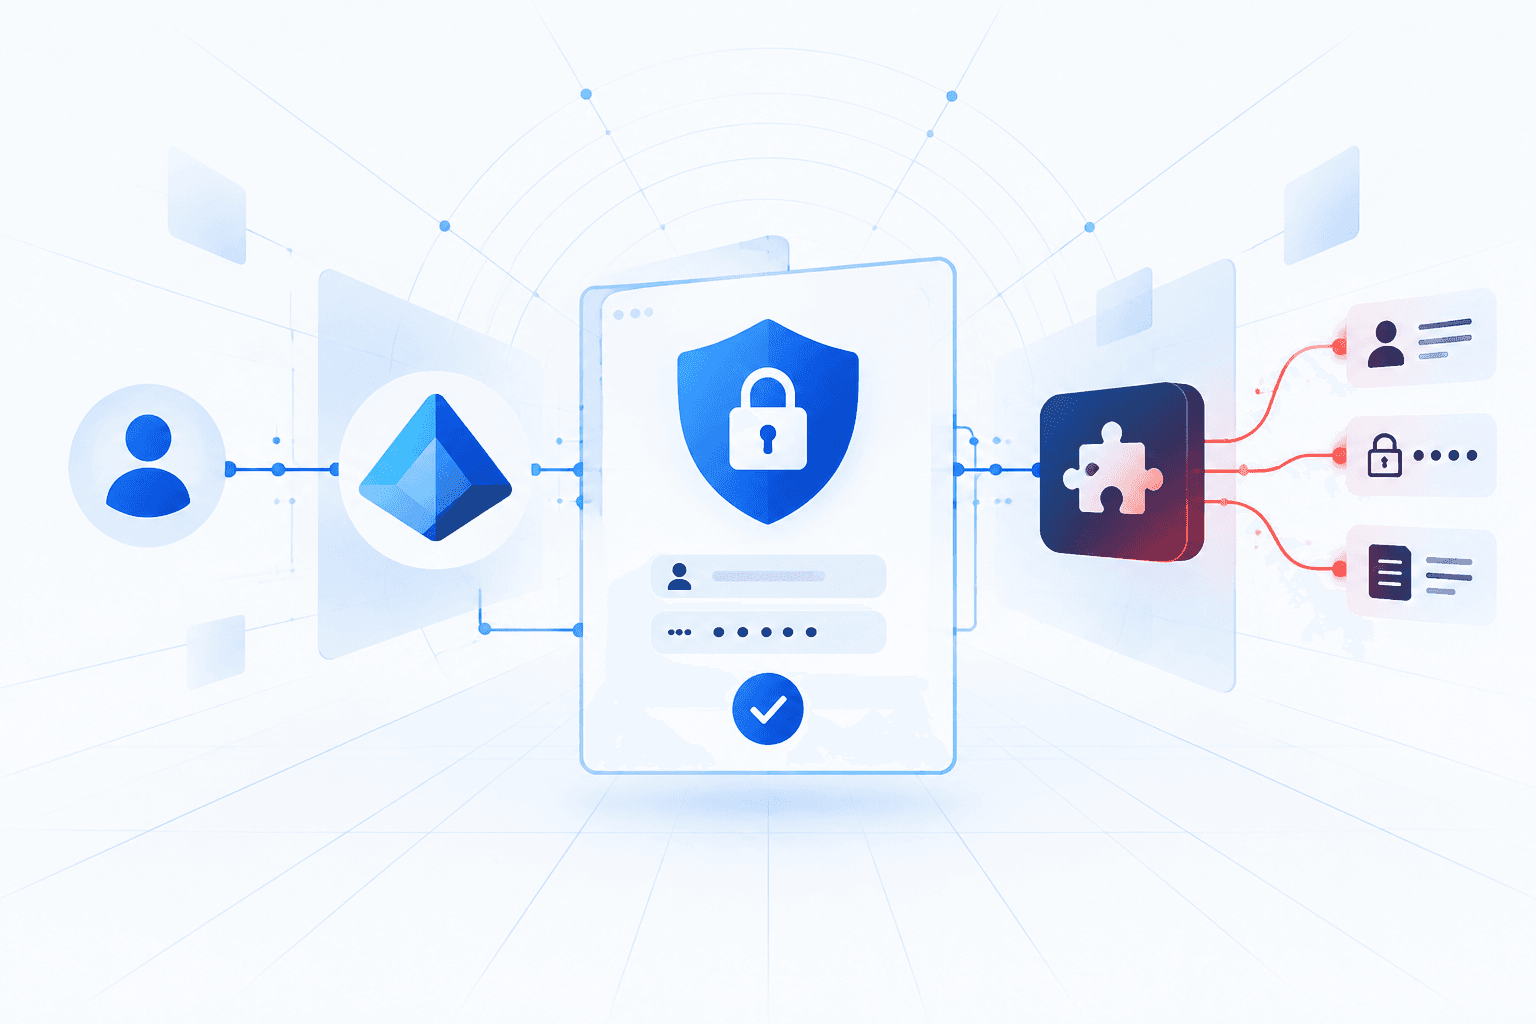
Varonis Threat Labs disclosed TrustSink, a post-compromise Microsoft Entra persistence and credential-phishing technique that abuses External Authentication Methods (EAMs). An attacker with Global Administrator or Authentication Policy Administrator privileges can register a malicious OIDC authentication provider and associated Entra application, present victims with a convincing Microsoft password prompt during a legitimate MFA flow, and capture plaintext credentials while returning a valid signed success response to Entra. Victims can complete MFA and access the intended application normally, concealing the theft.
The rogue provider can remain active after a password reset and capture replacement passwords at the next sign-in, so password resets alone do not remediate an intrusion. Organizations should monitor Authentication Methods Policy changes; newly created applications, service principals, and consent grants; unfamiliar EAM issuer URLs and redirect URIs; and hardware-key claims without a corresponding legitimate enrollment. Incident responders should remove the malicious external authentication method and all related Entra artifacts before resetting affected users' credentials.