GitHub AI Agent Finds 24 Android Vulnerabilities in Open-Source Apps
Vulnerability Disclosure · 4 sources · Updated 2mo ago · First seen Sep 28, 2026
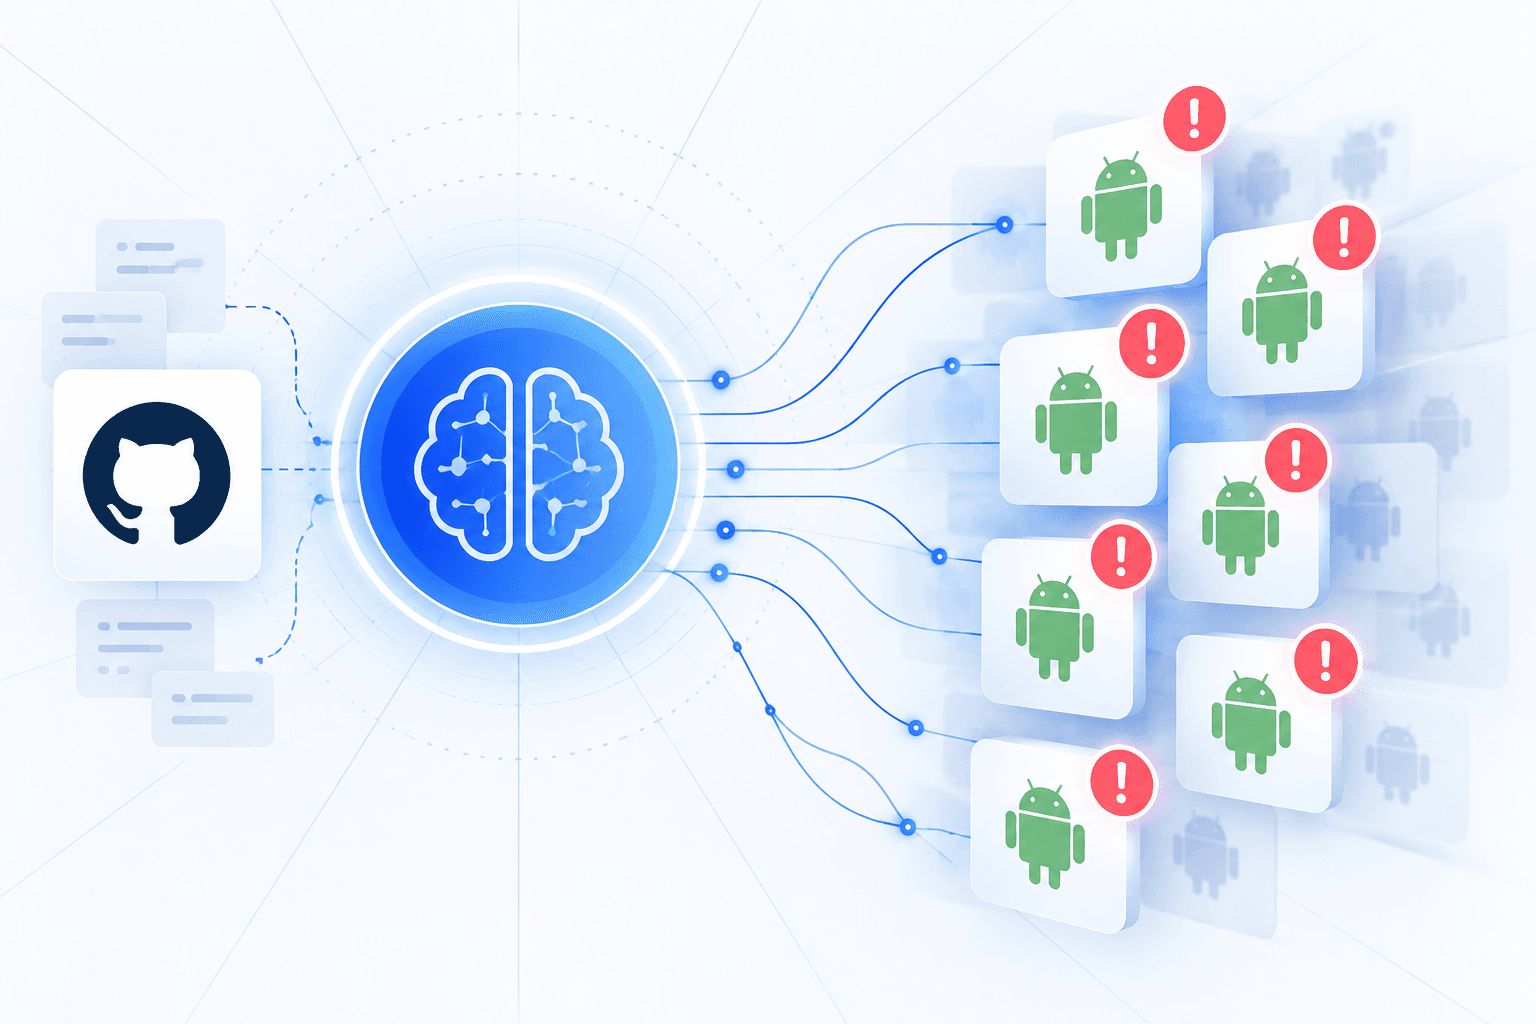
GitHub Security Lab reported that targeted, AI-assisted taskflows identified and disclosed 24 Android vulnerabilities in open-source applications. The workflows direct an open-source AI security agent to map mobile attack surfaces, locate entry points such as exported components and deep links, and evaluate Android-specific flaw classes; researchers emphasized that analysts must still validate findings and build proof-of-concept exploits because LLM output can overstate impact or produce false positives.
In OsmAnd, an exported MapActivity accepted attacker-controlled intent extras that could silently import and replace application settings. A permissionless malicious app could use the issue to redirect map-tile or routing traffic and potentially infer a victim's location, routes, origin, and destination. In Wikipedia for Android, researchers found two inadequate hostname-suffix checks that could be chained through a wikipedia:// deep link to load attacker-controlled content, expose Wikimedia cookies, and enable account takeover across Wikimedia projects.