
Loading story…
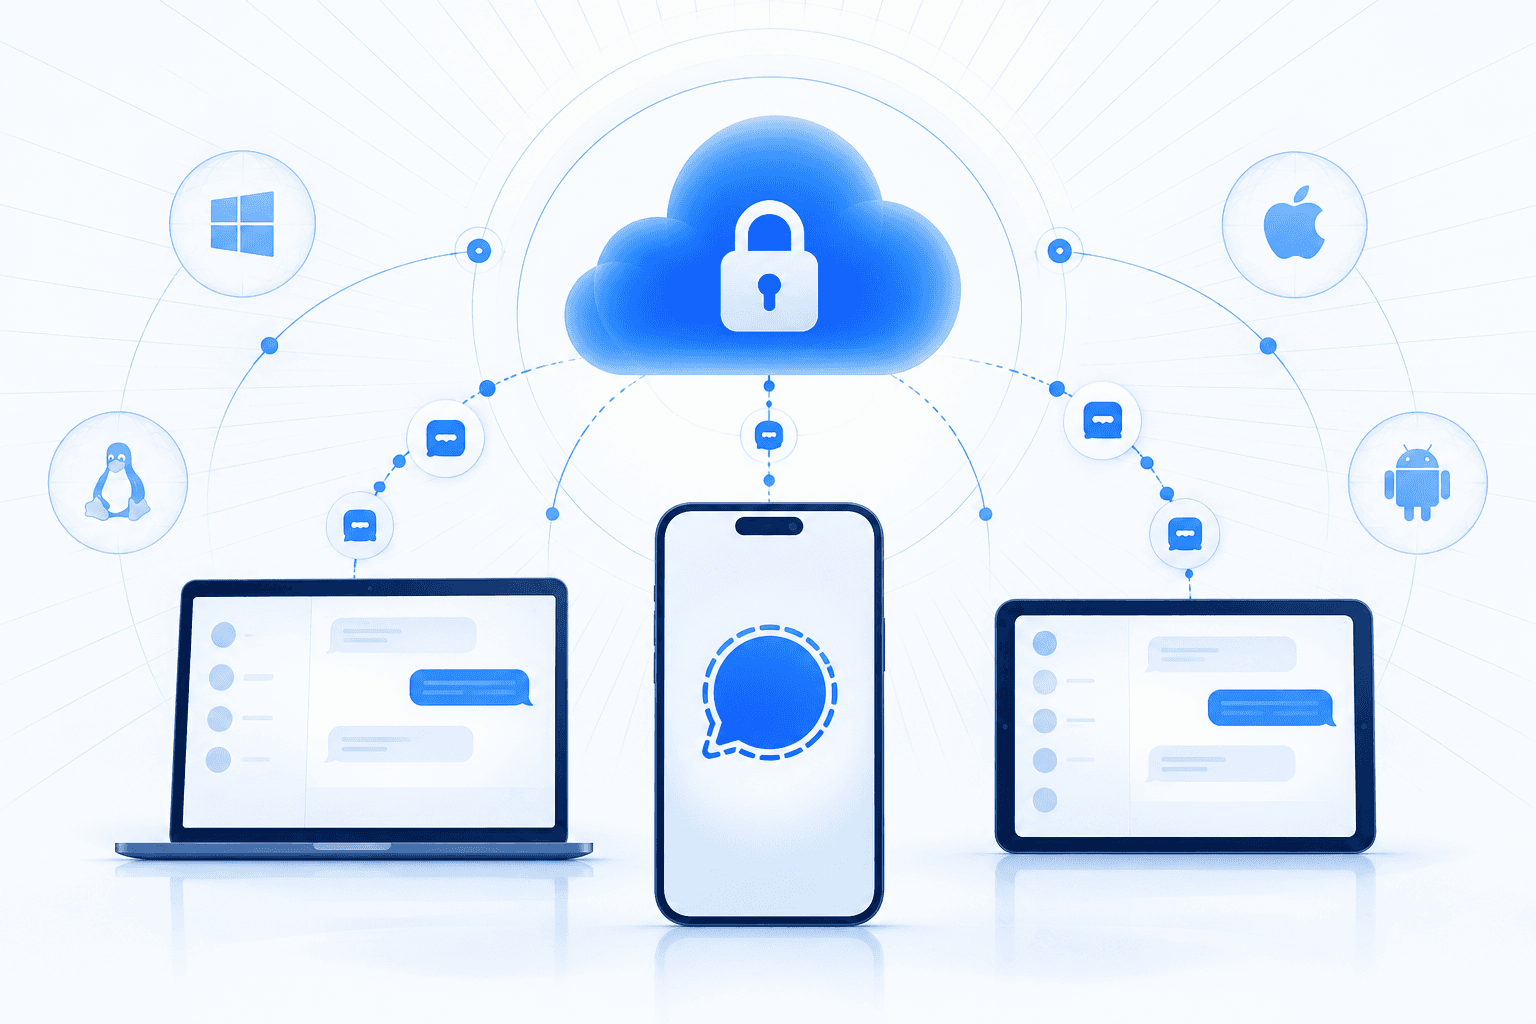
Signal completed a cross-platform rollout of encrypted backup enhancements with iOS version 8.30, adding on-device backups to iPhone and desktop clients on Linux, macOS, and Windows. Android now uses the same backup format, enabling restoration and migration of message history across Android, iOS, and desktop devices; encrypted local Wi-Fi transfers also streamline device migrations. Signal-hosted Secure Backups retain text and the latest 45 days of media for free, while a paid tier provides up to 100 GB of media storage. Disappearing messages set to expire within 24 hours are excluded from backups.
Both hosted and local backups are protected by recovery keys, but local backups rely solely on that key, which can decrypt every historical backup created with it. Signal said threat actors began targeting recovery keys following the feature’s initial release. Hosted backups add a daily rotating supplemental key retained in a Trusted Execution Environment. Separately, Signal introduced optional phone-number-free Android registration for a one-time US$3 fee, issuing users a 32-character account identifier and recovery key; users must create a username to remain discoverable without a phone number.
See affected versions and whether adversaries are exploiting it.
4 events from the most recent confirmed update back to the earliest known activity.
Signal released version 8.30, completing the first phase of its backup rollout across Android, iOS, Linux, macOS, and Windows. The release added on-device backups to iOS and desktop clients and moved Android to a unified cross-platform backup format.
Signal introduced its optional end-to-end encrypted Secure Backups service, providing hosted backup capability protected by recovery keys.
Signal stated that threat actors began targeting on-device backup recovery keys shortly after the backup feature's initial introduction. A local-backup recovery key can decrypt all previous backups encrypted with that key.
Signal introduced optional Android account registration without a phone number for a one-time US$3 fee intended to deter mass spam registrations. These accounts receive an account identifier and recovery key, and users are advised to create a username so others can find them.
Vulnerabilities, threat actors, malware, products, organizations, and breaches Mallory has linked to this story.
See whether adversaries are exploiting this yet, and where the affected versions run in your environment.
3 references tracked. Mallory keeps watching after this page renders.
helpnetsecurity.com
Open sourcebleepingcomputer.com
Open sourceheise.de
Open sourceMap indicators from this story to your assets and identify affected systems in minutes.
Every observed campaign, victim, and pivot linked to actors named in this story.
Malware, exploits, and IOCs connected to the activity described here.
YARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Get matching new stories delivered to your team as they break — not the next morning.
Ask questions about this story and take action on the answers.
Other stories Mallory is tracking that overlap on entities, sources, or topic labels.

Federal court reporting in Texas showed that the FBI recovered incoming **Signal** message content from an iPhone even after the app had been deleted and messages were set to disappear. The messages were cited as evidence in a case tied to the attack on the ICE Prairieland Detention Facility in Alvarado, where one police officer was shot; reporting identified defendant Lynette Sharp as having pleaded guilty to providing material support to terrorists. The recovered content reportedly came from iOS notification data stored on the device, not from any compromise of Signal’s end-to-end encryption. The exposure appears to stem from message previews cached by iOS when Signal notifications were displayed, allowing forensic tools used by law enforcement to extract at least some incoming message text while outgoing messages were not similarly recoverable. Privacy advocates including **EPIC** and the **EFF** called the issue a serious concern and urged users to limit notification exposure by changing Signal’s notification setting so previews show no sensitive content, such as **"No name or message"**.
Jun 29, 2026
Signal has added **Automatic Key Verification** to help users detect server-side key substitution and other man-in-the-middle risks in one-to-one chats. The feature uses **key transparency** so Signal clients can periodically confirm that the public keys tied to an account are globally consistent and actually belong to that user’s devices, warning users if verification fails. Trail of Bits said it built and operates one of three external auditors for the system, alongside Signal and Cloudflare, with each auditor maintaining a local Merkle-tree copy of the key map and signing consistent tree heads so clients can detect split-view behavior from a malicious server. The new mechanism complements Signal’s existing **safety number** protections rather than replacing them. Safety numbers remain unique to each one-to-one conversation and are used to manually verify end-to-end encryption, with Signal alerting users when a number changes—most often after a contact changes phones or reinstalls the app—and requiring approval before new messages are sent. Signal clients reportedly require recent signatures from all three auditors within seven days, limiting how long a compromised or malicious server could hide an inconsistent key view, and users are advised to fall back to manual safety number comparison if automatic verification does not succeed.
Aug 12, 2026
WhatsApp has announced the rollout of passkey-encrypted chat backups for both iOS and Android devices, allowing users to secure their stored message history using biometric authentication methods such as fingerprint, face recognition, or device screen-lock codes. This new feature leverages passwordless authentication standards like FIDO2/WebAuthn, replacing traditional backup passwords with cryptographic keys stored securely on the user's device. The update aims to simplify the backup security model and reduce risks associated with weak or forgotten passwords, as the device's biometric or lock code now serves as the primary gatekeeper for backup access. The introduction of passkey-encrypted backups reflects a broader industry shift toward passwordless authentication, with passkeys gaining traction among users seeking enhanced security and convenience. WhatsApp users can enable this feature by navigating to Settings > Chats > Chat backup > End-to-end encrypted backup, and the rollout is expected to reach all users over the coming months. This move builds on WhatsApp's previous implementation of end-to-end encrypted chat backups and further strengthens the privacy and security of user data stored on cloud services like iCloud and Google Drive.
Jul 12, 2026