
Loading story…
The Milk Dragon (also known as NaiLong) phishing-as-a-service kit has targeted online shoppers since October 2025 through counterfeit retail stores advertised via marketplace promotions and native social-media posts. Group-IB identified 258 phishing pages in 66 countries and 36 financial-institution verification templates tied to the operation.
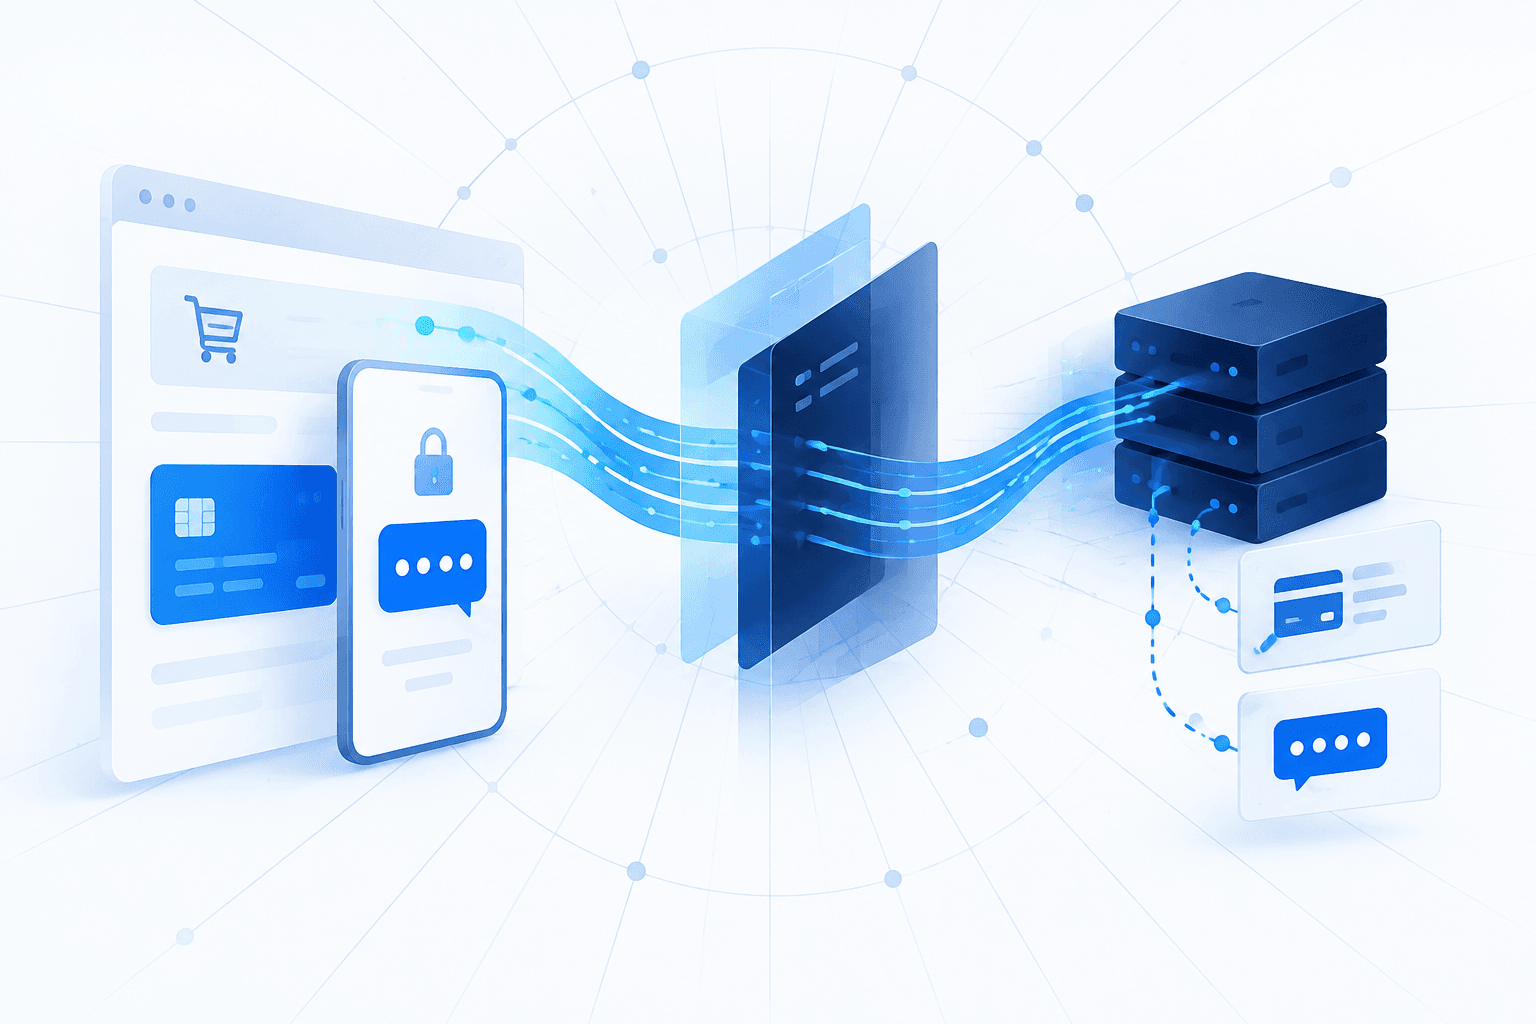
The kit deploys altered WordPress and WooCommerce sites using the malicious BytePress plugin, which opens a Socket.IO WebSocket connection to an operator-controlled panel. This provides real-time, character-by-character capture of payment data and operator control over checkout flows; counterfeit 3D Secure pages then capture and relay one-time passwords for fraudulent transaction authorization or account takeover. Milk Dragon is marketed through Telegram with subscriptions starting at 300 USDT per month, including infrastructure support and updates.
Get the infrastructure and lures behind it.
1 event from the most recent confirmed update back to the earliest known activity.
Milk Dragon, also known as NaiLong, began operating as a phishing-as-a-service kit targeting online shoppers with counterfeit retail offers promoted through marketplace advertisements and social-media posts.
Get the infrastructure, lures, and IOCs behind this campaign, ready to push into your email and identity stack.
2 references tracked. Mallory keeps watching after this page renders.
cryptika.com
Open sourcecybersecuritynews.com
Open sourceMap indicators from this story to your assets and identify affected systems in minutes.
Every observed campaign, victim, and pivot linked to actors named in this story.
Malware, exploits, and IOCs connected to the activity described here.
YARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Get matching new stories delivered to your team as they break — not the next morning.
Ask questions about this story and take action on the answers.
Other stories Mallory is tracking that overlap on entities, sources, or topic labels.
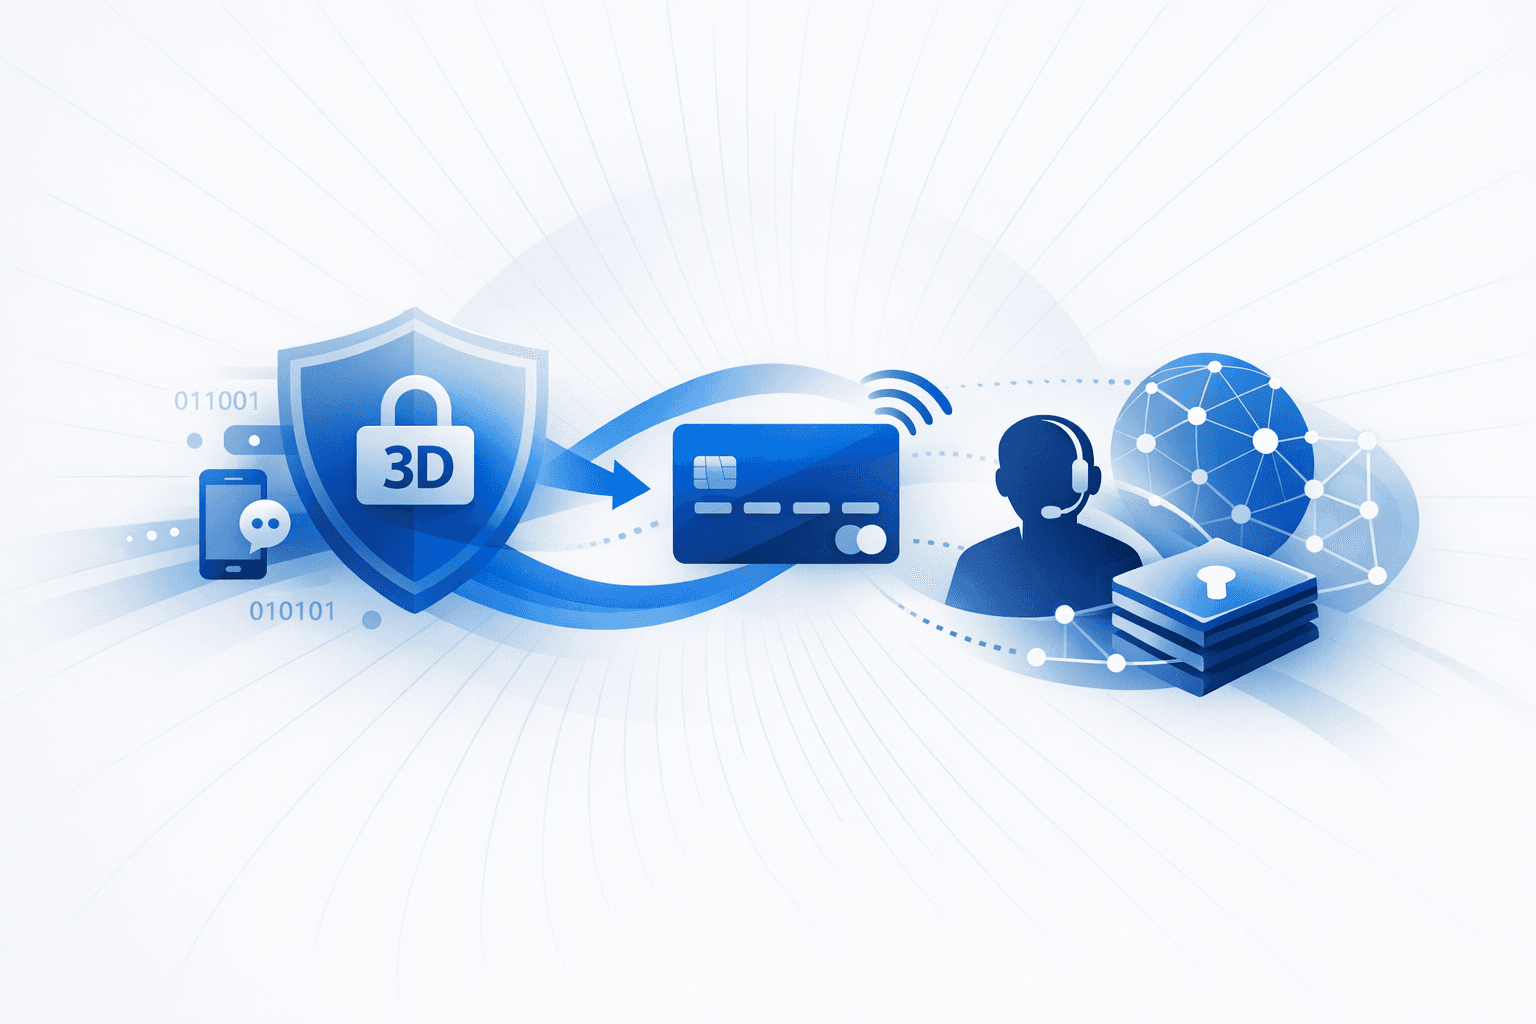
Researchers exposed two closely related smishing operations that impersonated parcel-delivery brands and used phishing kits with **live operator consoles** to steal identity and payment-card data. In one case, investigators tied a J&T Express lure to a short-lived domain, `jtexpress.mwkqbr[.]club`, and found a kit that harvested full identity details and card information before relaying victims into OTP, PIN, app, email, or CVV challenge screens. Static analysis showed AES-128-CBC encryption in browser storage and socket transport, a Socket.IO relay on the `/com/socket.io/` path, multiple client-side verification routes, and Chinese debug strings, while the infrastructure was registered through Dominet (HK) Limited and fronted by Cloudflare before being suspended days later. The findings mirror a broader investigation into **Darcula** and its `Magic Cat` phishing platform, which used smishing messages posing as postal and delivery services and streamed victim data in real time to an operator “admin” room. Researchers said the platform functioned as a mature phishing-as-a-service business with licensing, activation management, template distribution, real-time victim interaction, and possible backdoor capability, and linked it to Telegram communities and large-scale criminal monetization. The combined reporting indicates an industrialized ecosystem in which human operators actively guide victims through bank verification steps, allowing attackers to bypass 3D Secure protections and compromise hundreds of thousands of targets.
Aug 24, 2026
Phishing-as-a-service platforms continued to industrialize account takeover operations, with kits such as **Tycoon2FA**, **EvilProxy**, **Sneaky 2FA**, **CryptoChameleon**, **Darcula**, **Evilginx**, and **EvilTokens** enabling attackers to steal credentials, session cookies, MFA responses, payment-card data, and OAuth tokens at scale. Reporting across 2025 and 2026 described more than a million PhaaS attacks in a two-month period, a possible **CryptoChameleon** social-engineering campaign targeting LastPass and cryptocurrency users, and a targeted adversary-in-the-middle campaign against **RBC Express** online banking customers that used malvertising and cloaking to bypass multi-factor authentication. Researchers also documented a shift from fake login pages toward token theft and abuse of legitimate authentication workflows. A July 2026 analysis tied a bulk phishing platform dubbed **Mailer-Go Mission Control** to **EvilTokens** operations abusing Microsoft's OAuth device-code flow, while sector reporting said AiTM phishing had become the top initial access vector for law firms, with **Tycoon2FA** responsible for over half of AiTM-related compromises in that sector during 2025 despite a March 2026 disruption. The combined reporting warned that modern phishing kits lower the barrier to entry with automation, domain management, and real-time victim interaction, and recommended **phishing-resistant MFA** such as FIDO2/WebAuthn, conditional access, managed-device controls, and rapid revocation of compromised sessions and refresh tokens.
Aug 15, 2026
Barracuda researchers reported that the **LogoKit** phishing-as-a-service platform has evolved into a real-time deception system that builds a unique login page for each target. The kit extracts the victim’s email address from the URL, identifies the employer’s domain, and assembles branded content on demand, including a live screenshot of the organization’s legitimate website as the page background. Researchers said the shift moves phishing beyond simple brand spoofing toward **environment impersonation**, while the victim is often redirected to the real site after submitting credentials, reducing suspicion. The campaigns were observed in multiple languages, including English, German, French, Spanish, Chinese, and Korean, and rely heavily on legitimate cloud services such as **Thum.io, Clearbit, Google Favicon, ImageKit, and Microlink**. Stolen credentials are exfiltrated through **Telegram bots** rather than attacker-hosted infrastructure, making the operation easier to deploy and harder to disrupt or detect with traditional indicator- and template-based defenses. Barracuda recommended **phishing-resistant MFA** such as **FIDO2** security keys and passkeys, along with conditional access, browser isolation, provider and brand impersonation checks, and URL filtering for newly registered domains and links containing email addresses in the path.
Aug 11, 2026