Phishing Campaign Abuses Microsoft Power BI to Deploy Rogue ScreenConnect Clients
Social Engineering & Fraud · 6 sources · Updated 1mo ago · First seen Oct 7, 2026
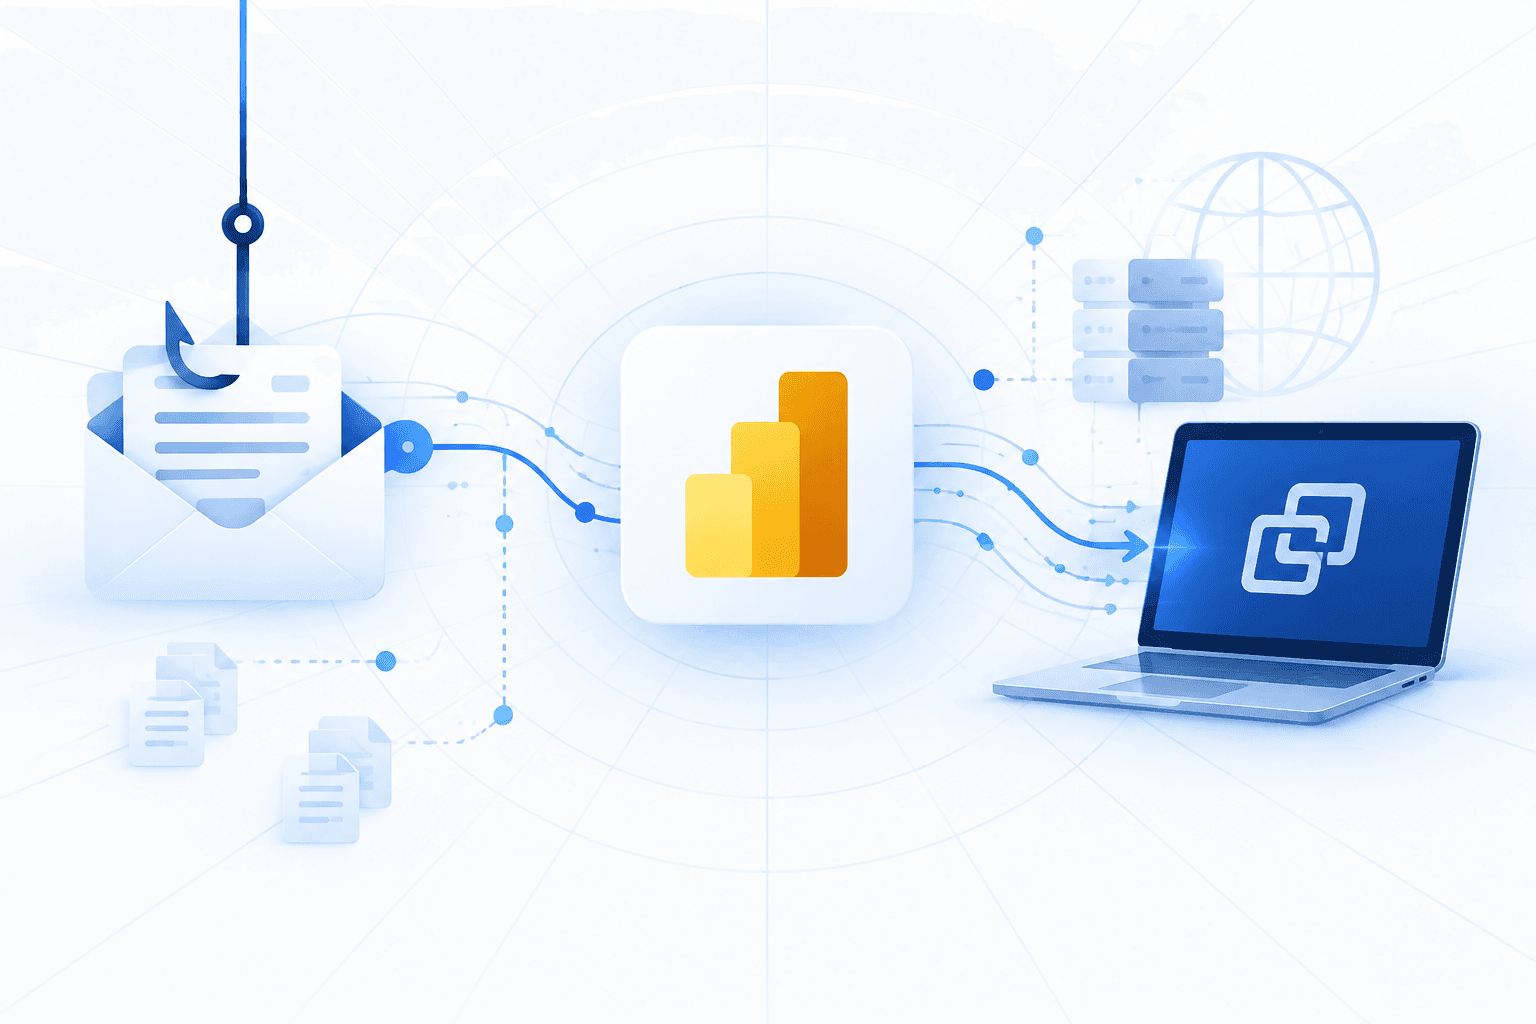
Attackers are using public Microsoft Power BI dashboards as phishing landing pages to distribute unauthorized ScreenConnect remote-access clients. Huntress first observed the campaign on September 10, 2026. Phishing emails direct recipients to a blurred document hosted on the legitimate app.powerbi.com domain, where a “Download Reference” link redirects them to attacker-controlled websites. Those sites fingerprint visitors, filter potential security scanners, send victim telemetry through a Telegram bot, and automatically download a ScreenConnect installer. Hosting the initial lure on a trusted Microsoft service can help the links bypass email controls that allow-list Power BI.
The attackers deployed a second ScreenConnect client to maintain access; one observed incident included replacement of the original client, a suspected defense-evasion executable identified as HideUL_x64.exe, and a scheduled task that reran a PowerShell installation script every two minutes. Retrospective hunting linked one ScreenConnect configuration to 22 additional endpoints across separate incidents, although that linkage does not independently establish that all belonged to this campaign. Huntress interrupted the observed attack and recommends monitoring for unauthorized remote-management installations, restricting ScreenConnect use to approved instances, and scrutinizing phishing links hosted on trusted cloud services.