Attackers Chain PaperCut Authentication Bypass and Critical RCE Against Education Sector
Active Exploitation · 5 sources · Updated 21d ago · First seen Aug 28, 2026
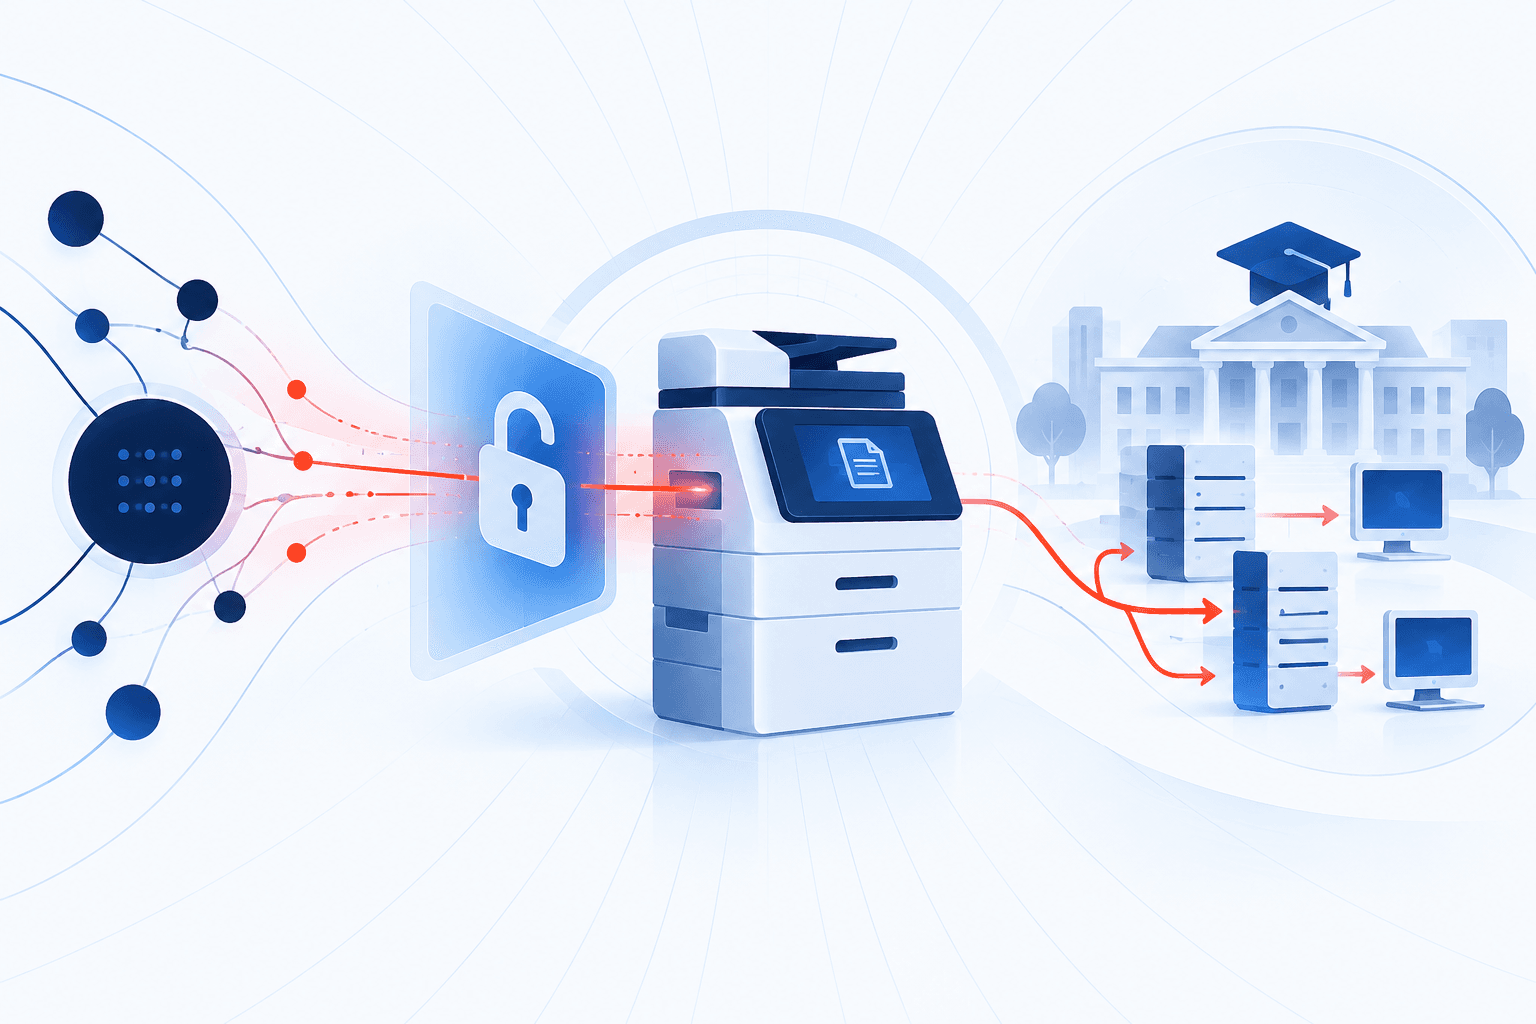
Attackers are chaining two actively exploited vulnerabilities in PaperCut NG/MF to execute commands, conduct reconnaissance, and facilitate credential theft. Arctic Wolf reported attacks against schools and universities in the United States and Europe, while PaperCut confirmed customer incidents and issued an urgent security advisory on August 27. CVE-2026-81578, an improper access control flaw rated CVSS v4.0 8.8, allows unauthenticated requests under specific conditions to trigger administrative actions before access validation completes and modify configuration settings. Attackers can combine it with CVE-2026-82078, rated 9.4, to exploit unsafe dynamic class loading in database connection utilities and execute arbitrary Java bytecode already on the application classpath under the PaperCut server process’s security context.
Both vulnerabilities are listed in the EU and CISA Known Exploited Vulnerabilities catalogs. Affected releases include versions earlier than 24.1.10, the 25.0 branch before 25.0.13, and the 26.0 branch before 26.0.5; organizations should prioritize upgrading affected servers to these fixed versions or later and investigate evidence of configuration tampering, command execution, and credential theft. A subsequent Metasploit release added a PaperCut NG/MF exploit module among 10 new exploit modules, expanding publicly available exploitation tooling. One supplied report recorded 559 exploitation attempts on a single sensor, but provided no collection period, limiting conclusions about attack volume.