PaperCut Server Exploitation Enables Ransomware, Cryptomining and Botnet Attacks
Active Exploitation · 2 sources · Updated 24d ago · First seen Jul 25, 2023
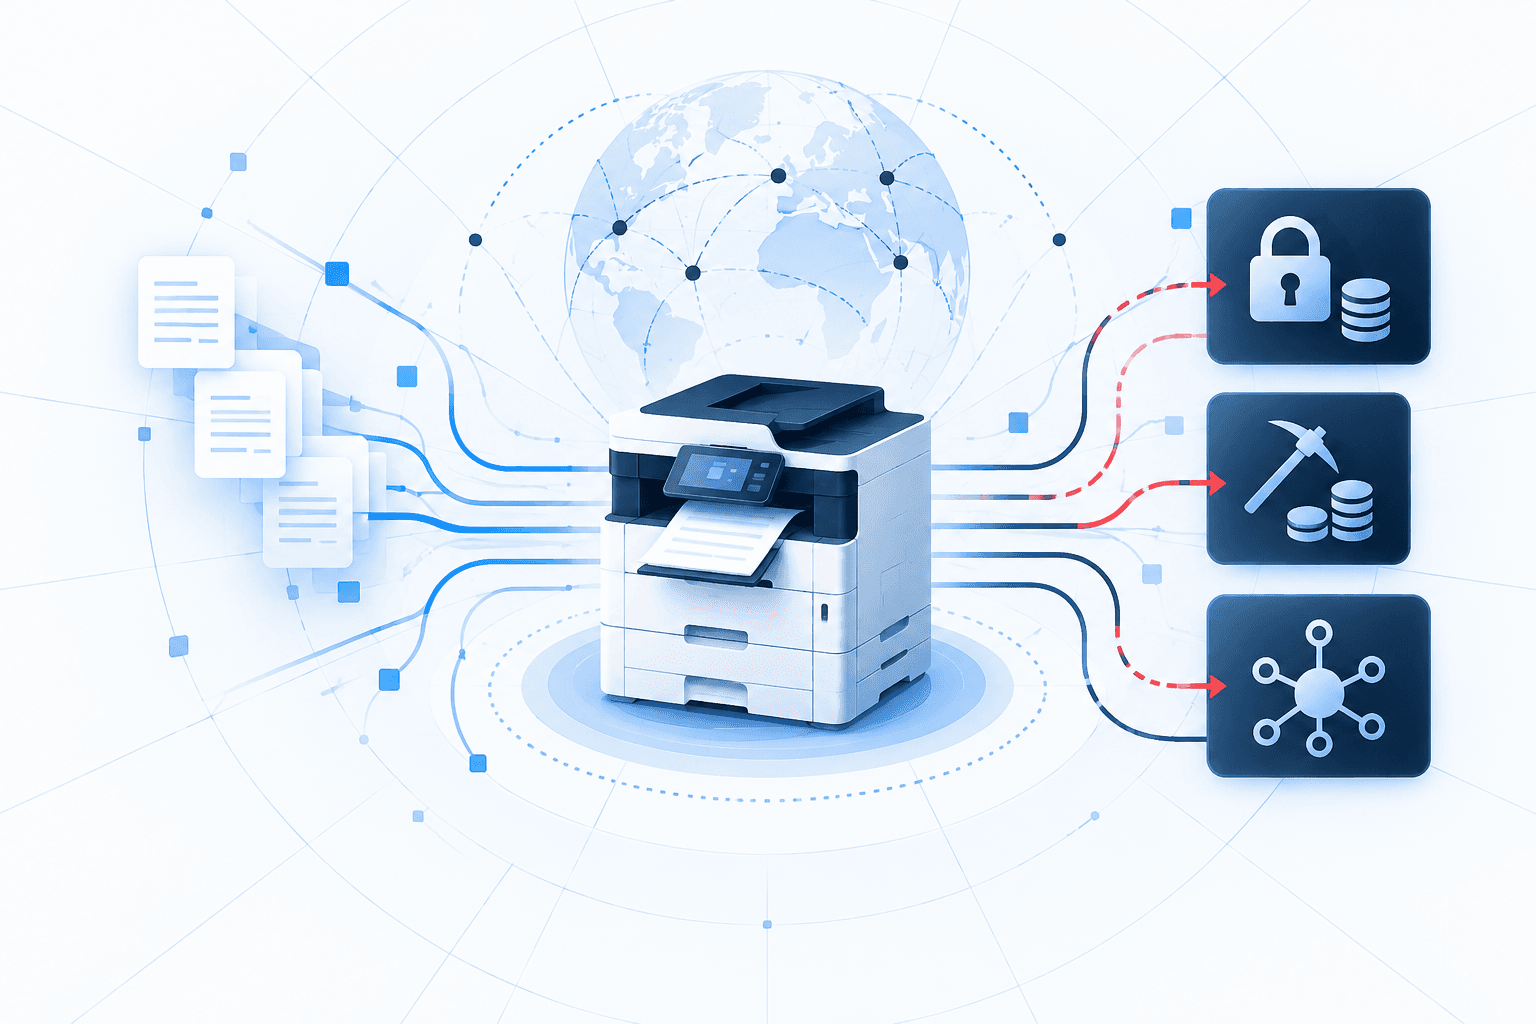
Multiple threat groups exploited CVE-2023-27350 in PaperCut NG and MF print-management servers to bypass authentication and execute code remotely, targeting organizations worldwide with a disproportionate concentration in education. Sophos observed attacks beginning April 13, 2023, after PaperCut released a patch on March 8. Post-exploitation activity included Cobalt Strike, abuse of remote-management tools, ransomware, cryptocurrency miners and botnet payloads, demonstrating the range of threats facing unpatched deployments.
PaperCut also published a July security bulletin, and Sophos’s August update highlighted CVE-2023-39143, a separate Windows-specific path traversal vulnerability affecting versions before 22.1.3 that permits arbitrary file reading and writing. Sophos had not observed exploitation of that flaw at the time of its report. Organizations should promptly apply vendor fixes, investigate suspicious child processes spawned by the PaperCut application process, pc-app.exe, and isolate servers showing signs of compromise rather than treating patching alone as remediation.