Mallory
← Back to News
botnet-infrastructureinternet-exposed-serviceactively-exploited-vulnerabilityinternet-facing-service-vulnerability

Satori Variant Hijacks Claymore Mining Wallets Through Exposed Management APIs

Active Exploitation · 3 sources · Updated 1mo ago · First seen Jan 16, 2018
Satori Variant Hijacks Claymore Mining Wallets Through Exposed Management APIs

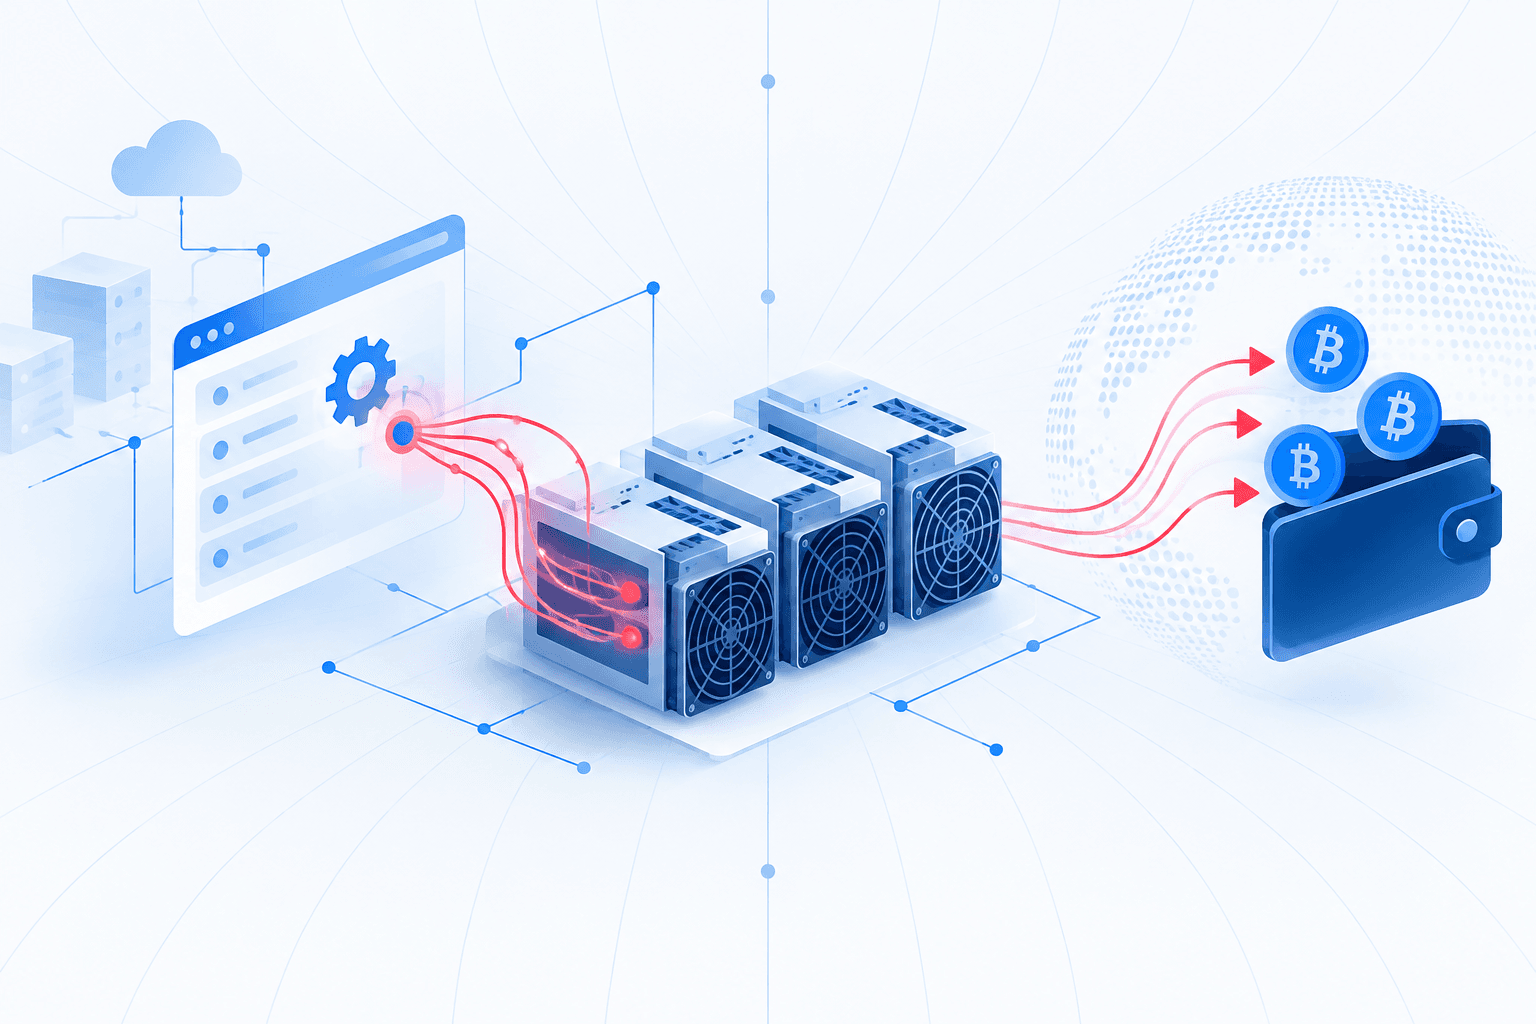
The Satori.Coin.Robber botnet variant targeted exposed Claymore Miner management interfaces to redirect Ethereum mining proceeds to an attacker-controlled wallet. Netlab researchers reported in January 2018 that the malware used unauthenticated access on TCP port 3333 to alter a reboot batch file, replace mining pool and wallet settings, and restart predominantly Windows mining hosts. Researchers observed approximately 4,900 unique scanning source IPs; the attacker’s mining account reportedly averaged 1,606 MH/s over two days and accumulated 0.1733 ETH in the preceding 24 hours. Separately, SANS reported increased port-3333 scanning in May 2018 and honeypot requests consistent with exploitation of CVE-2018-1000049, using Claymore’s JSON-RPC API to upload a reboot script and trigger its execution. That payload configured mining through Dwarfpool with a specified wallet.

The Satori variant also retained exploitation of CVE-2017-17215 on port 37215 and CVE-2014-8361 on port 52869, alongside asynchronous scanning and DNS-based command-and-control communication. CVE-2014-8361 permits remote code execution through a crafted NewInternalClient request to the Realtek SDK’s miniigd SOAP service; its CVE record reports exploitation in the wild through 2023 but provides no affected-version or remediation details. Operators should restrict Claymore management interfaces to trusted networks, verify mining pool and payout-wallet settings, and investigate unexpected reboot-script changes. Configuring Claymore with a negative management-port value enables read-only mode, disabling its most dangerous management functions.
This is being exploited nowSee which actors are running it and whether you're in range.
Check your exposure
Event timeline

How this story unfolded

Events from the most recent confirmed update back to the earliest known activity.

8 events · May 1, 2015 – Feb 2018
  1. Reported May 18, 20189y ago

    SANS honeypot detects Claymore exploitation amid increased port 3333 scanning

    A SANS honeypot observed increased JSON-RPC requests consistent with exploitation of CVE-2018-1000049 alongside increased TCP port 3333 scanning. The requests uploaded a reboot.bat command configuring EthDcrMiner64.exe to mine through Dwarfpool using wallet 0xd0897da92bd7d7754f4ea18f8169dbc08beb8df7, then issued miner_reboot.

    Insecure Claymore Miner Management API Exploited in the Wild
  2. Feb 2018

    Claymore Dual Miner remote code execution vulnerability disclosed

    CVE-2018-1000049 was disclosed in February 2018. The vulnerable JSON-RPC management interface allows attackers to upload a reboot.bat script and execute it through a subsequent miner_reboot request.

    Insecure Claymore Miner Management API Exploited in the Wild
  3. Reported Jan 17, 20189y ago

    Security community sinkholes Satori command-and-control infrastructure

    Following a December 5 report, the security community sinkholed Satori's command-and-control infrastructure, temporarily halting the botnet's spread.

    Art of Steal: Satori Variant is Robbing ETH BitCoin by Replacing Wallet Address
  4. Jan 16, 20189y ago

    Researchers document mining activity associated with the attacker's wallet

    At 17:00 GMT+8 on January 16, researchers observed that the attacker's mining account averaged 1,606 MH/s over two days and accumulated 0.1733 ETH over the preceding 24 hours. The account also showed another 0.76 ETH in its balance.

    Art of Steal: Satori Variant is Robbing ETH BitCoin by Replacing Wallet Address
  5. Jan 8, 20189y ago

    Satori.Coin.Robber begins rebuilding the botnet and hijacking mining proceeds

    Researchers first observed renewed botnet activity at 10:42:06 GMT+8 on January 8, 2018. The variant targeted exposed Claymore management interfaces on port 3333 to rewrite reboot.bat, substitute an attacker-controlled Ethereum wallet, and restart miners, while retaining exploitation of Huawei and Realtek vulnerabilities.

    Art of Steal: Satori Variant is Robbing ETH BitCoin by Replacing Wallet Address
  6. Nov 2017

    Claymore Miner arbitrary file access vulnerability disclosed with exploit code

    CVE-2017-16929 was publicly disclosed with exploit code, exposing remote arbitrary file reading and writing in Claymore Miner. Researchers distinguished this exploit from the unauthenticated management functionality later abused by Satori.Coin.Robber.

    Art of Steal: Satori Variant is Robbing ETH BitCoin by Replacing Wallet Address
  7. 2016

    Proof-of-concept exploit becomes public for CVE-2014-8361

    Proof-of-concept exploit code for the Realtek SDK vulnerability became publicly available. Satori.Coin.Robber later exploited this flaw against devices on port 52869.

    Art of Steal: Satori Variant is Robbing ETH BitCoin by Replacing Wallet Address
  8. May 1, 201512y ago

    MITRE publishes CVE-2014-8361 for Realtek SDK remote code execution

    MITRE published the CVE record for a vulnerability in the Realtek SDK's miniigd SOAP service. A crafted NewInternalClient request allows remote attackers to execute arbitrary code.

    CVE Record: CVE-2014-8361
Linked entities

Related entities

Vulnerabilities, threat actors, malware, products, organizations, breaches, and observables Mallory has linked to this story. Indicator values are masked here and available in full in the app.

Open in app →

Malware

1 linked

Observables

14 linked

Indicator values are masked on this page. View all 14 in Mallory Domains, IPs, hashes, and URLs are exportable to your SIEM.

Do you run this?Correlate live exploitation activity against the software you actually run, and see where you're exposed.
See Who's Exploiting This
Mallory platform

See the full picture, correlated to your attack surface.

This page covers what’s public. Mallory adds the parts that aren’t: which of your assets are affected, which threat actors are using it right now, and what to deploy next.

Exposure mappingMap indicators from this story to your assets and identify affected systems in minutes.
Threat actor evidenceEvery observed campaign, victim, and pivot linked to actors named in this story.
Associated malwareMalware, exploits, and IOCs connected to the activity described here.
Detection signaturesYARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Scheduled alertsGet matching new stories delivered to your team as they break, not the next morning.
AI threadsAsk questions about this story and take action on the answers.