Mallory
← Back to News
defense-evasion-methodinternet-exposed-servicepersistence-methodcommand-and-control-method

SANSAR Cryptomining Toolkit Compromises Linux GPU Hosts and Fakes 0% Utilization

Attack Tradecraft · 14 sources · Updated 6h ago · First seen Nov 13, 2026
SANSAR Cryptomining Toolkit Compromises Linux GPU Hosts and Fakes 0% Utilization

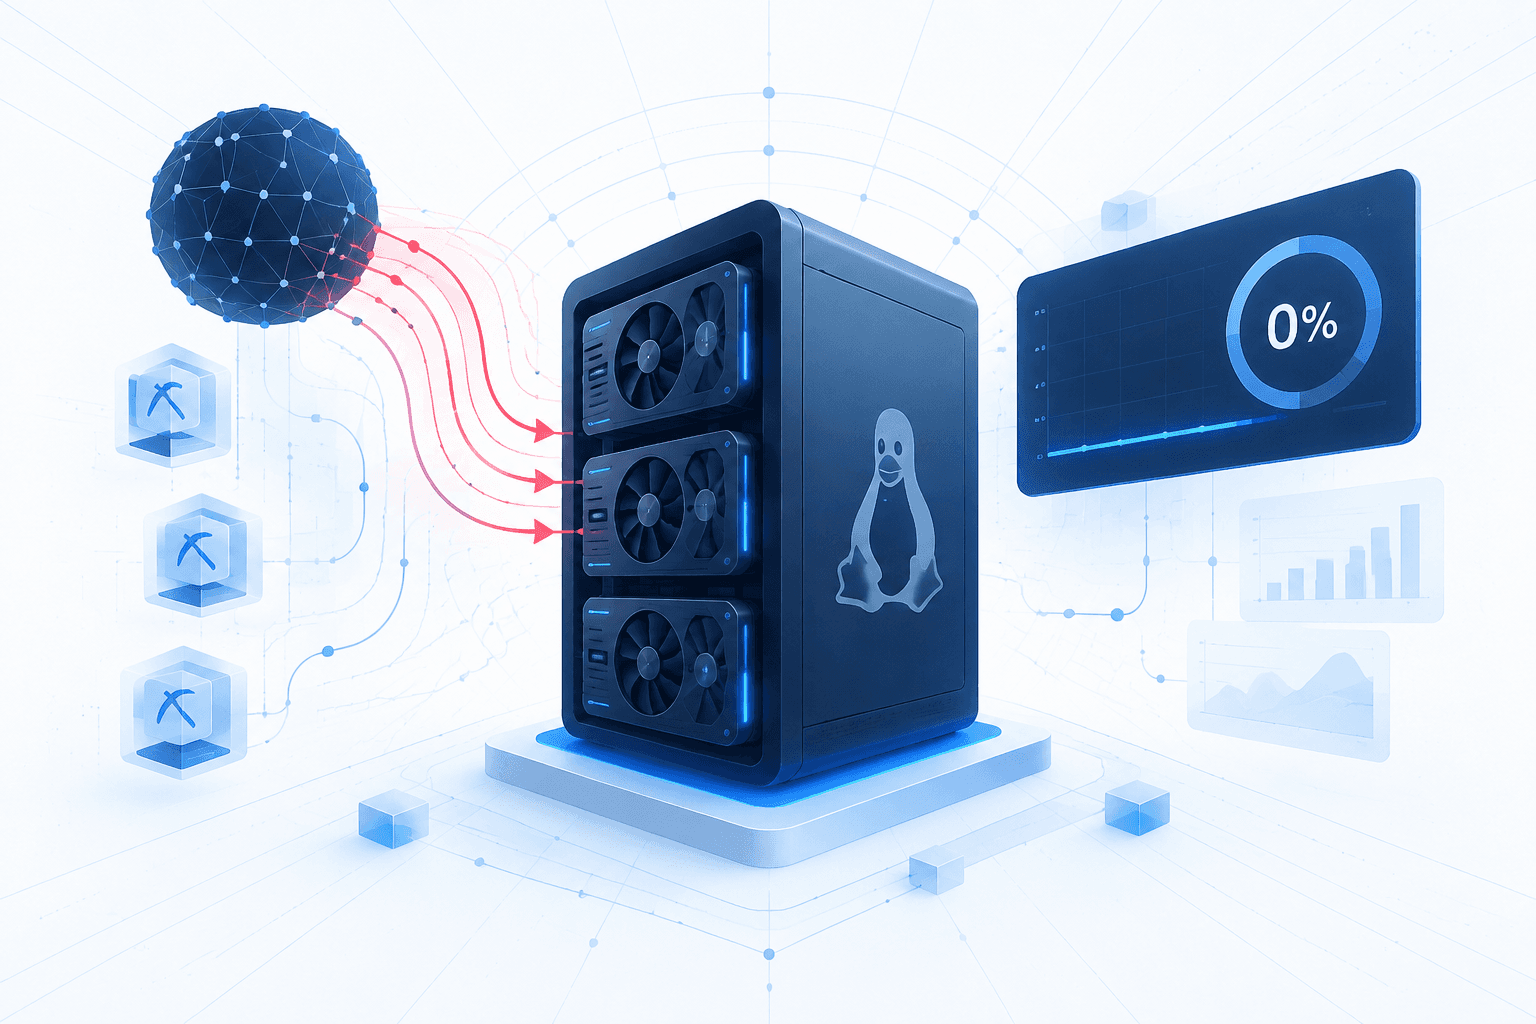
Attackers compromised three Linux GPU hosts through an internet-exposed Ray job agent that accepted unauthenticated job submissions, deploying a cryptomining toolkit centered on the Rust-based SANSAR orchestrator. Elastic Security Labs tracked the intrusion as REF3364, observing activity from October 22–25, 2026. The attackers inventoried GPUs, launched a Python reverse shell, and deployed XMRig and SRBMiner-MULTI miners alongside a kernel rootkit. A modified NVIDIA Management Library (NVML) wrapper concealed mining activity by reporting 0% GPU utilization and fabricated temperature and power readings.

The attackers maintained access through an SSH key and an early-boot loader. SANSAR used Tor for remote control, while a separate backdoor, netns, retrieved its command-and-control address from an Ethereum smart contract. Elastic did not establish how the attackers obtained root privileges, and the reporting identifies neither a threat actor nor a specific CVE. Defenders should restrict access to Ray job submission interfaces, verify GPU monitoring library integrity, and investigate SSH persistence, boot-time loaders, and kernel-level concealment rather than trusting reported GPU utilization alone; supplied indicators require validation before operational use.
Who uses this technique?Get the actors, campaigns, and ATT&CK mapping behind it.
Get the tradecraft
Event timeline

How this story unfolded

Events from the most recent confirmed update back to the earliest known activity.

6 events · Oct 22, 2026 – Nov 12, 2026
  1. Reported Nov 12, 20265d ago

    Attacker installs SANSAR mining toolkit, rootkit, and early-boot loader

    After obtaining root privileges through an unexplained method, the attacker deployed the toolkit under /opt/vadi_/, built its kernel module using DKMS, and installed an early-boot loader. The toolkit combined SANSAR, CPU and GPU miners, a GPU telemetry-falsification wrapper, a kernel rootkit, and the netns backdoor.

    SANSAR : orchestrateur de cryptominage Linux furtif combinant Tor, rootkit et C2 via Ethereum | CyberVeille
  2. Reported Nov 12, 20265d ago

    Attacker adds an SSH key for persistent access

    After establishing the reverse shell, the attacker added an SSH key to authorized_keys to maintain access.

    SANSAR : orchestrateur de cryptominage Linux furtif combinant Tor, rootkit et C2 via Ethereum | CyberVeille
  3. Nov 12, 20266d ago

    Elastic publishes technical analysis of the REF3364 intrusion

    Elastic Security Labs published its analysis of REF3364, documenting SANSAR's Tor-based control, GPU telemetry falsification, kernel-level concealment, and netns controller discovery through an Ethereum smart contract. The analysis provided detection material and indicators without identifying a threat actor or explaining how root privileges were obtained.

    SANSAR : orchestrateur de cryptominage Linux furtif combinant Tor, rootkit et C2 via Ethereum | CyberVeille
  4. Oct 25, 202624d ago

    Python reverse-shell job establishes remote access

    The attacker submitted a Python reverse-shell job through the exposed Ray agent, connecting to an external listener. The shell initially ran under the account owning the Ray session.

    SANSAR : orchestrateur de cryptominage Linux furtif combinant Tor, rootkit et C2 via Ethereum | CyberVeille
  5. Oct 24, 202625d ago

    Attacker inventories GPUs through an unauthenticated Ray job

    The attacker submitted a Ray job that executed nvidia-smi and exfiltrated the GPU inventory.

    SANSAR : orchestrateur de cryptominage Linux furtif combinant Tor, rootkit et C2 via Ethereum | CyberVeille
  6. Oct 22, 202627d ago

    External probes target the exposed Ray job agent

    Ray logs recorded external probes against an internet-accessible job agent that accepted unauthenticated submissions. The intrusion ultimately affected three Linux GPU hosts.

    SANSAR : orchestrateur de cryptominage Linux furtif combinant Tor, rootkit et C2 via Ethereum | CyberVeille
Linked entities

Related entities

Vulnerabilities, threat actors, malware, products, organizations, breaches, and observables Mallory has linked to this story. Indicator values are masked here and available in full in the app.

Open in app →

Threat actors

1 linked

Malware

1 linked

Affected products

1 linked
Ray

Observables

11 linked

Indicator values are masked on this page. View all 11 in Mallory Domains, IPs, hashes, and URLs are exportable to your SIEM.

Do you run this?Get the adversaries, campaigns, and ATT&CK mapping behind this technique, with detections ready to deploy.
See Who Uses This Technique
Mallory platform

See the full picture, correlated to your attack surface.

This page covers what’s public. Mallory adds the parts that aren’t: which of your assets are affected, which threat actors are using it right now, and what to deploy next.

Exposure mappingMap indicators from this story to your assets and identify affected systems in minutes.
Threat actor evidenceEvery observed campaign, victim, and pivot linked to actors named in this story.
Associated malwareMalware, exploits, and IOCs connected to the activity described here.
Detection signaturesYARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Scheduled alertsGet matching new stories delivered to your team as they break, not the next morning.
AI threadsAsk questions about this story and take action on the answers.