Attackers Exploit Patched FortiClient EMS SQL Injection Flaw Across Multiple Regions
Active Exploitation · 1 source · Updated 1mo ago · First seen Oct 23, 2024
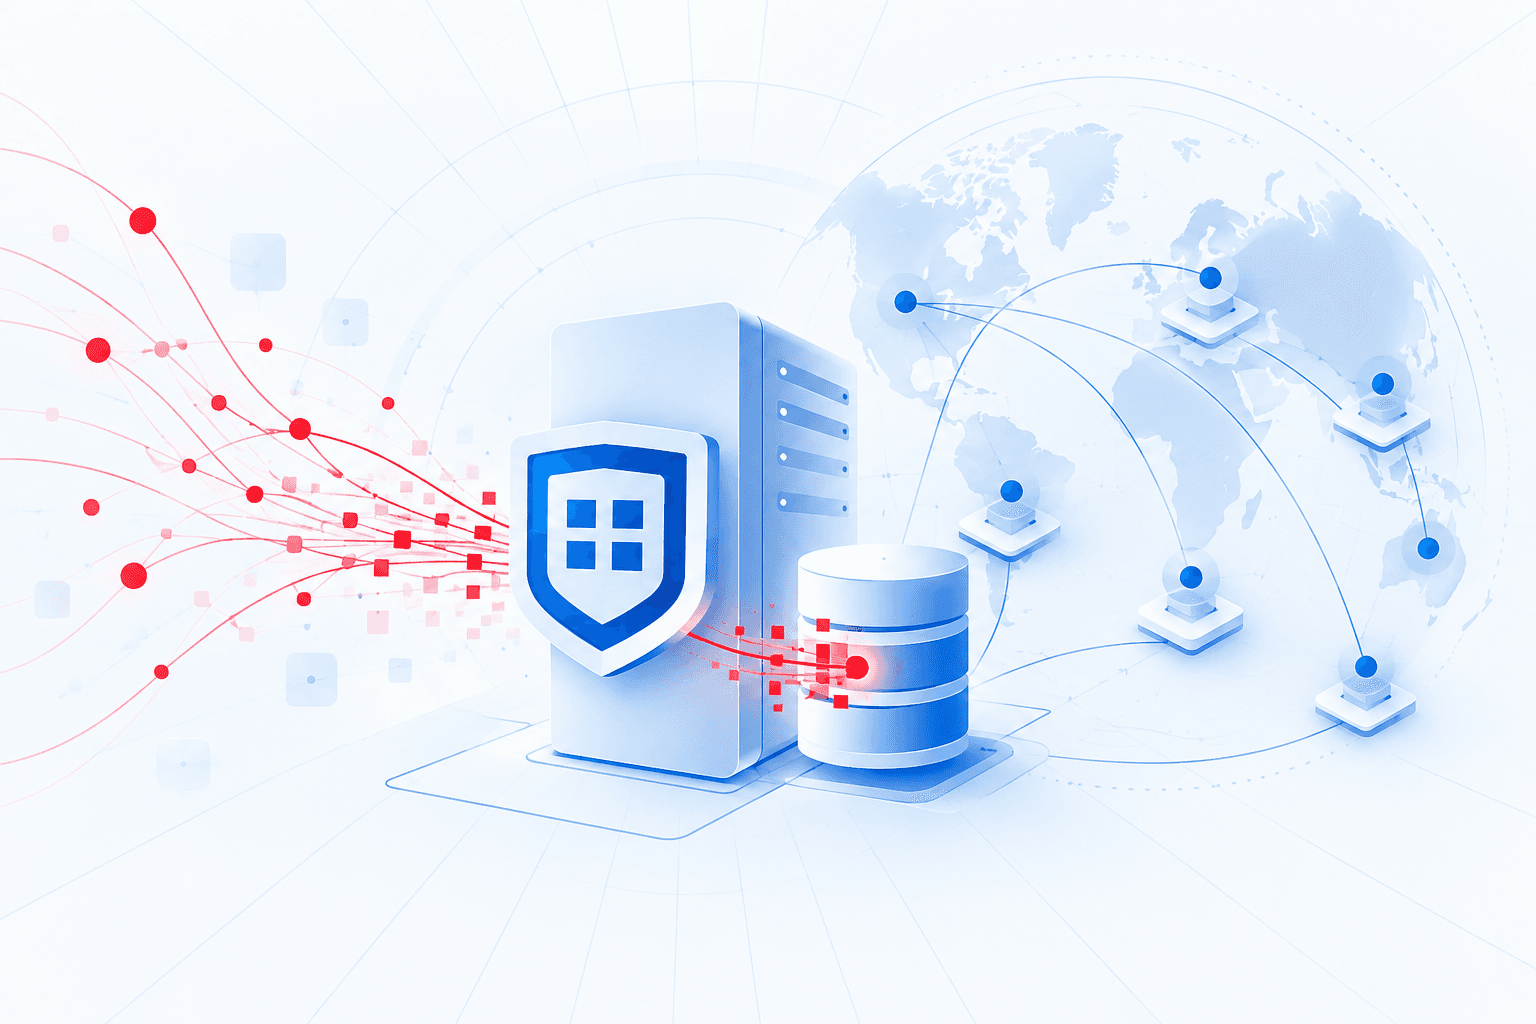
Attackers exploited CVE-2023-48788, an already-patched SQL injection vulnerability in Fortinet FortiClient EMS, to compromise an internet-facing server in an October 2024 intrusion investigated by Kaspersky’s Global Emergency Response Team. They installed ScreenConnect and AnyDesk, deployed credential-theft and network-discovery tools, attempted lateral movement, and interfered with security applications. Monitoring on neighboring systems enabled timely detection and containment.
Additional telemetry showed exploitation targeting multiple organizations and regions, potentially involving several threat actors using different second-stage payloads. On October 23, researchers observed attackers using webhook.site callbacks to identify vulnerable systems, with requests received from 22 distinct target IP addresses across 18 countries. Organizations should prioritize patching exposed FortiClient EMS installations and extend monitoring beyond the management server to detect unauthorized remote-access tools, credential theft, and lateral movement.