REvil Exploits Kaseya VSA Zero-Day to Spread Ransomware Through MSPs
Active Exploitation · 5 sources · Updated 1mo ago · First seen Jul 9, 2021
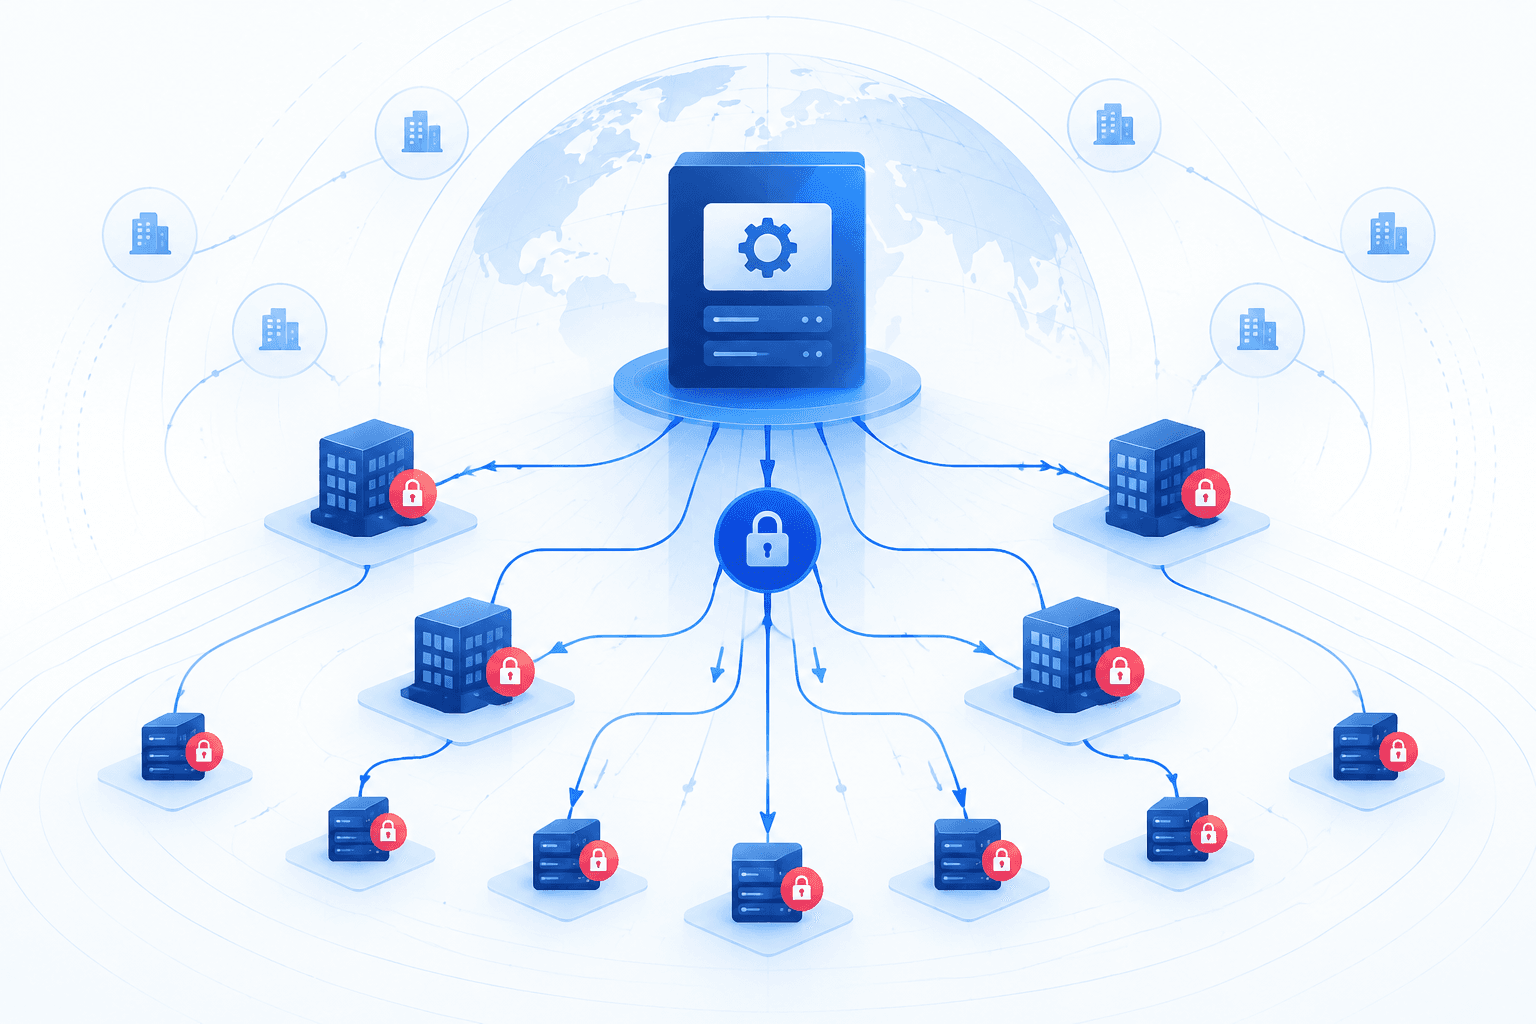
REvil ransomware operators compromised on-premises Kaseya Virtual System Administrator (VSA) servers on July 2, 2021, using managed service providers (MSPs) to deploy ransomware to downstream organizations. Kaseya reported at least 60 customers and 1,500 downstream businesses affected. Investigators identified an attack chain involving authentication bypass, payload upload, and code injection; DIVD confirmed exploitation of CVE-2021-30116. The critical vulnerability, rated CVSS 10.0 and affecting VSA versions before 9.5.7, exposed agent credentials that could be exchanged for a session cookie, allowing access to services not intended for agents and supporting further authentication bypass.
REvil demanded $70 million in Bitcoin for a universal decryptor and claimed more than one million infected systems, a figure not independently verified in the reporting. Unlike typical REvil campaigns, investigators reported no data exfiltration and disabled command-and-control communications. Kaseya advised customers to shut down VSA servers and released a detection tool, while CISA and the FBI issued MSP guidance. Kaseya subsequently released VSA 9.5.7a to address three outstanding vulnerabilities, patched its SaaS platform before restoring service, and announced on July 22 that it had obtained a universal decryptor from a trusted third party for affected customers. The incident highlights the need to patch remote-management platforms and assess downstream exposure through MSP access.