3102 Trojan Targets U.S. Government and European Media Through Excel Spear-Phishing
Active Exploitation · 1 source · Updated 1mo ago · First seen May 11, 2015
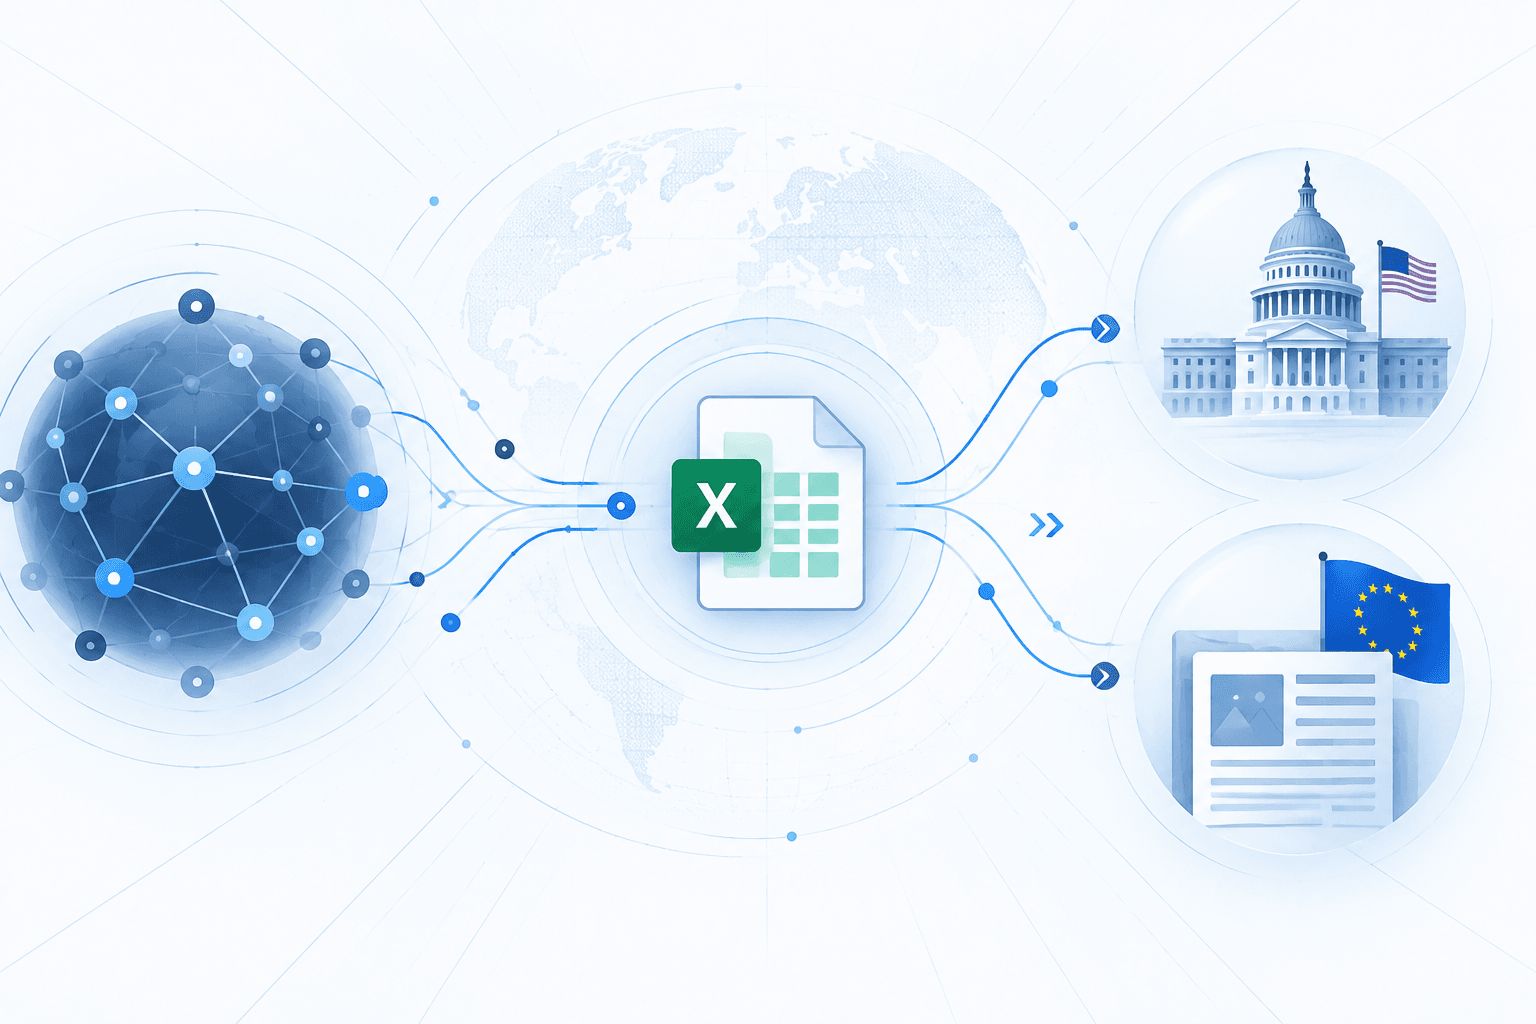
Unit 42 identified spear-phishing attacks against the U.S. government and a European media company in May 2015 that used the same malicious Excel document to deploy 3102, a modular variant of the 9002 Trojan. The document exploited CVE-2012-0158, triggering a multistage installation process that established persistence and stored the Trojan’s configuration separately in the Windows registry to hinder analysis. Embedded and remotely delivered plugins supported keylogging, file manipulation, screen capture, and interactive control.
Shared signing certificates and command-and-control infrastructure linked the campaigns to an Evilgrab watering-hole attack on the President of Myanmar’s website, although attribution to a common operator remained unconfirmed. Historical domain-registration records connected the infrastructure to Chinese hacking communities, prompting researchers to assess that the operators were likely China-based and possibly contractors. The attacks underscore the importance of remediating legacy Office vulnerabilities and monitoring for suspicious Office-triggered execution, registry-based configuration storage, and modular malware activity.