ErrTraffic Uses Compromised WordPress Sites and Blockchain Infrastructure to Deliver Malware
Threat Actor Intelligence · 2 sources · Updated 17d ago · First seen Aug 10, 2026
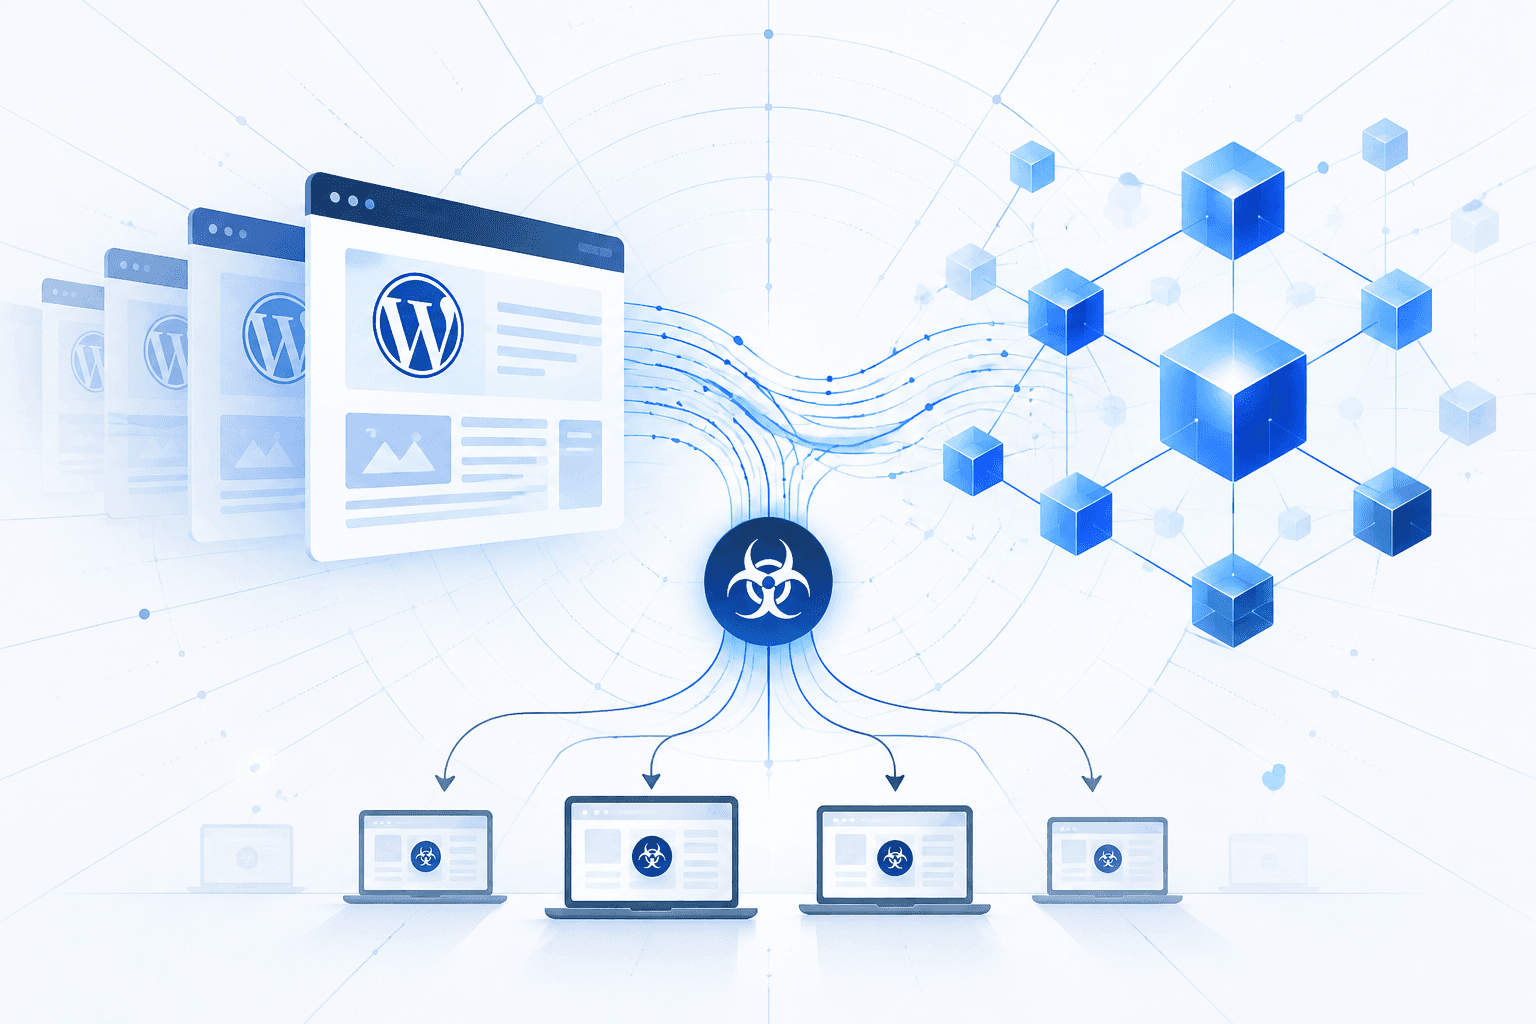
An active malware campaign uses the ErrTraffic Malware-as-a-Service framework to distribute malicious payloads through compromised WordPress websites and ClickFix social engineering, according to WatchGuard Threat Lab. The framework combines traffic distribution with EtherHiding, querying Polygon smart contracts to dynamically resolve malicious infrastructure instead of hardcoding destinations in injected JavaScript. Observed delivery chains included Vidar, Okobot, a Node.js backdoor, OnionDrop-related variants, LegionLoader-associated activity, and BabaDedaLoader. Malwarebytes separately reported hacked websites delivering the Vidar infostealer to Windows users, highlighting the overlapping threat from compromised web content.
The observed payloads used DLL side-loading, browser process injection, anti-analysis checks, reflective loading, and modifications to security controls to support theft and evade detection. The campaign also abused legitimate applications and Windows utilities, making individual malware indicators insufficient for reliable detection. Defenders should correlate browser, endpoint, and network activity, investigate suspicious execution following website visits, and reinforce user awareness of ClickFix lures that persuade visitors to perform purported troubleshooting steps.