Phishing Campaigns Abuse GitHub and GitLab, With Malware Hosted on GitHub
Social Engineering & Fraud · 2 sources · Updated 1mo ago · First seen Oct 13, 2026
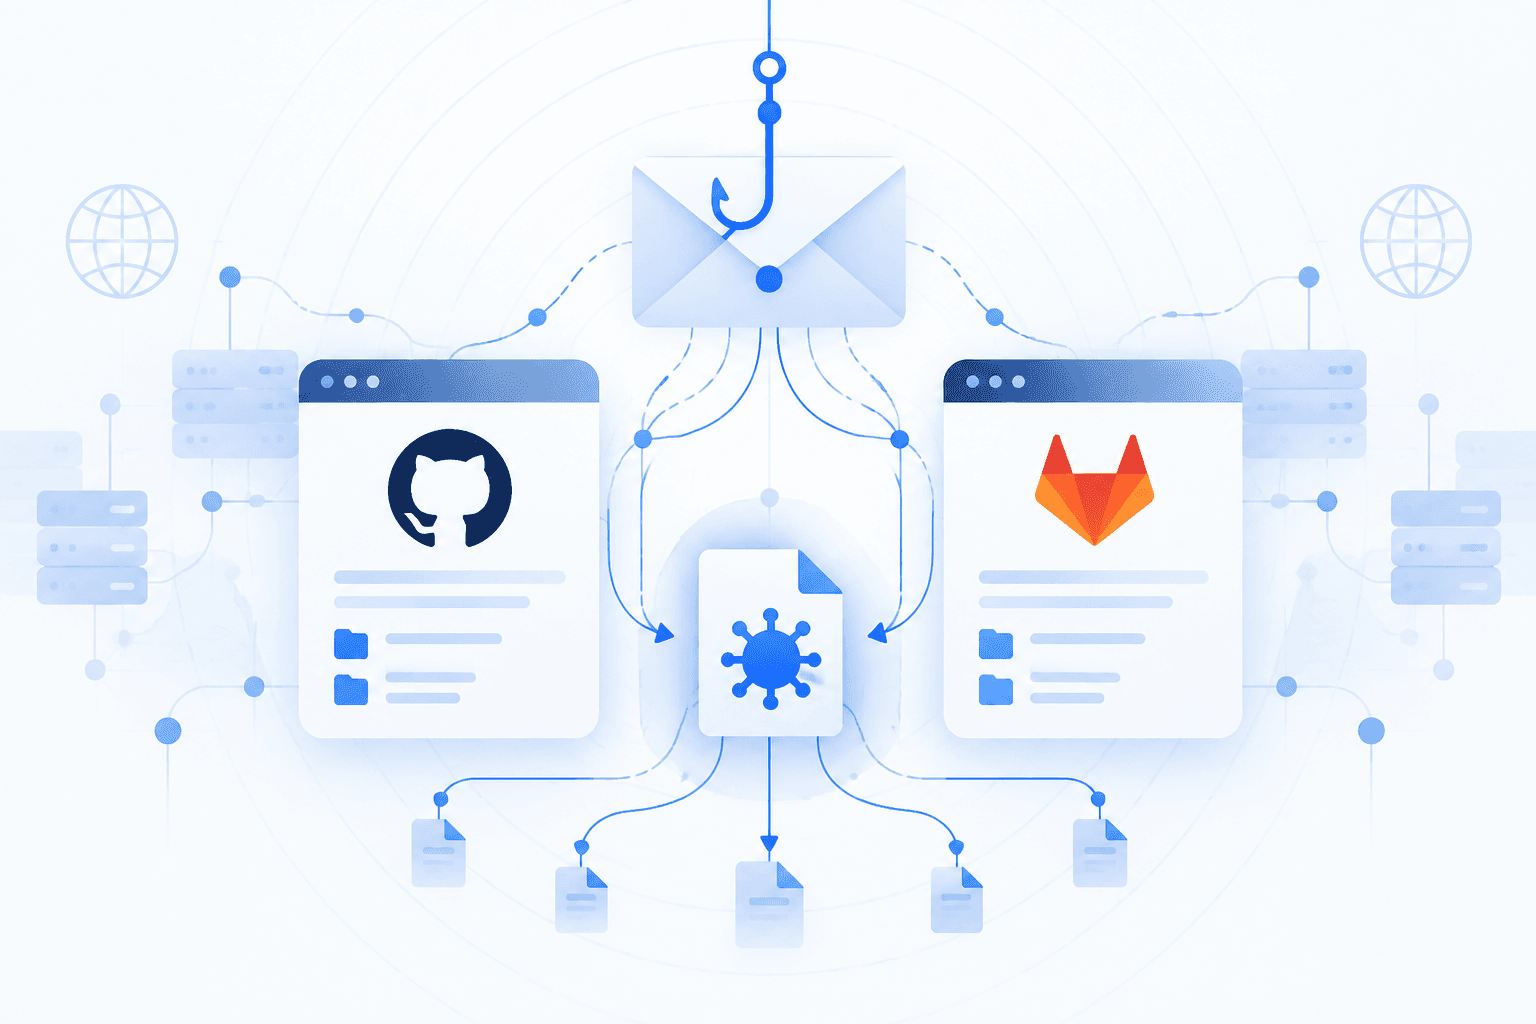
Phishing campaigns are abusing GitHub and GitLab, with GitHub-hosted malware illustrating how links to legitimate development platforms can lead users to malicious content. The activity exploits the distinction between a trusted hosting service and the attacker-controlled material it hosts: a familiar platform domain does not establish that a linked repository, file, or download is safe.
For defenders, the key exposure is trust placed in development-platform links arriving through email. Security teams should avoid blanket allowlisting of GitHub and GitLab, inspect linked content and subsequent downloads, and correlate suspicious email activity with endpoint execution. Controls should preserve legitimate developer access while detecting malicious use of these platforms.