ClickFix Intrusion Deploys Lorem Ipsum Loader and Python Tunnel Ahead of Suspected Ransomware
Malware Intelligence · 2 sources · Updated 10d ago · First seen Oct 14, 2026
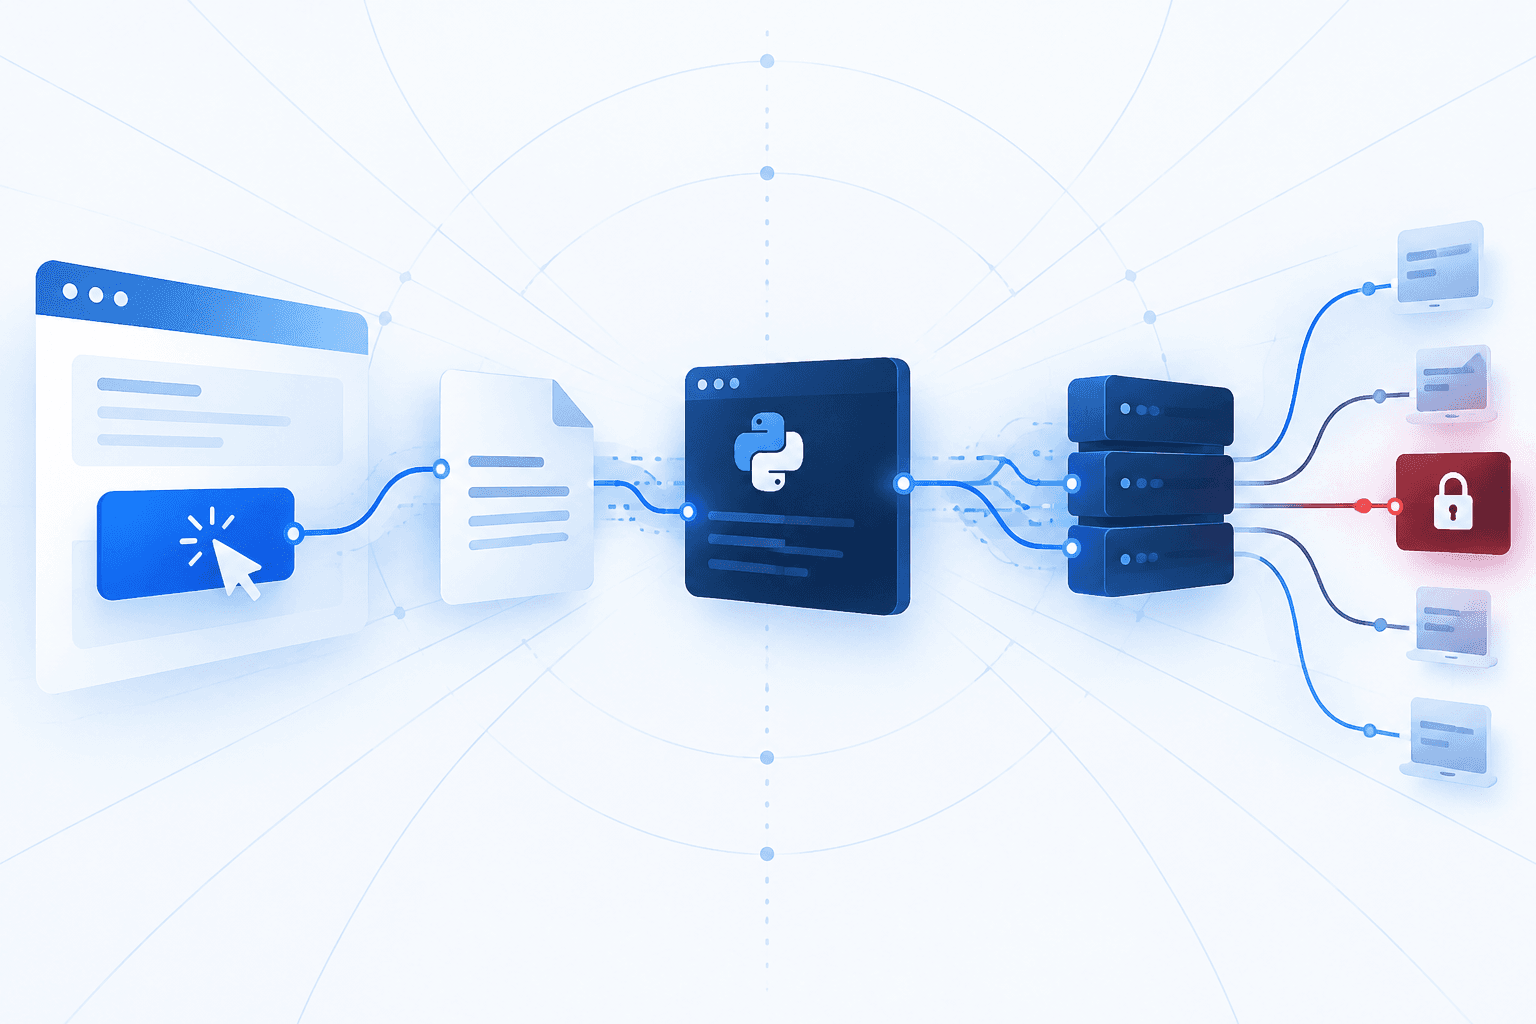
Attackers used ClickFix social engineering in a late-September Windows intrusion to deploy Lorem Ipsum Loader and a Python reverse-tunnel client, establishing access investigators assessed was likely intended for ransomware deployment. Responders contained the intrusion before the suspected final payload was deployed; no ransomware execution was confirmed. The Python client used a TLS-protected WebSocket tunnel capable of relaying multiple TCP connections. Related activity has previously been linked to Vice Society, also tracked as Rapid Brigantine and Vanilla Tempest, but investigators did not establish attribution for this incident.
Forescout analyzed five Lorem Ipsum samples and 39 AxolotlLoader samples, identifying an alternative modified Teams MSI-to-PowerShell delivery chain and three Axolotl variants. Lorem Ipsum uses DLL sideloading, dictionary-encoded payloads, persistence, defense evasion, and legitimate public-forum profiles to retrieve command-and-control information; Axolotl uses standalone executables containing PNG-encrypted shellcode. Shared C2 registration behavior and infrastructure concentrated at AS62005 suggest a possible relationship, but differing code leaves the proposed evolutionary link unconfirmed. Defenders should prioritize detection of ClickFix-driven execution, suspicious DLL sideloading, forum-based C2 resolution, and unexpected Python tunnels, using the report’s confirmed indicators rather than treating unverified infrastructure pivots as established C2.