Malicious Arch AUR Packages Impersonate yay and paru to Run Remote Scripts as Root
Supply Chain Risk · 4 sources · Updated 12d ago · First seen Oct 15, 2026
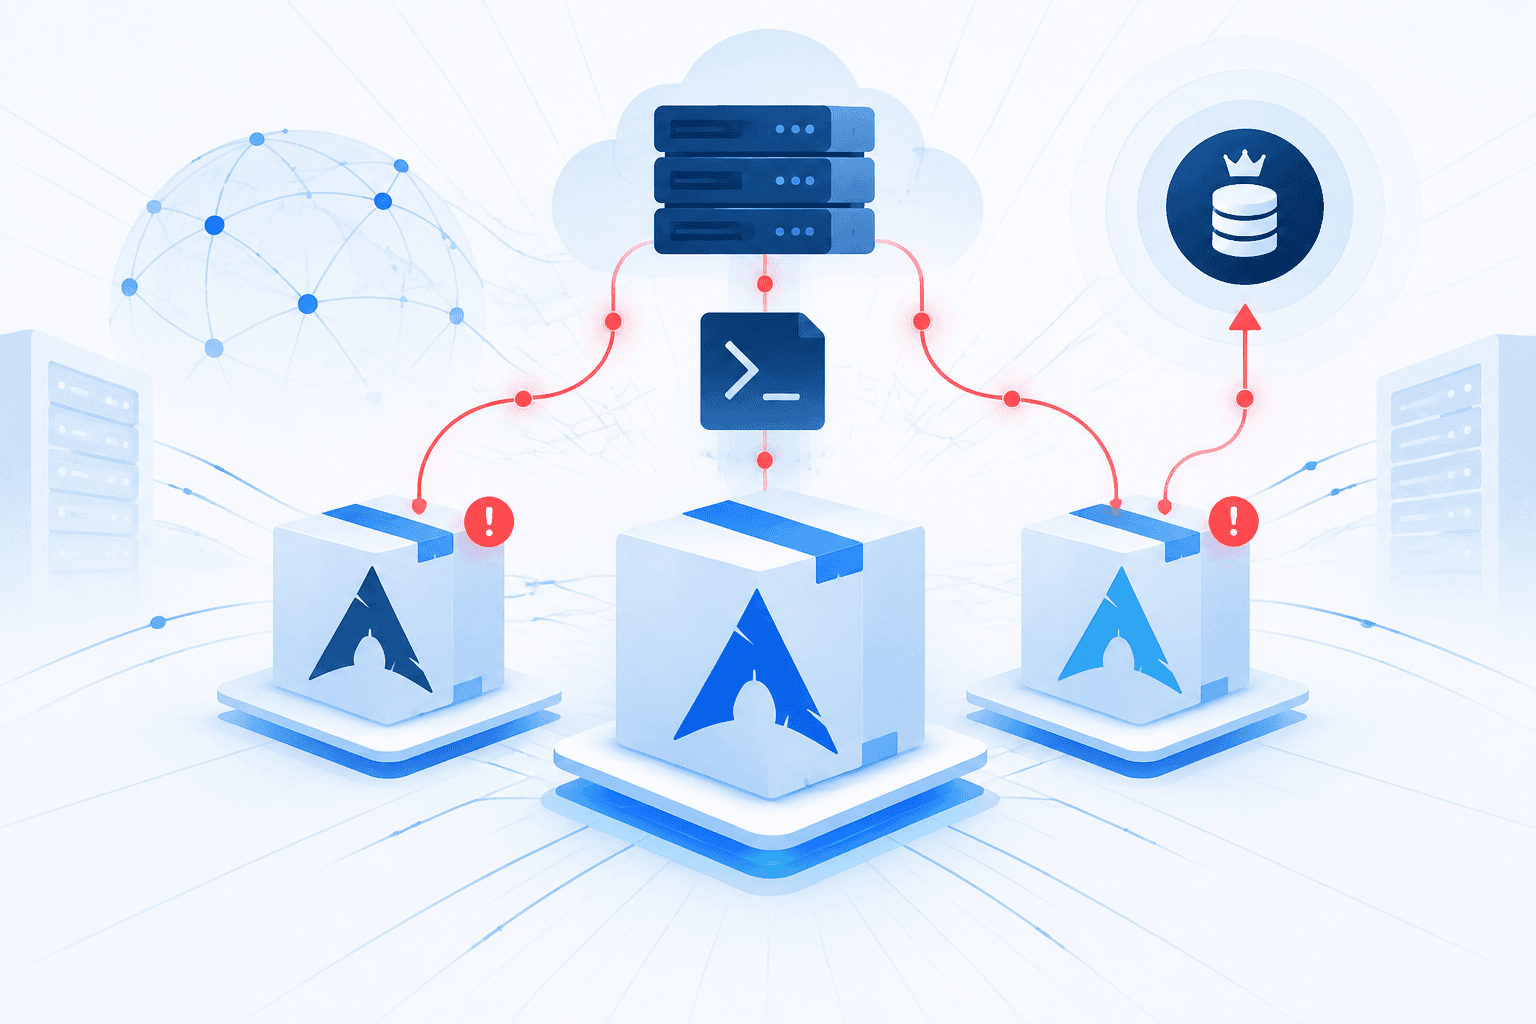
A malicious package campaign targeted the Arch User Repository (AUR) with typosquatted packages impersonating the yay and paru package-management helpers. Detected on October 13, the packages were uploaded by the account “marchos1as” and combined legitimate upstream code with malicious installation scripts designed to download and execute a remote shell script with root privileges. The AUR team banned the account and removed the malicious packages.
A package scan flagged the impersonator yyay with 99% confidence and blocked its build. Its yyay.install scriptlet placed the malicious logic at the top level, while post_install and post_upgrade contained benign-looking commands; the remote payload was neither checksum-verified nor pinned to an archived snapshot. The available evidence does not establish the downloaded payload’s behavior or confirm successful compromises. Infrastructure overlaps suggest a possible, unconfirmed connection to the DirtyBlanket npm worm campaign. Users who downloaded the suspicious packages were advised to assume compromise and take immediate remediation action.