PhantomBuffer PoC Uses Windows GUI Messages and CDB for Stealth Process Injection
Attack Tradecraft · 2 sources · Updated 24d ago · First seen Oct 18, 2026
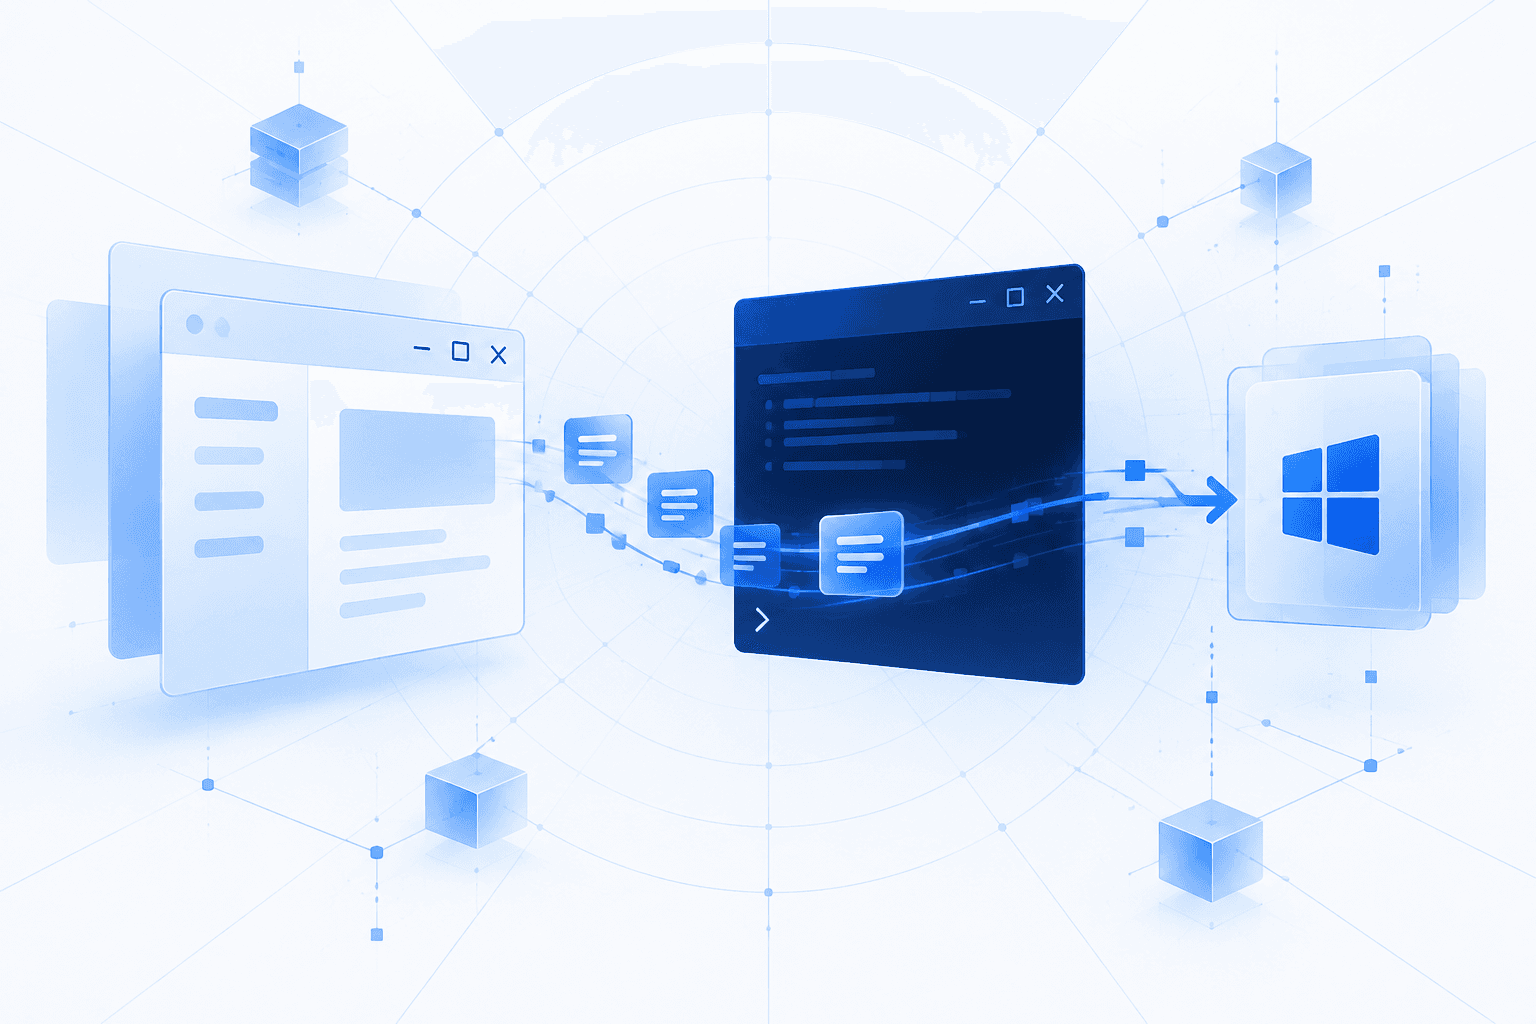
Researcher Two Seven One Three published PhantomBuffer, a proof-of-concept process-injection suite intended to evade endpoint detection and response (EDR) monitoring. The technique uses SendMessageW with WM_SETTEXT to place a payload into a target application's GUI control memory without calling WriteProcessMemory. It then locates the payload, changes its memory permissions to permit execution, and uses Microsoft's CDB debugger to redirect a target thread to the payload.
The researcher reports successful testing against an unnamed high-end EDR, but the supplied reporting provides no independent validation, identifies no affected products, and presents no evidence of real-world malicious deployment. A community post also circulated the claimed bypass without additional test evidence. Defenders should assess monitoring for suspicious SendMessageW activity involving WM_SETTEXT, executable-memory permission changes, thread-context manipulation, and unusual CDB execution paths, rather than relying solely on conventional cross-process memory-write detections.