Loading story…
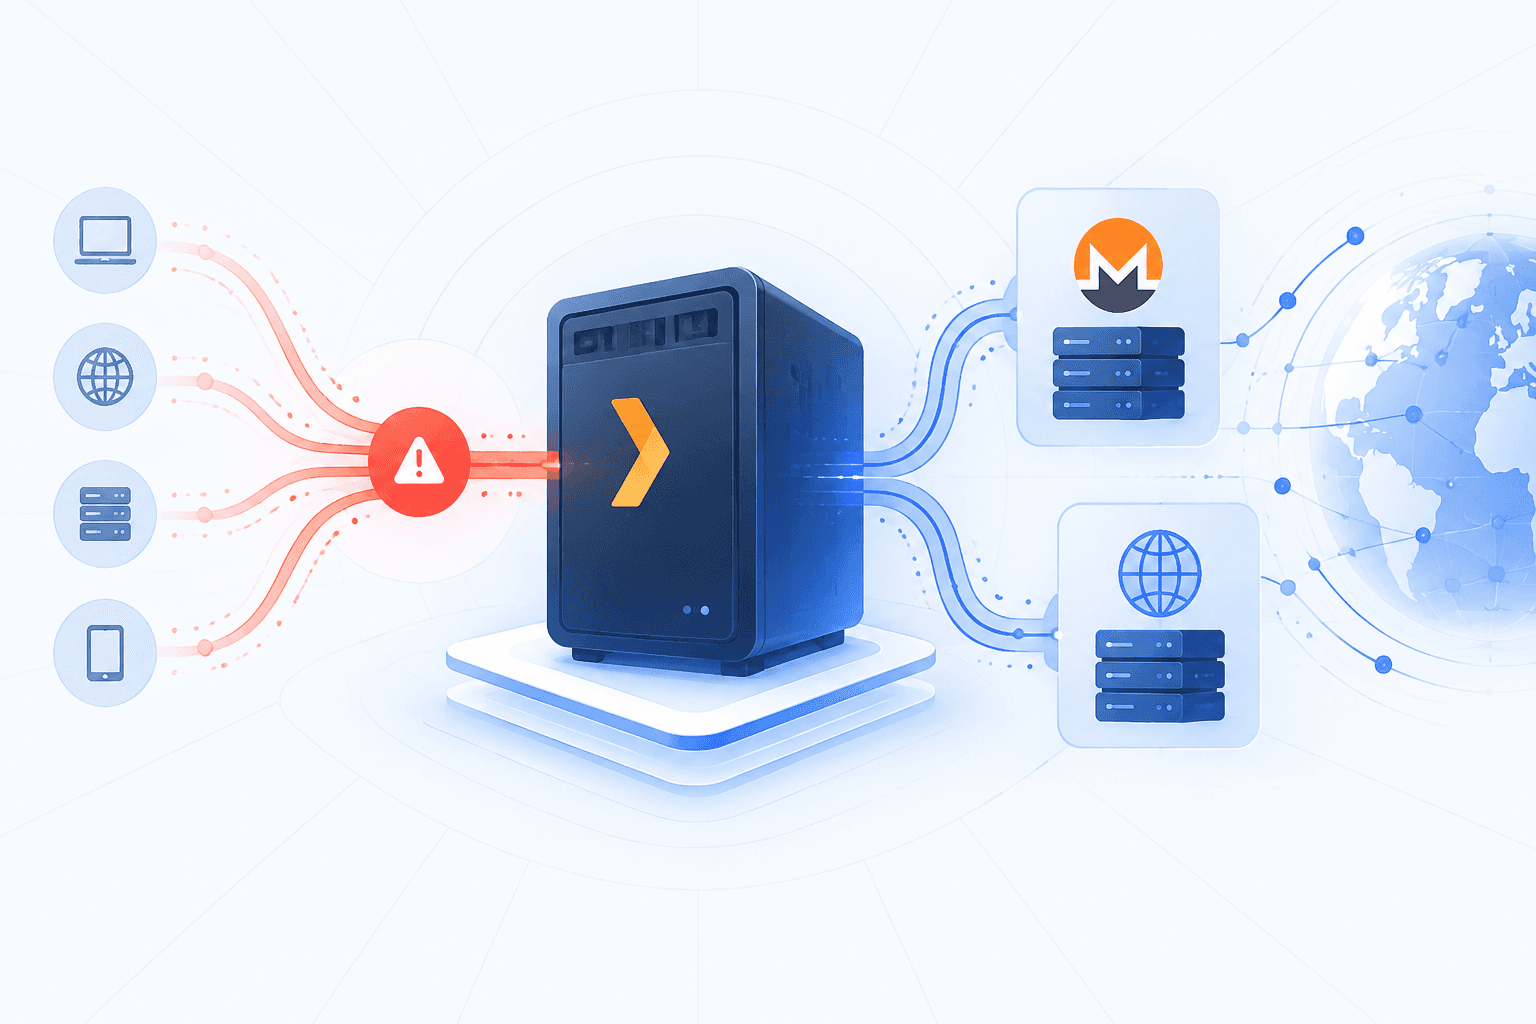
Attackers are exploiting Plex Media Server vulnerabilities to deploy cryptocurrency-mining malware, with successful attacks recorded against a Linux-based Docker honeypot on October 17, 2026. Boredhackerblog observed payload downloads followed by XMRig execution and later reported proxy software running alongside the miner. The public Plex2Shell exploit chains four reported vulnerabilities—CVE-2026-96652, CVE-2026-96654, CVE-2026-96655, and CVE-2026-96656—to achieve unauthenticated remote code execution through server-side request forgery, a loopback authentication bypass and injection, arbitrary-path file writing, and unsigned codec loading. Its repository includes a Python proof of concept and Linux and Windows payload source files, and assigns the chain a CVSS v3.1 score of 9.8.
The repository identifies Plex versions earlier than 1.43.3.10828 as affected and states that 1.43.3.10861 fixes the chain. Exploitation requires the server to reach attacker-controlled infrastructure for media retrieval and reverse-shell connectivity. Administrators should prioritize upgrading, verify the version actually running—including container deployments—and investigate unexpected downloads, processes, mining activity, and proxy software. Restricting unnecessary external exposure and outbound connectivity can reduce attack opportunities. The reported observations establish successful honeypot exploitation, but do not establish the scale of production compromises, attacker identities, or attribution to a specific botnet.
See which actors are running it and whether you're in range.
8 events from the most recent confirmed update back to the earliest known activity.
Boredhackerblog recorded successful exploitation of a Linux-based Plex Media Server honeypot running in Docker. The first attempt originated from 45.194.92[.]222, with further attempts involving 91.92.40[.]202 and 176.65.139[.]228.
Plex announced security updates and urged users to install Plex Media Server 1.43.3 and Plex Desktop 1.115.0. It warned that NAS users might need to install the updates manually.
Plex released Media Server version 1.43.3.10861 with fixes for the disclosed vulnerabilities, including the four-flaw Plex2Shell chain that enables unauthenticated remote code execution.
The discovering researcher reported the four Plex2Shell vulnerabilities to Plex on July 27, 2026. Plex confirmed the vulnerabilities and awarded a bug bounty on August 4, 2026.
Reddit posts described multiple Plex users whose instances were compromised with the mylovelyminer cryptocurrency-mining payload. The report could not confirm whether those compromises resulted from Plex2Shell exploitation.
A subsequent update reported a process named myawesomeproxy and traffic involving proxystream[.]st. The program displayed a message about external use of the device's internet traffic, but the observations did not establish a connection to a specific botnet.
After outbound access was enabled on the honeypot, the researcher observed downloads from 217.60.194[.]116 involving files named docker and x. Published attack artifacts included packed and unpacked samples, followed by execution of an XMRig cryptocurrency miner.
The public Plex2Shell release provided a Python proof of concept and Linux and Windows payload sources chaining CVE-2026-96652, CVE-2026-96654, CVE-2026-96655, and CVE-2026-96656. The repository identifies Plex Media Server versions before 1.43.3.10828 as affected and version 1.43.3.10861 as fixed.
Vulnerabilities, threat actors, malware, products, organizations, breaches, and observables Mallory has linked to this story. Indicator values are masked here and available in full in the app.
Indicator values are masked on this page. View all 14 in Mallory Domains, IPs, hashes, and URLs are exportable to your SIEM.
Correlate live exploitation activity against the software you actually run, and see where you're exposed.
12 references tracked. Mallory keeps watching after this page renders.
acn.gov.it
Open sourcemkd-cirt.mk
Open sourcearstechnica.com
Open sourcesecurityaffairs.com
Open sourcereddit.com
Open sourcegithub.com
Open sourceboredhackerblog.info
Open sourcezmain.info
Open sourceMap indicators from this story to your assets and identify affected systems in minutes.
Every observed campaign, victim, and pivot linked to actors named in this story.
Malware, exploits, and IOCs connected to the activity described here.
YARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Get matching new stories delivered to your team as they break — not the next morning.
Ask questions about this story and take action on the answers.
Other stories Mallory is tracking that overlap on entities, sources, or topic labels.
**React2Shell (CVE-2025-55182)**, a CVSS 10.0 unauthenticated remote code execution vulnerability affecting React Server Components and applications using them, including Next.js, triggered widespread exploitation after its December 3, 2025 disclosure. The flaw involves unsafe handling of serialized input and can be exploited with a single HTTP POST request. Honeypots recorded attempts within approximately 20 hours, and CrowdSec subsequently observed daily attacking IPs rise from roughly 500 to more than 10,000 at the December 11 peak. Researchers documented reverse shells, persistent XMRig cryptocurrency miners, Mirai botnet payloads and activity associated with suspected China-linked operators. Targeting expanded from banks and healthcare organizations to smaller websites and exposed development servers. The Next.js-specific identifier CVE-2025-66478 was rejected as a duplicate of CVE-2025-55182. Exploitation later concentrated around a smaller set of high-volume sources: GreyNoise recorded **1,419,718 attempts during January 26–February 2, 2026**, with two IP addresses generating 56% of activity and delivering distinct reverse-shell and cryptomining payloads. An April WhoisXML API report identified the previously undocumented **ILOVEPOOP toolkit**, linking nine scanner nodes through shared exploit headers, payload structures and reconnaissance patterns. These infrastructure associations and potential-target lists do not establish successful compromise, exfiltration or common ownership, and some threat-actor connections remain unconfirmed. Organizations should inventory affected applications across cloud and on-premises environments, patch React Server Components and affected frameworks, and restrict internet exposure of development servers. Where patching is unavailable, disable affected server-component functionality if feasible. Investigations should review historical ingress logs for suspicious headers and serialized payloads, unexpected child processes spawned by Node.js, outbound command-and-control connections and unauthorized persistent services; WAF rules and IP blocking are supplementary controls, not substitutes for remediation.
Oct 13, 2026
Security researchers reported an active campaign exploiting **React2Shell** (`CVE-2025-55182`) in React.js and Next.js server components to achieve remote code execution and deploy **XMRig** for Monero mining. Darktrace observed the activity through its **CloudyPots** honeypot network, where an attacker abused an exposed, unauthenticated Docker daemon to launch a container, install utilities, retrieve Python components from Pastebin and a GitHub Gist, and validate exploitation with commands such as: ```bash whoami wget ``` The exploit chain used crafted Next.js server component payloads to trigger exceptions and leak command output, enabling shell execution on vulnerable targets.
Jul 9, 2026
AhnLab Security intelligence Center (ASEC) reported an ongoing campaign targeting poorly managed Linux servers, where attackers gain access through SSH brute-force attempts or stolen credentials and then deploy propagation malware to install **XMRig**-based coin miners. Observed through multiple honeypots, the activity uses a multi-stage toolset that includes Go-based downloaders and SSH spreaders, along with malware families such as **ShellBot/PerlBot**, **MIG LogCleaner**, and **XHide** to move laterally, fetch payloads, hide activity, and maintain control of compromised hosts. The miners are disguised as legitimate processes and are installed with multiple persistence mechanisms, including `systemd` services, cron jobs, hidden binary paths, and watchdog functions that restore deleted payloads. ASEC said the propagation malware scans for exposed SSH services, authenticates with credential lists, installs miners on newly compromised systems, and reports results back to attacker infrastructure, assessing that the same threat actor has likely been conducting Linux-focused cryptomining attacks since at least 2023.
Jul 15, 2026