Apache Camel Path-Case Mismatch Allows Authorization Bypass in camel-netty-http
Vulnerability Disclosure · 5 sources · Updated 7d ago · First seen Oct 19, 2026
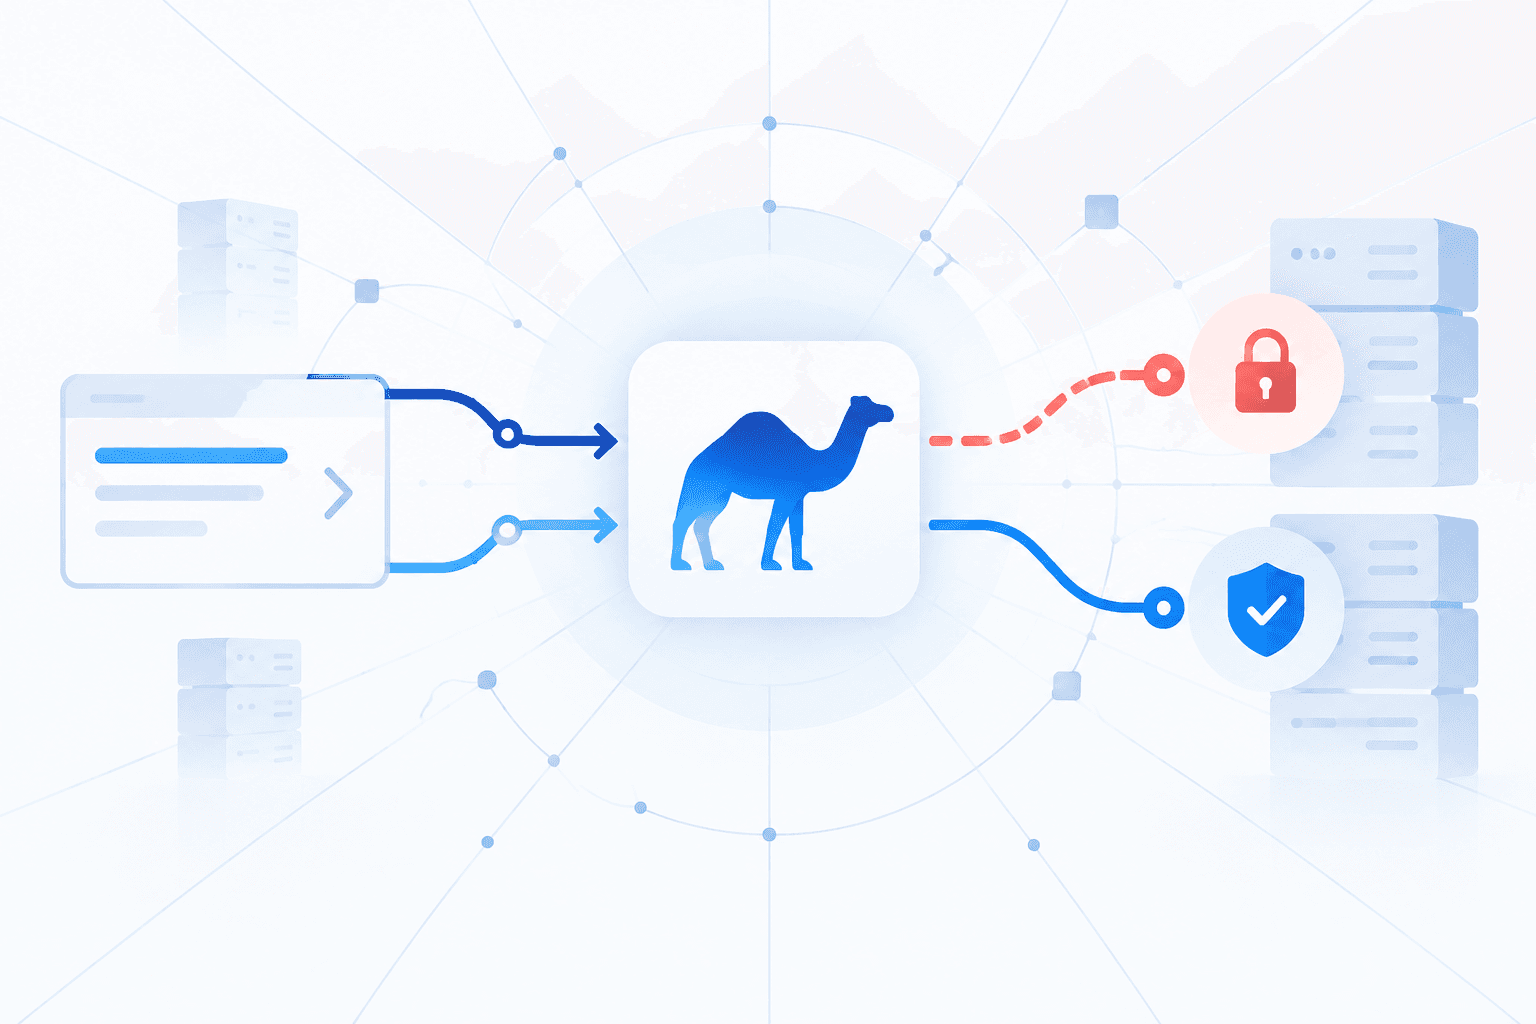
Apache disclosed CVE-2026-80343, a security-constraint bypass in its camel-netty-http component that allows an unauthenticated external caller to reach a protected endpoint by changing the letter case of the request’s context path. The flaw stems from inconsistent path handling: a case-sensitive check prevents context-path stripping during security-constraint evaluation, while request dispatch still accepts the differently cased path. The documented bypass involves matchOnUriPrefix=true and security constraints protecting specific sub-paths.
Apache fixed the issue in 4.23.0, 4.18.5, and 4.22.1, aligning security checks with dispatch through case-insensitive context-path stripping. Regression tests verify that both exact-case and differently cased requests receive an authentication challenge. Security teams should identify affected consumers and upgrade to a fixed release; the end-of-life 4.14.x line will not receive a fix. Where upgrades cannot be applied immediately, Apache recommends enforcing authorization before the Camel consumer, such as through a reverse proxy that normalizes request paths.