Apache Camel AS2 Flaw Enables SSRF and MDN Credential Disclosure
Vulnerability Disclosure · 5 sources · Updated 7d ago · First seen Oct 19, 2026
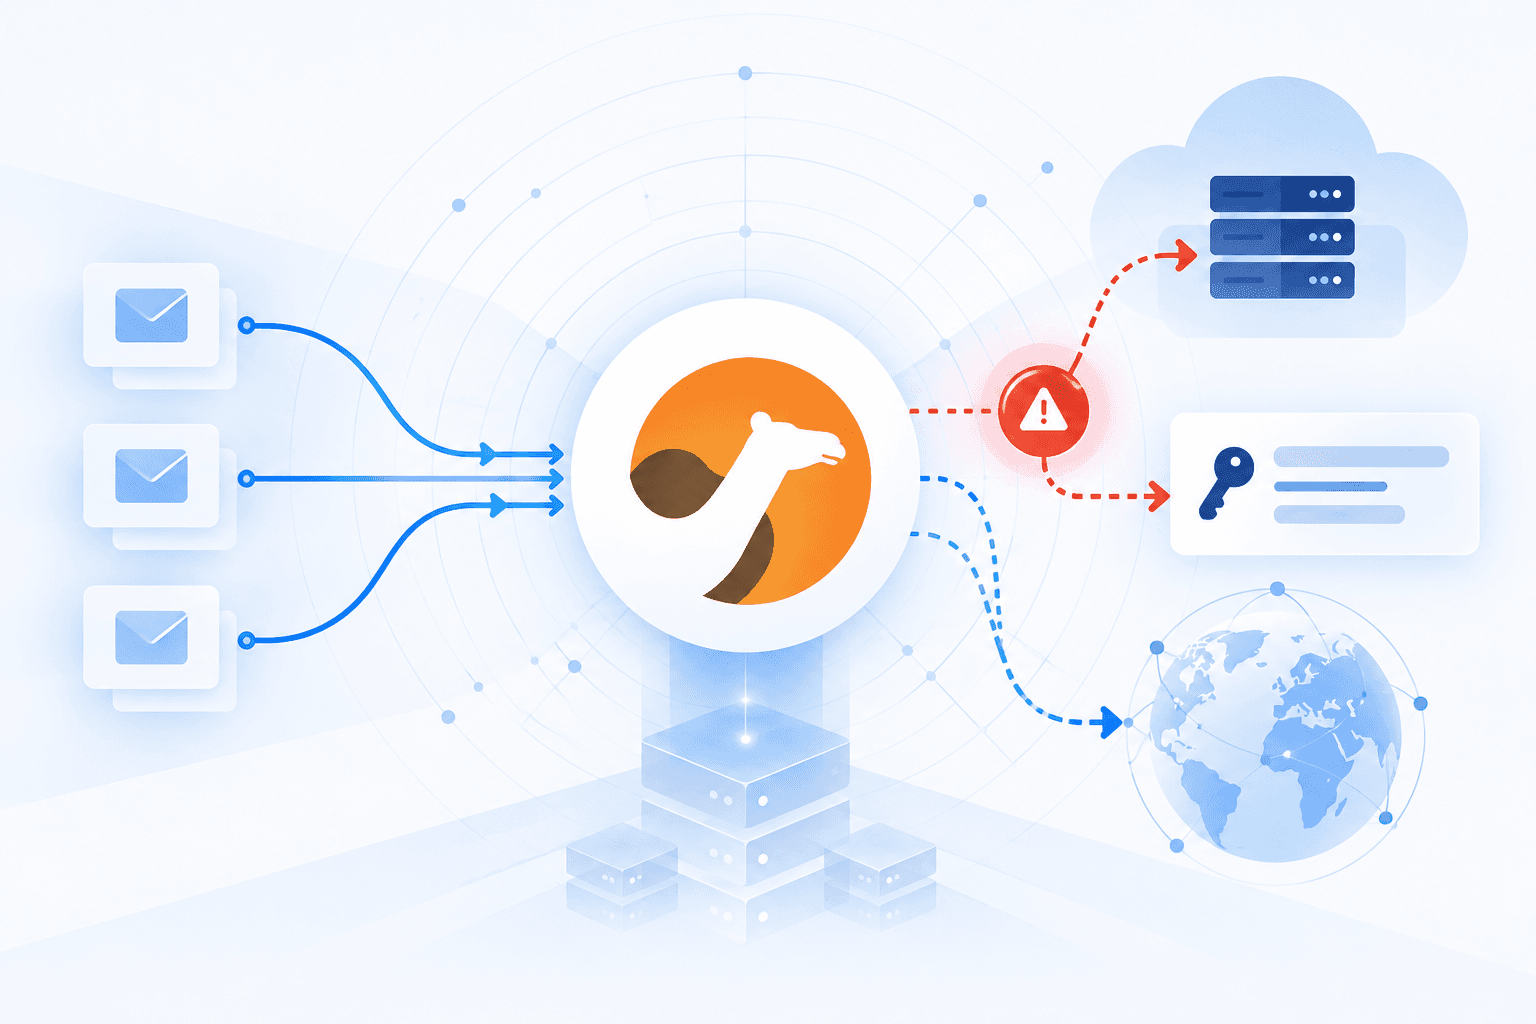
Apache disclosed CVE-2026-80344, a server-side request forgery and conditional credential-disclosure vulnerability in its camel-as2 component. The component trusted asynchronous Message Disposition Notification (MDN) destinations supplied through the sender-controlled Receipt-Delivery-Option header, allowing outbound connections to attacker-selected hosts, including internal systems. Configured Basic or Bearer credentials could also be sent to those destinations. Because delivery used a plain socket without validating the URI scheme, an HTTPS address could cause credentials to be transmitted in cleartext to a TLS port.
Apache fixed the issue in Camel 4.23.0, 4.22.1, and 4.18.5; the end-of-life 4.14.x line will not receive a fix. The patch adds asyncMdnAllowedHosts to restrict destinations and scope credential attachment; when unset, delivery remains enabled but credentials are omitted. It accepts only HTTP and rejects HTTPS, with actual TLS support tracked separately under CAMEL-24474. Operators should upgrade, explicitly configure legitimate partner hosts, and account for a shared-port caveat: the first endpoint initialized on a port determines the allowlist for other endpoints sharing it. Until upgrading, restrict AS2 receiver egress to legitimate partners and avoid MDN credentials valid beyond those partners.