Mallory
← Back to News
actively-exploited-vulnerabilityransomware-group-operationidentity-authentication-vulnerabilitycredential-access-method

Ransomware Operators Exploit GlobalProtect MFA Bypass to Steal Credentials From VMware Disks

Active Exploitation · 14 sources · Updated 24d ago · First seen Oct 20, 2026
Ransomware Operators Exploit GlobalProtect MFA Bypass to Steal Credentials From VMware Disks

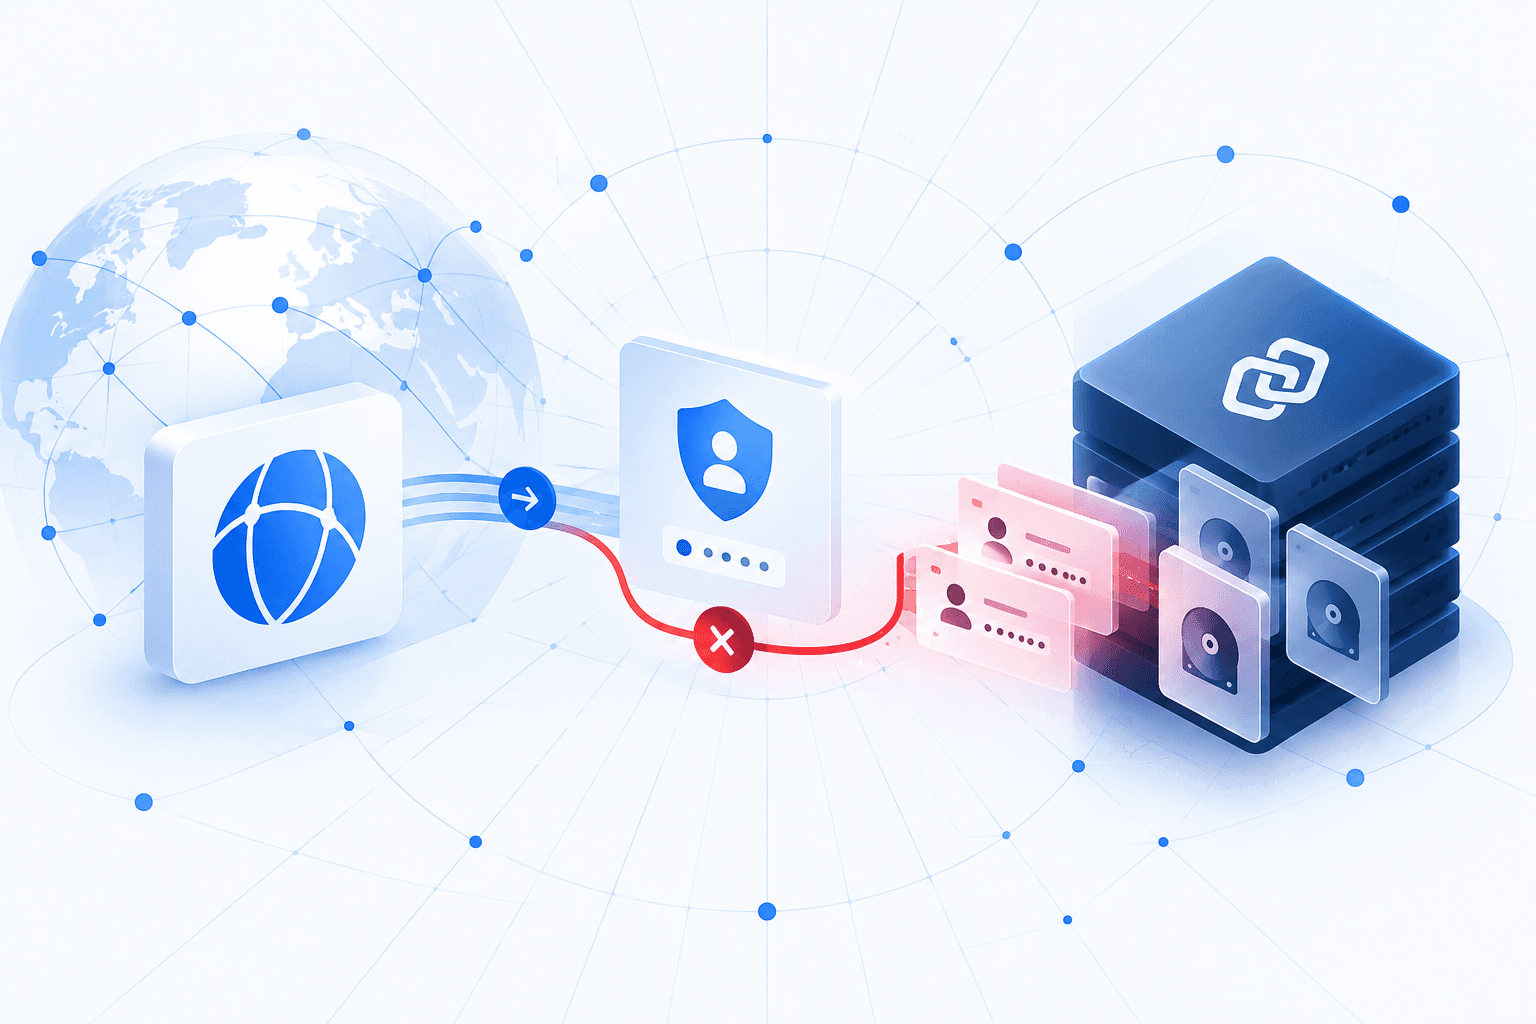
Ransomware operators are exploiting CVE-2026-0257 in certain Palo Alto Networks GlobalProtect deployments, using forged authentication override cookies to bypass authentication and multi-factor authentication and enter corporate networks. Unit 42 linked exploitation to Qilin and Inc, while separate public reporting connected exploitation to operators using Settra ransomware. In one investigated intrusion, attackers accessed VMware management infrastructure, disabled an ESXi security control, and extracted credentials directly from a domain controller’s virtual disk, bypassing endpoint security controls running inside the virtual machine. Investigators also observed tools targeting Veeam backup infrastructure through CVE-2023-27532.

Organizations should prioritize upgrading affected GlobalProtect portals and gateways and investigate suspicious successful VPN connections rather than relying solely on failed-login alerts. Temporary mitigations include disabling authentication override or using a new certificate dedicated exclusively to override cookies. Incident-response investigations should extend beyond VPN access to VMware management systems, domain controller virtual disks, and Veeam infrastructure, given the observed credential theft and backup-targeting activity.
This is being exploited nowSee which actors are running it and whether you're in range.
Check your exposure
Event timeline

How this story unfolded

Events from the most recent confirmed update back to the earliest known activity.

12 events · May 2026 – Oct 19, 2026
  1. Reported Oct 21, 202626d ago

    Qilin and INC reportedly encrypt ESXi datastores after GlobalProtect compromise

    The report describes Qilin and INC Ransom intrusions progressing from CVE-2026-0257 exploitation to ESXi encryption in less than four hours. Attackers reportedly obtain vCenter or ESXi administrator credentials, forcibly shut down virtual machines, and deploy Linux encryptors against virtual disks and datastore storage.

    PAN-OS GlobalProtect MFA Bypass: Qilin and INC R | Shellcode
  2. Reported Oct 20, 202628d ago

    Public reporting links GlobalProtect exploitation to Settra ransomware operators

    Separate public reporting connected exploitation of CVE-2026-0257 to operators using Settra ransomware.

    Hackers Exploit Palo Alto VPN Flaw to Bypass MFA and Steal Credentials From VMware Disks | Cryptika Cybersecurity
  3. Reported Oct 20, 202628d ago

    Rapid7 explains how forged cookies bypass GlobalProtect authentication

    Rapid7’s technical analysis found that vulnerable devices decrypt authentication override cookies without properly verifying their trusted origin. When the cookie certificate is reused on a publicly exposed service, attackers can obtain its public key and forge cookies that bypass normal login and MFA checks.

    Hackers Exploit Palo Alto VPN Flaw to Bypass MFA and Steal Credentials From VMware Disks | Cryptika Cybersecurity
  4. Reported Oct 20, 202628d ago

    Unit 42 observes Veeam targeting following GlobalProtect compromise

    Unit 42 observed attackers combining GlobalProtect initial access with tools targeting Veeam backup infrastructure through CVE-2023-27532. The vulnerability can expose encrypted credentials in the backup configuration database, potentially enabling access to backup hosts.

    Hackers Exploit Palo Alto VPN Flaw to Bypass MFA and Steal Credentials From VMware Disks | Cryptika Cybersecurity
  5. Reported Oct 20, 202628d ago

    Attackers extract domain controller credentials from a VMware virtual disk

    In one investigated intrusion, attackers moved from a compromised GlobalProtect gateway to VMware vCenter and disabled the execInstalledOnly security control on ESXi hosts. They then used a custom tool to extract credentials offline from a domain controller’s VMDK disk, bypassing endpoint security controls inside the virtual machine.

    Hackers Exploit Palo Alto VPN Flaw to Bypass MFA and Steal Credentials From VMware Disks | Cryptika Cybersecurity
  6. Reported Oct 20, 202628d ago

    Investigators examine GlobalProtect exploitation across multiple sectors

    Investigations ongoing since early June examined ransomware operators exploiting CVE-2026-0257 to bypass GlobalProtect authentication and MFA. Affected sectors included healthcare, education, financial services, manufacturing, government, and energy.

    Hackers Exploit Palo Alto VPN Flaw to Bypass MFA and Steal Credentials From VMware Disks | Cryptika Cybersecurity
  7. Oct 19, 202629d ago

    Unit 42 updates threat brief and links exploitation to Qilin and Inc

    In an October 19 threat brief update, Palo Alto Networks Unit 42 detailed exploitation of CVE-2026-0257. It linked the activity to Spikey Scorpius, also known as Qilin, and Tarnished Scorpius, also known as Inc.

    Hackers Exploit Palo Alto VPN Flaw to Bypass MFA and Steal Credentials From VMware Disks | Cryptika Cybersecurity
  8. Jul 2026

    Arctic Wolf flags Qilin exploitation of GlobalProtect authentication bypass

    In July 2026, Arctic Wolf flagged Qilin ransomware actors exploiting CVE-2026-0257, the authentication bypass affecting Palo Alto Networks PAN-OS and Prisma Access.

    Qilin and INC Ransomware Groups Continue Exploiting Patched Palo Alto Flaw, Now Pivoting Directly to Virtualization Layer (CVE-2026-0257) | Uganda National Computer Emergency Response Team-National Cert
  9. May 29, 20266mo ago

    Proof of concept released for GlobalProtect authentication bypass

    A proof of concept for CVE-2026-0257 was released on May 29, 2026. The report identifies a hard-coded endpoint_os_version value of 'Microsoft Windows 10 Pro 64-bit' and an empty source_user_info.domain value as indicators for hunting post-release exploitation.

    CVE-2026-0257: Actively Exploited PAN-OS GlobalProtect Authentication Bypass Vulnerability - Malware News - Malware Analysis, News and Indicators
  10. May 29, 20266mo ago

    Palo Alto Networks acknowledges GlobalProtect exploitation attempts

    Palo Alto Networks updated its CVE-2026-0257 advisory on May 29 to acknowledge limited exploitation attempts against unpatched PAN-OS devices without mitigations.

    Ransomware gangs have been exploiting Palo Alto GlobalProtect VPN flaw since June - Help Net Security
  11. May 13, 20266mo ago

    CISA adds GlobalProtect authentication bypass flaw to KEV catalog

    On May 13, 2026, CISA added CVE-2026-0257 to its Known Exploited Vulnerabilities catalog. The vulnerability affects Palo Alto Networks PAN-OS and Prisma Access and enables attackers to establish unauthorized VPN connections while bypassing authentication and MFA.

    Qilin and INC Ransomware Groups Exploit Palo Alto Networks Flaw to Bypass MFA
  12. May 2026

    Palo Alto Networks releases patch for GlobalProtect authentication bypass

    Palo Alto Networks reportedly released a patch for CVE-2026-0257 in May 2026. The PAN-OS vulnerability allows attackers to bypass GlobalProtect authentication and establish VPN sessions without MFA.

    PAN-OS patched in May. Still a ransomware favorite in October. : r/sysadmin
Linked entities

Related entities

Vulnerabilities, threat actors, malware, products, organizations, breaches, and observables Mallory has linked to this story. Indicator values are masked here and available in full in the app.

Open in app →

Malware

2 linked

Affected products

5 linked
GlobalprotectPrisma AccessVmware EsxiVmware Vcenter ServerPan-Os

Observables

11 linked

Indicator values are masked on this page. View all 11 in Mallory Domains, IPs, hashes, and URLs are exportable to your SIEM.

Do you run this?Correlate live exploitation activity against the software you actually run, and see where you're exposed.
See Who's Exploiting This
Mallory platform

See the full picture, correlated to your attack surface.

This page covers what’s public. Mallory adds the parts that aren’t: which of your assets are affected, which threat actors are using it right now, and what to deploy next.

Exposure mappingMap indicators from this story to your assets and identify affected systems in minutes.
Threat actor evidenceEvery observed campaign, victim, and pivot linked to actors named in this story.
Associated malwareMalware, exploits, and IOCs connected to the activity described here.
Detection signaturesYARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Scheduled alertsGet matching new stories delivered to your team as they break, not the next morning.
AI threadsAsk questions about this story and take action on the answers.