Cloned Bank Support Sites Lure Customers Into Installing Remote-Access Tools
Social Engineering & Fraud · 3 sources · Updated 28d ago · First seen Oct 20, 2026
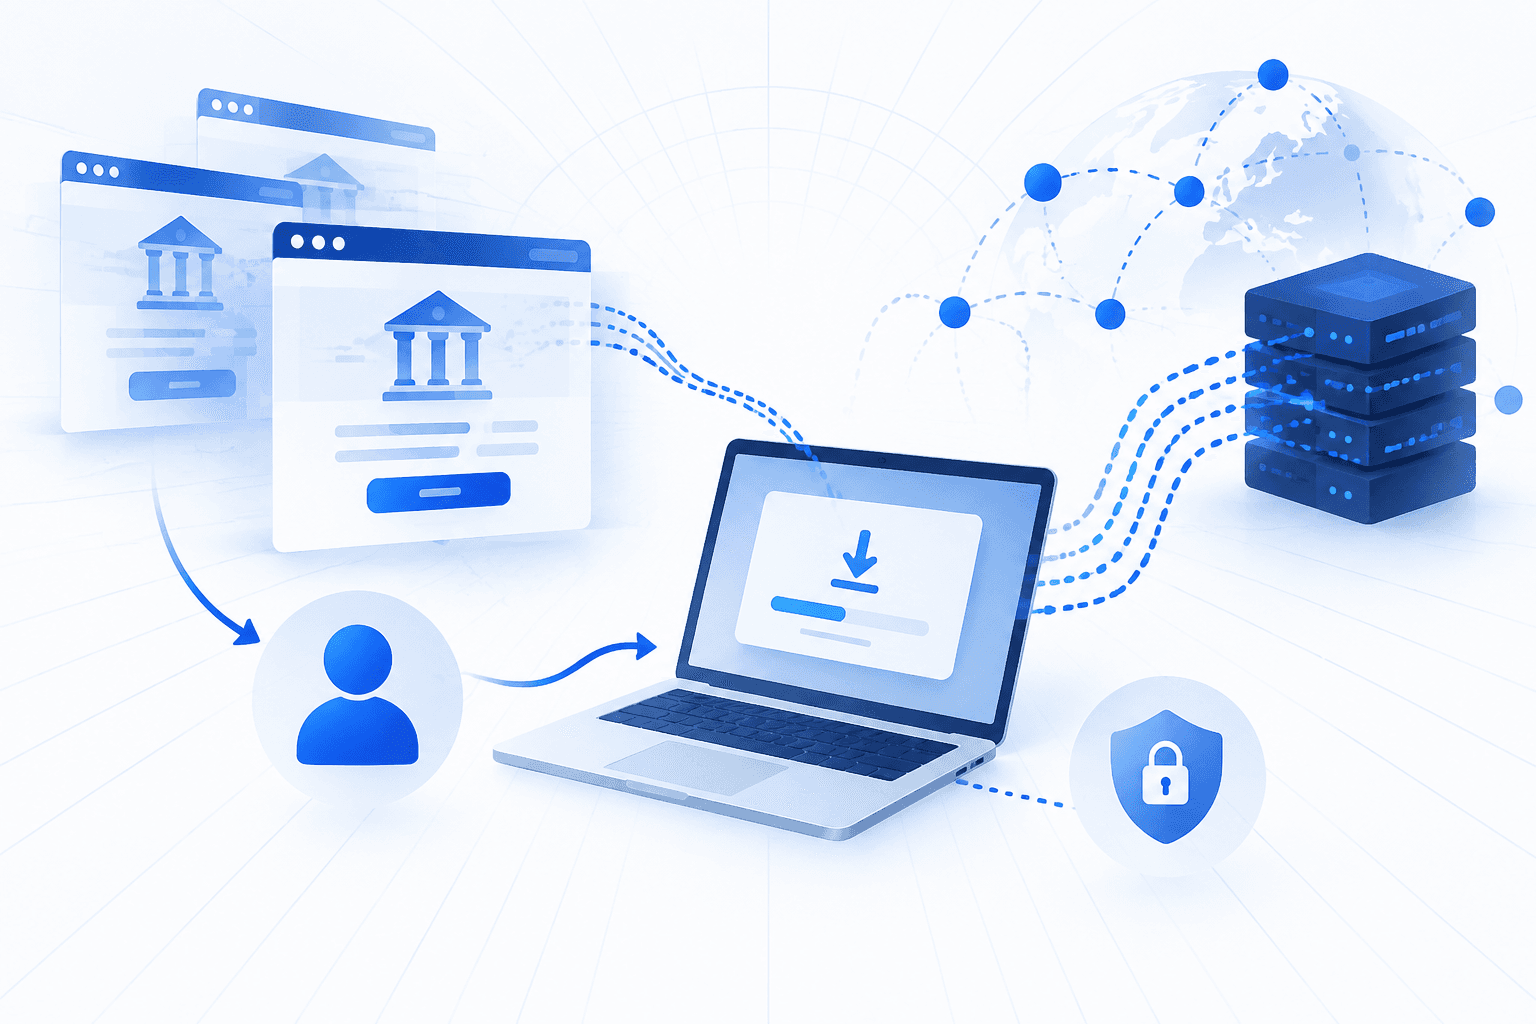
An active phone-led fraud campaign is using cloned bank support websites to persuade customers to call fraudsters and install remote-access software. Lab539 linked more than 380 domains to the operation, which has operated since at least March 2026 and impersonates Barclays, HSBC, Lloyds, Revolut and Santander. Callers are guided through fake verification workflows that deliver AnyDesk or malicious packages that install ScreenConnect, giving attackers remote access to victims’ devices.
Some payloads disable security tools, escalate privileges or use DLL sideloading, including an attack chain that abuses a genuine Microsoft Defender component to load a malicious DLL. Two malicious files carried signing certificates assigned to Japan-based Botania Games, although the company’s involvement remains unclear. The certificates were revoked after Lab539 reported them on October 9, but revocation alone does not prevent download or execution. Lab539 shared additional research with vetted defenders and the impersonated financial institutions to support defensive action.