Symantec Uncovers ‘Skynet’ Agent Designed to Hijack AI Models for Autonomous Attacks
Emerging Technology Risk · 6 sources · Updated 7h ago · First seen Oct 21, 2026
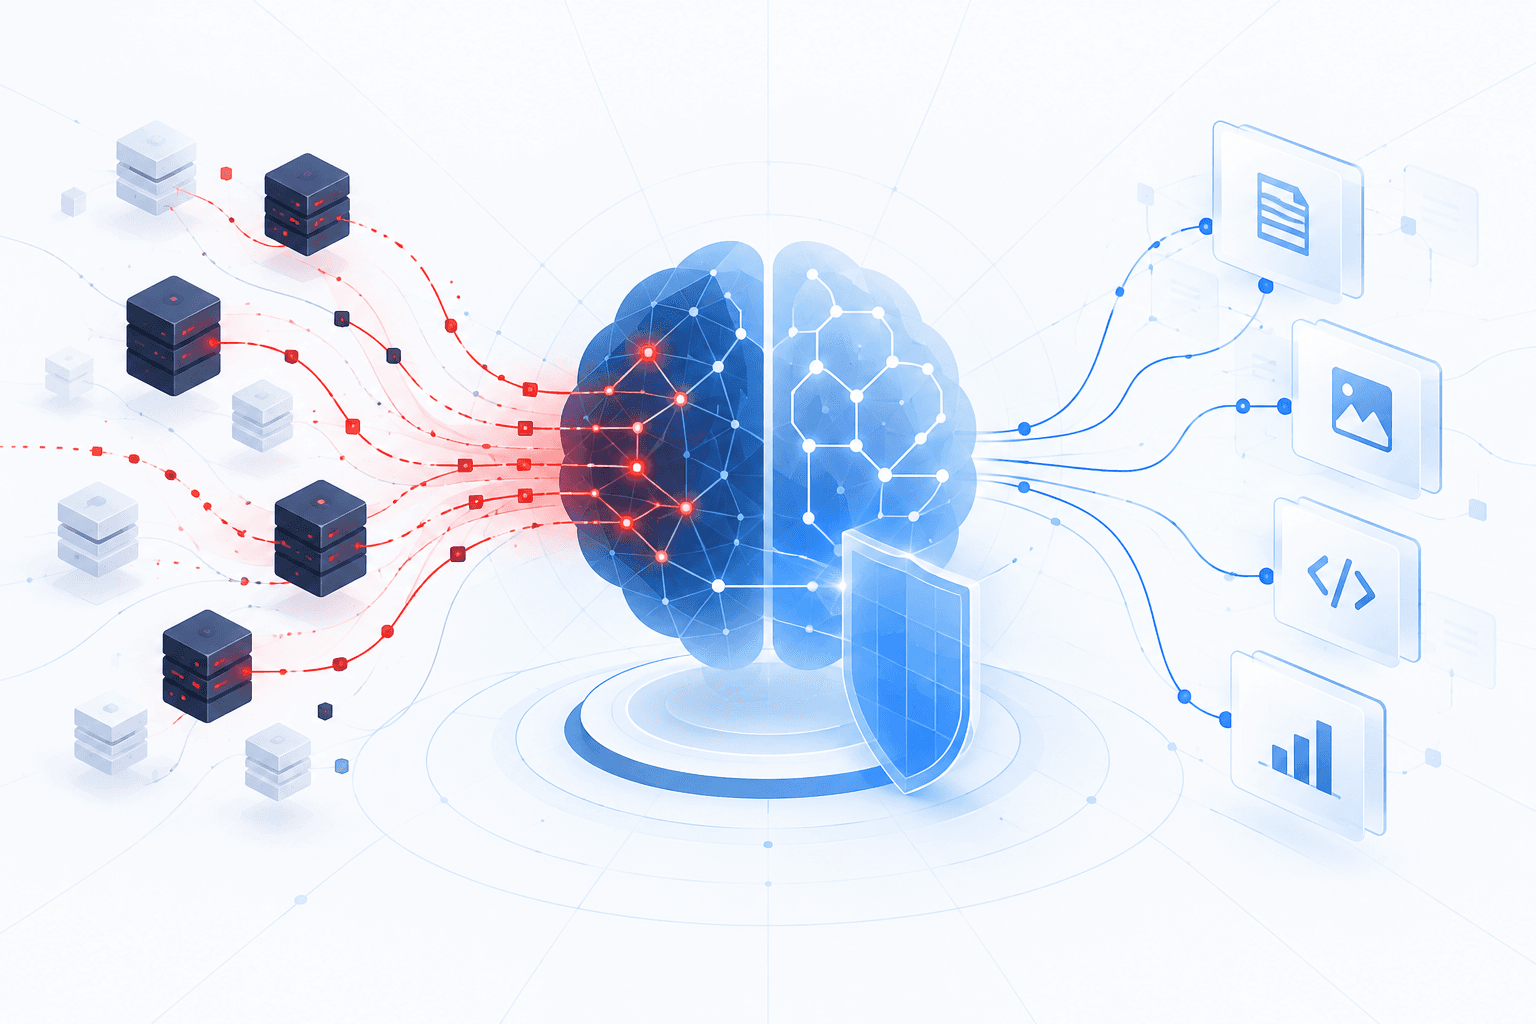
Symantec researchers captured instructions for an autonomous offensive agent dubbed Skynet, designed to hijack exposed large language model endpoints and use victims’ inference resources to conduct cyberattacks. Captured through an AI honeypot, the agent combined layered jailbreaks with approximately 74 offensive tool definitions and permission to run up to 100,000 unattended steps. Its intended capabilities included reconnaissance, vulnerability exploitation, credential and data theft, cryptocurrency mining, and reinfection. The LLMjacking approach shifts inference costs to victims while helping attackers conceal their activity and avoid provider account bans.
A separate request captured the following day contained an obfuscated XMRig deployment script apparently tailored to go2rtc camera-server environments. The honeypot executed neither request, so the findings demonstrate attacker intent and tooling—not confirmed compromises or successful end-to-end autonomous attacks. The integration of established techniques into a self-directed agent could lower the skill needed to launch broad exploitation campaigns. Organizations should authenticate AI endpoints, protect API keys, restrict agent privileges and outbound connectivity, and require approval for sensitive tool actions.