Eternidade Banking Trojan Uses WhatsApp Phishing and Process Hollowing to Target Windows Users
Malware Intelligence · 3 sources · Updated 6d ago · First seen Nov 19, 2025
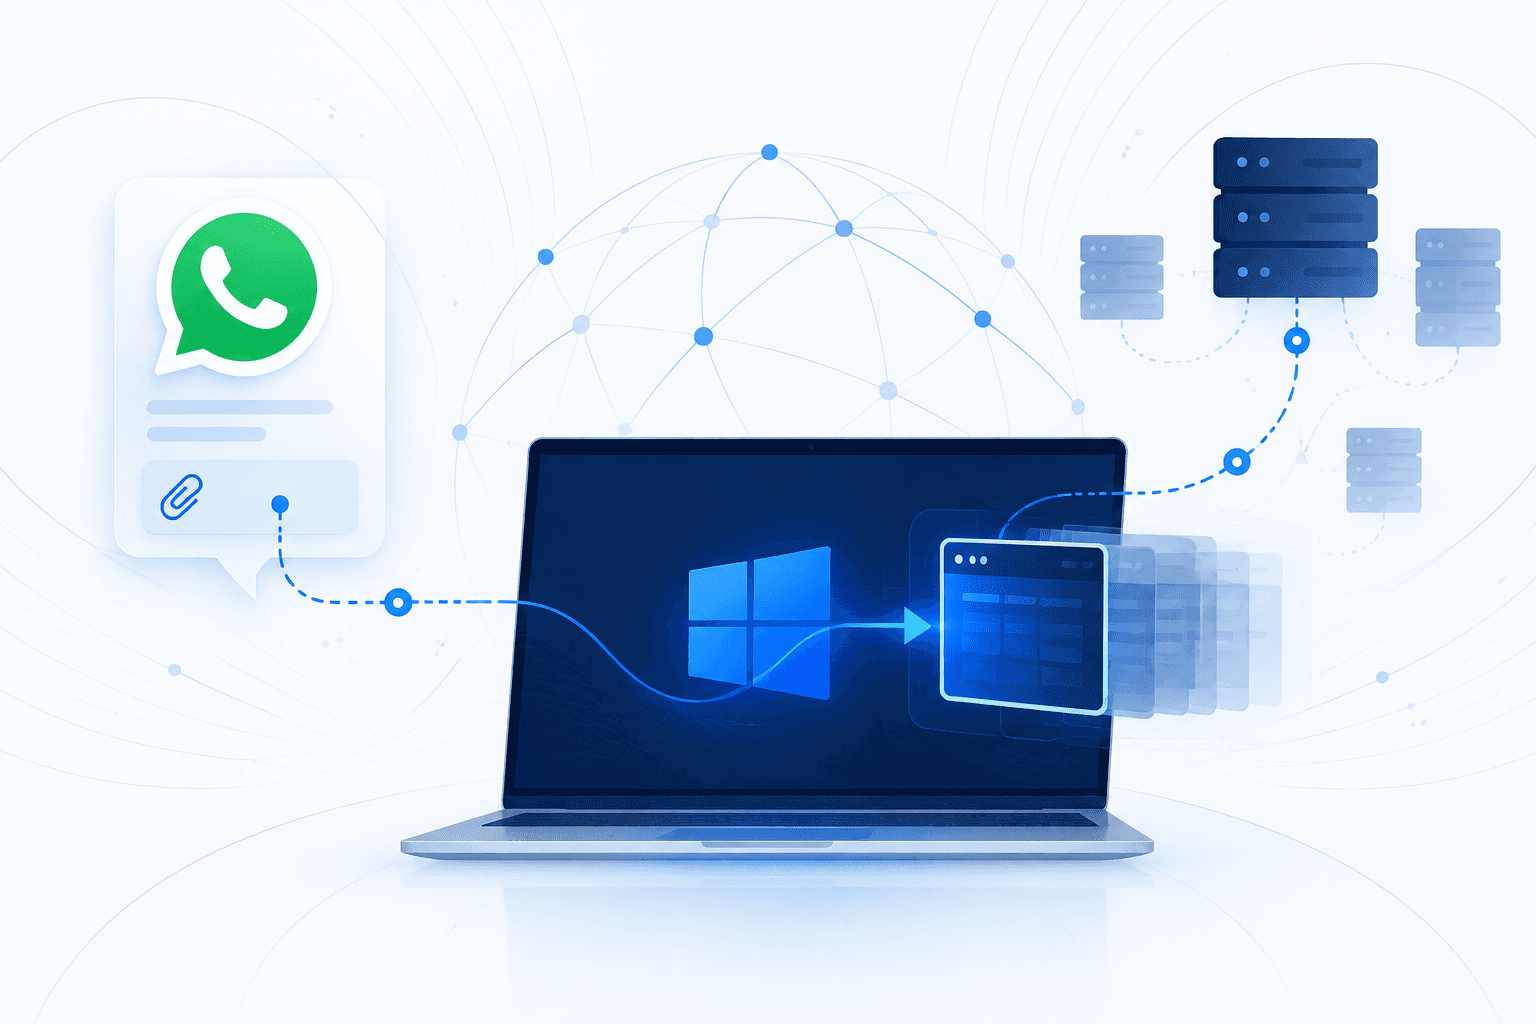
An active Eternidade Stealer campaign is targeting Windows users, primarily in Brazil, through WhatsApp phishing and a multistage malware delivery chain. Analysis of a September 2026 infection chain shows a malicious MSI installer deploying AutoIt scripts and encrypted payload containers before using process hollowing into RegSvcs.exe to execute the Delphi-based banking Trojan. First publicly documented by SpiderLabs in November 2025, Eternidade includes references to 95 banking institutions across Brazil, Portugal, Argentina, and Mexico; those references do not establish that the institutions were breached. No specific threat group has been confirmed as responsible.
Eternidade gives operators banking credential overlays, screen capture and streaming, keyboard and mouse control, clipboard manipulation, file transfer, and shell command execution. It discovers its command-and-control address through an IMAPS mailbox, falls back to secretonow[.]site, and communicates over a proprietary TCP protocol using separate operational channels on port 8090. Defenders should prioritize suspicious MSI-to-AutoIt execution chains, process hollowing involving RegSvcs.exe, and unexpected IMAPS or outbound TCP/8090 activity, using the published hashes, filesystem artifacts, registry indicators, and network observables to scope potential infections.