Four HAPI FHIR Flaws Risk Cross-Tenant Patient Data Exposure and Denial of Service
Vulnerability Disclosure · 3 sources · Updated 21h ago · First seen Oct 23, 2026
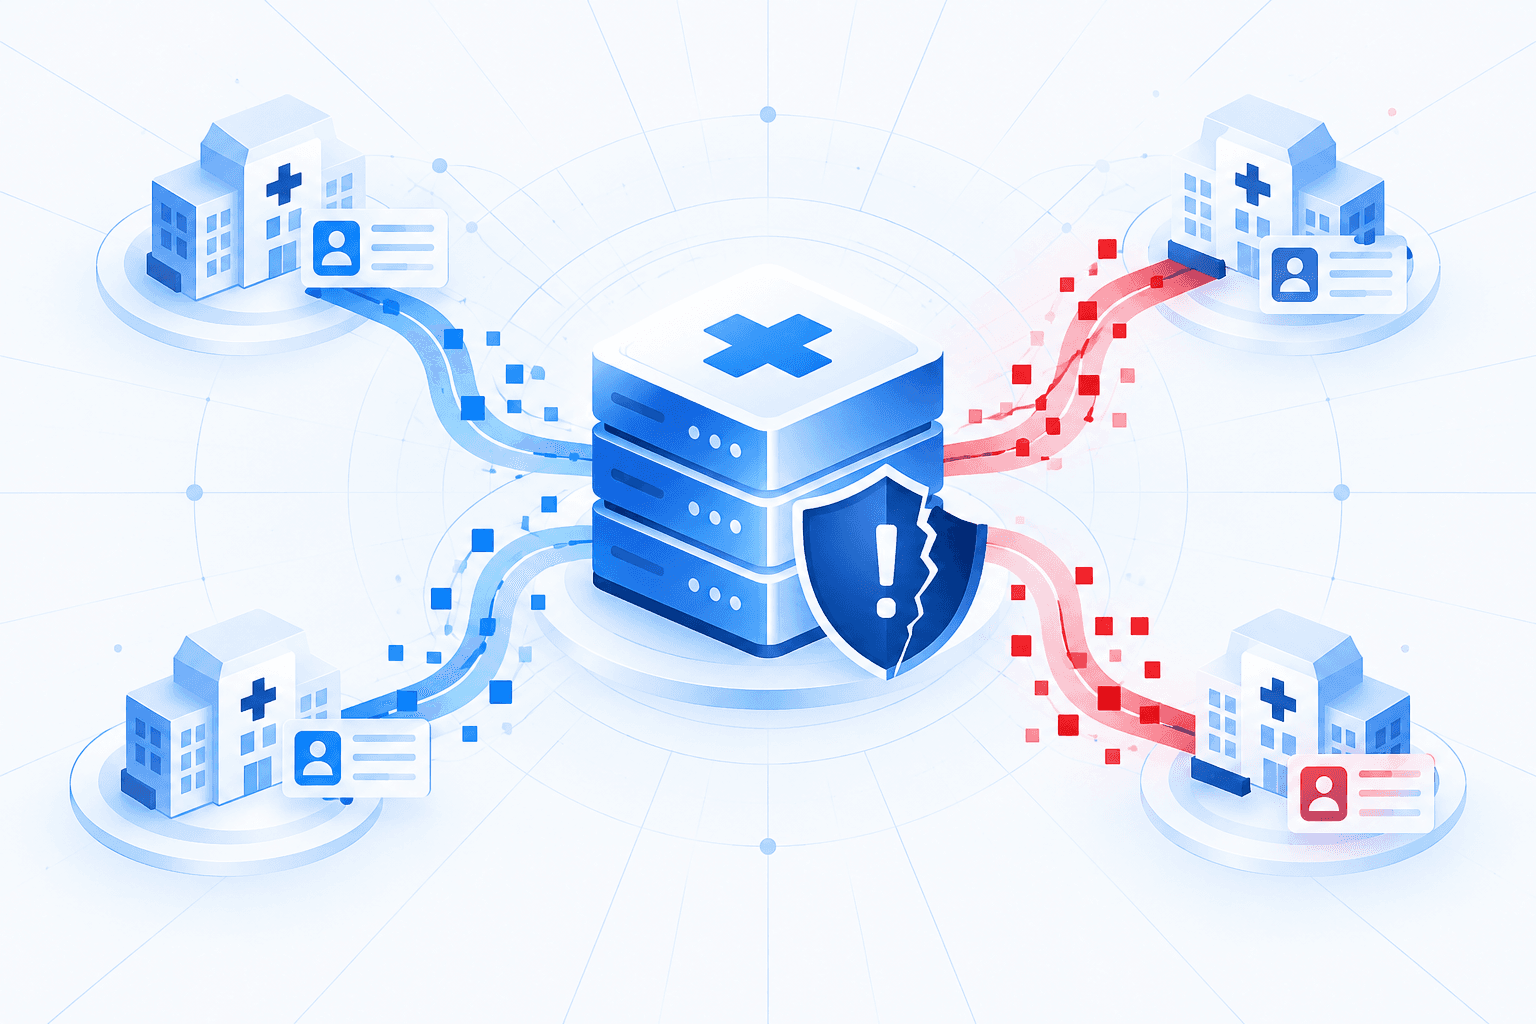
Independent researcher Abhinav Agarwal identified four vulnerabilities in HAPI FHIR 8.10.0, an open-source healthcare interoperability component used in Smile Digital Health’s Smile CDR and other commercial products. Depending on deployment configuration, the flaws could expose patient records across authorization boundaries, allow record creation in another tenant’s partition, or enable unauthenticated memory-exhaustion attacks. The two high-severity issues are CVE-2026-113874, involving insufficiently protected tenant-partition routing, and CVE-2026-113873, involving compressed payloads that expand before authorization checks. CVE-2026-113875 and CVE-2026-113876 concern potential clinical-record exposure through subscription notifications and conditional-create requests, respectively.
Exploitability depends on deployment settings and security controls, particularly partition authorization in multi-tenant environments. Smile Digital Health said enabling partition security protects Smile CDR customers against CVE-2026-113874 and announced a November release to address CVE-2026-113873 and clarify partitioning documentation. Healthcare organizations using affected components should verify partition-security enforcement and confirm remediation plans with their vendors. Agarwal reported no evidence of exploitation or impact on real patient data.