Anubis Ransomware Affiliates Exploit CitrixBleed 2 to Hijack NetScaler Sessions
Active Exploitation · 2 sources · Updated 2d ago · First seen Jun 25, 2025
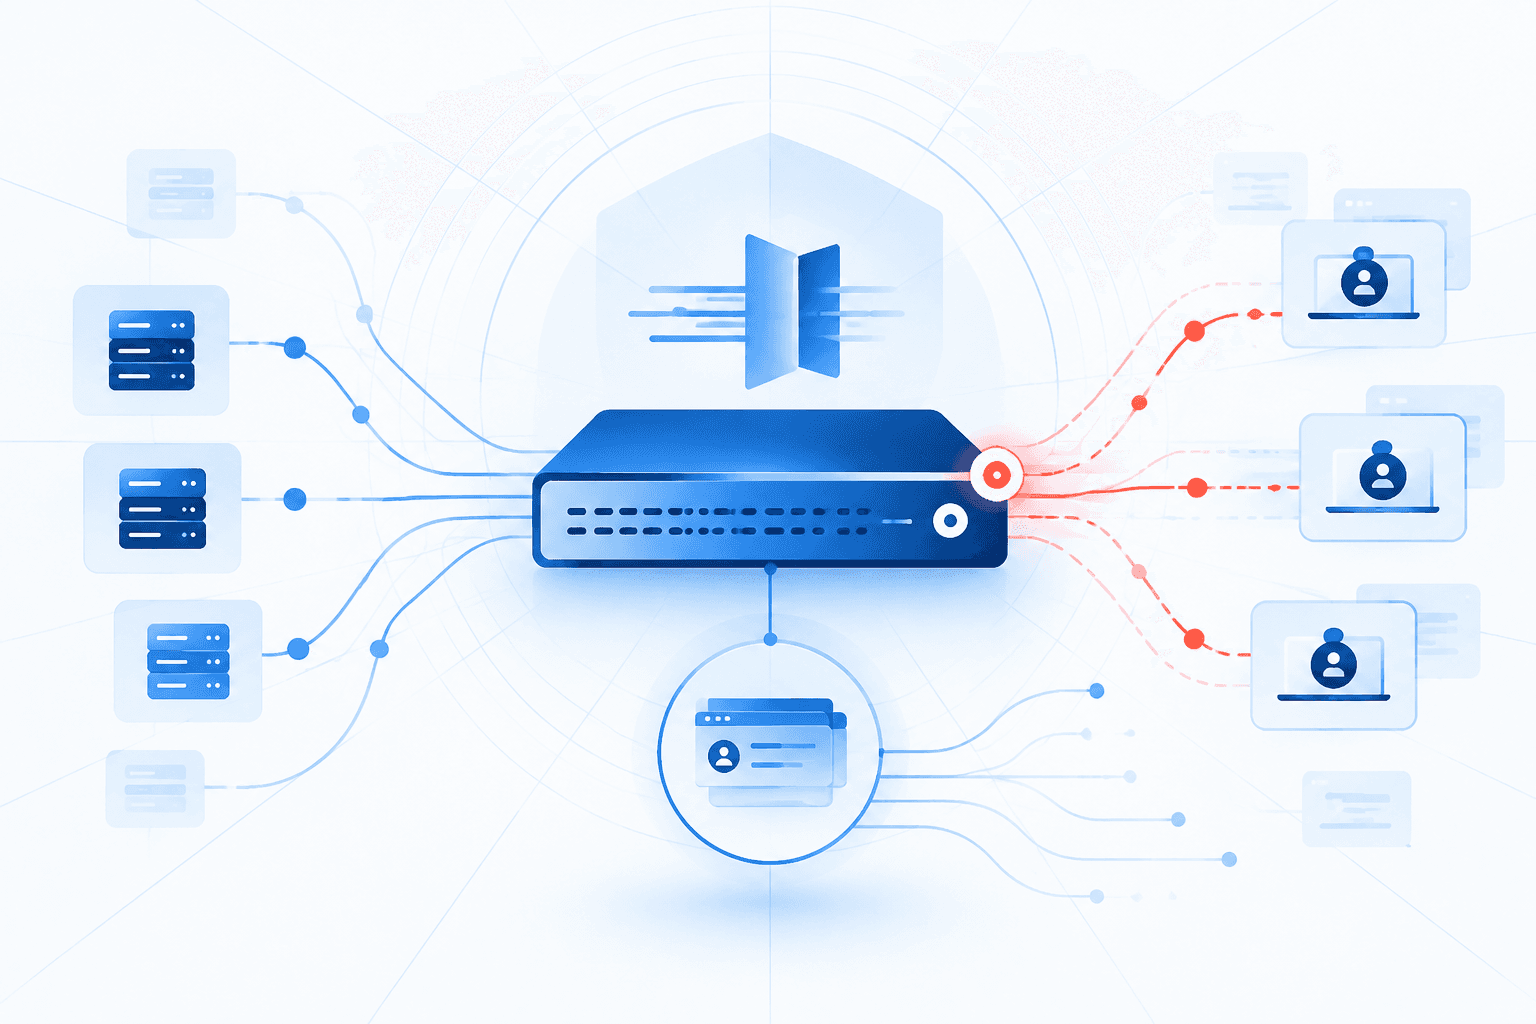
Anubis ransomware affiliates are exploiting CVE-2025-5777, known as CitrixBleed 2, in Citrix NetScaler ADC and NetScaler Gateway appliances to gain access to enterprise networks, according to SecPod. The memory-overread vulnerability affects appliances configured as Gateway or AAA virtual servers and can expose session material, enabling attackers to hijack authenticated sessions and bypass MFA. Affiliates then use remote administration tools, credential theft, lateral movement, tunneling, and cloud-based exfiltration before deploying Windows and Linux ransomware payloads. Anubis encrypts files with the .anubis extension and leaves ransom notes named RESTORE FILES.html.
CERT-FR separately warns of active exploitation of CVE-2025-5777 and CVE-2025-6543, another NetScaler vulnerability that can cause memory overflow, unintended control flow, and remote denial of service. The agency advises treating exposed appliances missing the relevant patches as compromised. Organizations should urgently upgrade affected appliances, terminate active ICA and PCoIP sessions after patching, and investigate renewed sessions and suspicious VPN activity; patching alone does not invalidate stolen sessions. CERT-FR also recommends password resets when patching occurred after public exploit code became available. Suspected compromises warrant evidence preservation, network isolation, credential and certificate revocation, investigation of connected systems, and rebuilding from a clean configuration backup. Restricting unauthorized remote administration tools and strengthening endpoint protections can help disrupt follow-on ransomware activity.