Windows WESP Exposes Telemetry to SYSTEM Clients but Preserves Tested EDR Protections
Vulnerability Disclosure · 5 sources · Updated 16d ago · First seen Oct 25, 2026
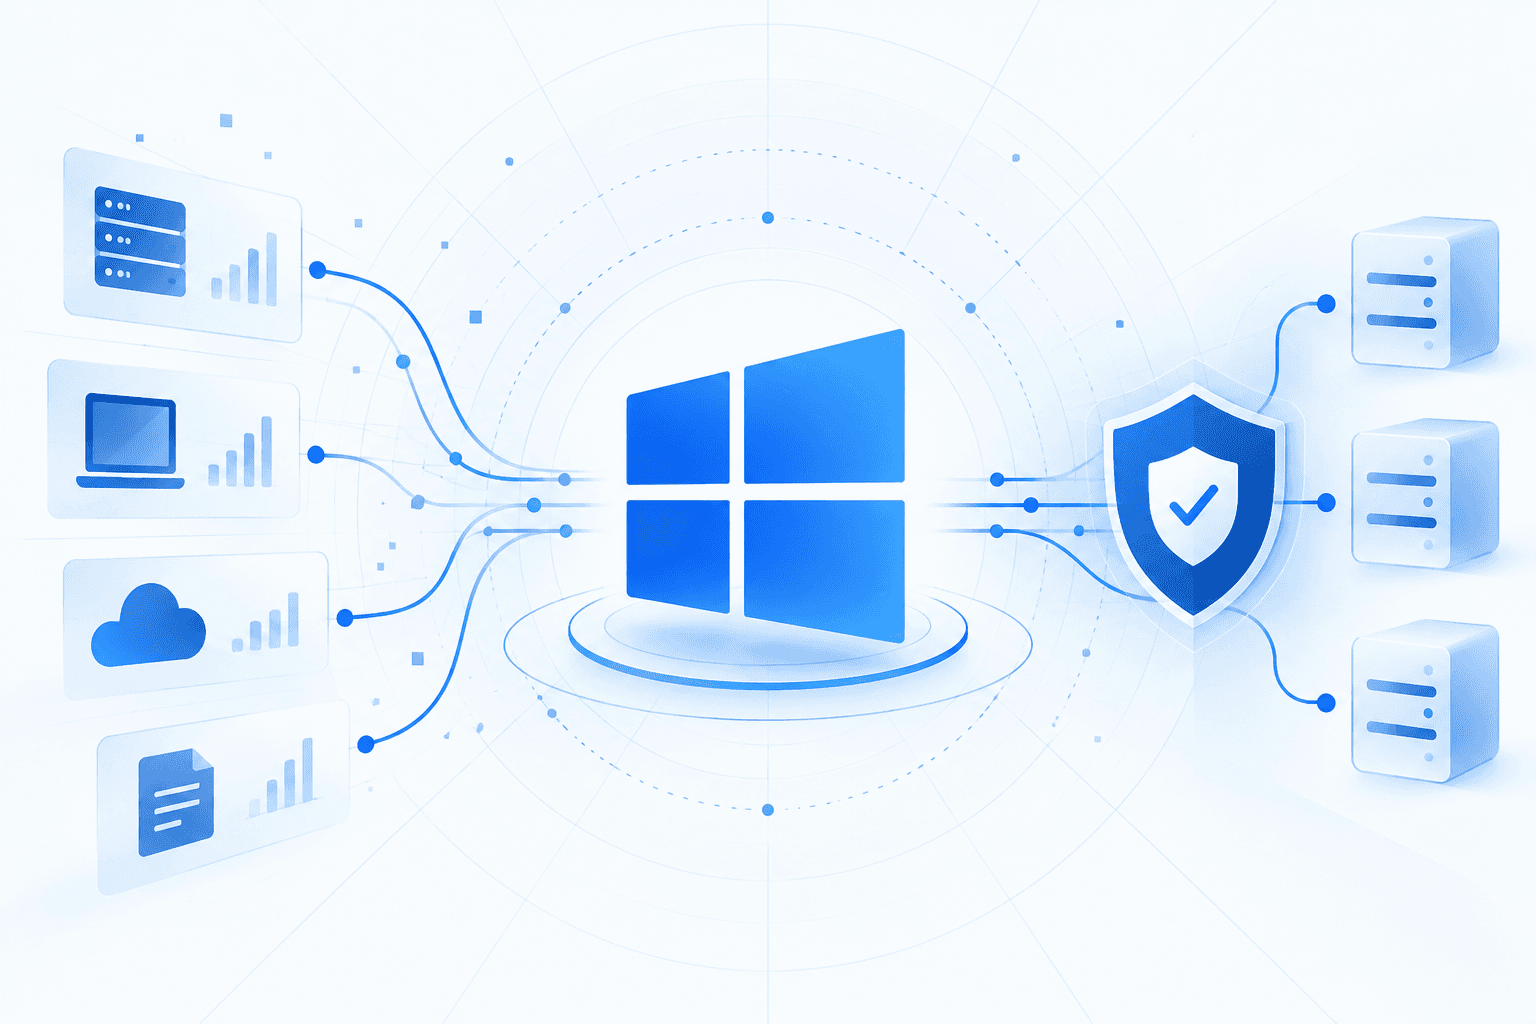
Research into Microsoft’s Windows Endpoint Security Platform (WESP) highlights both its emerging role in moving endpoint detection and response functionality out of the Windows kernel and its current security boundaries. Testing on Windows 11 Insider build 29695.1001 found that a SYSTEM process without Antimalware Protected Process Light (AM-PPL) protection could register as a restricted client, enumerate security products, and receive kernel-sourced telemetry without installing its own driver. These capabilities could enable surveillance and security-product fingerprinting by attackers who already hold SYSTEM privileges.
Kernel-enforced AM-PPL requirements and per-client isolation prevented restricted clients from installing blocking rules, suppressing another client’s telemetry, or unregistering a connected security client. The researcher also identified a potential weakness in an administrator-writable persistence store whose boot-time loader grants full trust without revalidating process protection, but did not demonstrate exploitation. WESP’s kernel ETW provider records registrations and related activity, although collection was not enabled by default on the tested build. Defenders evaluating WESP should assess that telemetry for monitoring unauthorized registrations; the findings are limited to one evolving Insider build and do not establish a memory-corruption flaw or successful EDR enforcement bypass.