Convertr Analytics Script Compromise Exposes Merchant Checkouts to Card Skimmer
Supply Chain Risk · 9 sources · Updated 6d ago · First seen Oct 26, 2026
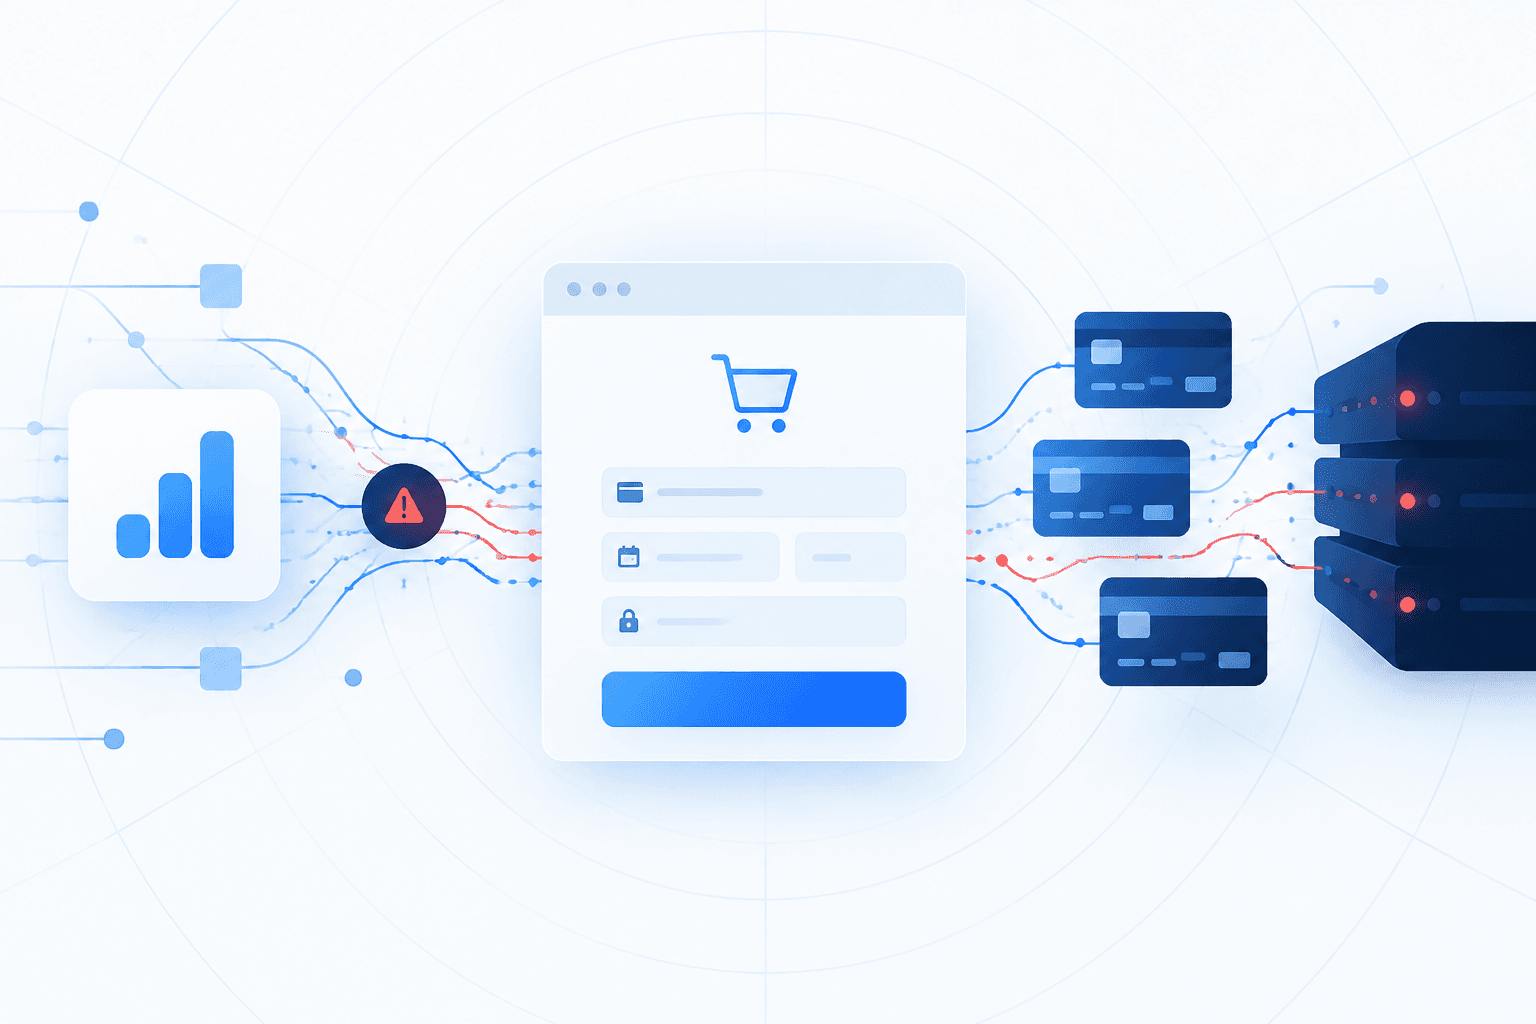
Attackers compromised a shared Plausible analytics script hosted by Brazilian e-commerce platform Convertr, exposing checkout pages at dozens of Brazilian fashion brands to a payment-card skimmer. Sansec detected the infection on October 24 and attributed it to a Brazil-focused Magecart group tracked since July 2024, calling it the group’s first observed supply-chain attack. The malicious script collected card numbers, expiration dates, CVVs, cardholder names and Brazilian CPF taxpayer identification numbers, exfiltrating them to https://1x0.is/ws when shoppers placed orders. By October 26, an updated version was tailored to Convertr’s payment API fields.
On October 27, Sansec confirmed that Convertr had removed the skimmer and upgraded Plausible to a patched version; Convertr said it was notifying affected merchants and payment providers. Investigators suspect exploitation of CVE-2026-8467 in Convertr’s outdated Plausible Community Edition installation, but could not confirm the entry point without server logs. Sansec warned that browser caches could retain the malicious script for up to 24 hours after cleanup and advised potentially affected cardholders to contact their banks and block their cards.