Huntress Flags Trusted-Tool Abuse, Session Theft and ClickFix Infostealer Attacks
Attack Tradecraft · 2 sources · Updated 2d ago · First seen Oct 27, 2026
Attackers targeting small and midsized organizations are exploiting trusted administrative tools, authentication flows and routine user workflows, according to Huntress. Its threat ranking identifies remote monitoring and management tool abuse, mailbox manipulation and adversary-in-the-middle session theft as priority risks across its endpoint and identity telemetry. Other observed threats include EvilTokens device-code phishing, which targeted 344 organizations across five countries in 16 days, and FakeAgent, which distributed SectopRAT through a malicious Claude Artifact and reached 29 organizations in two days.
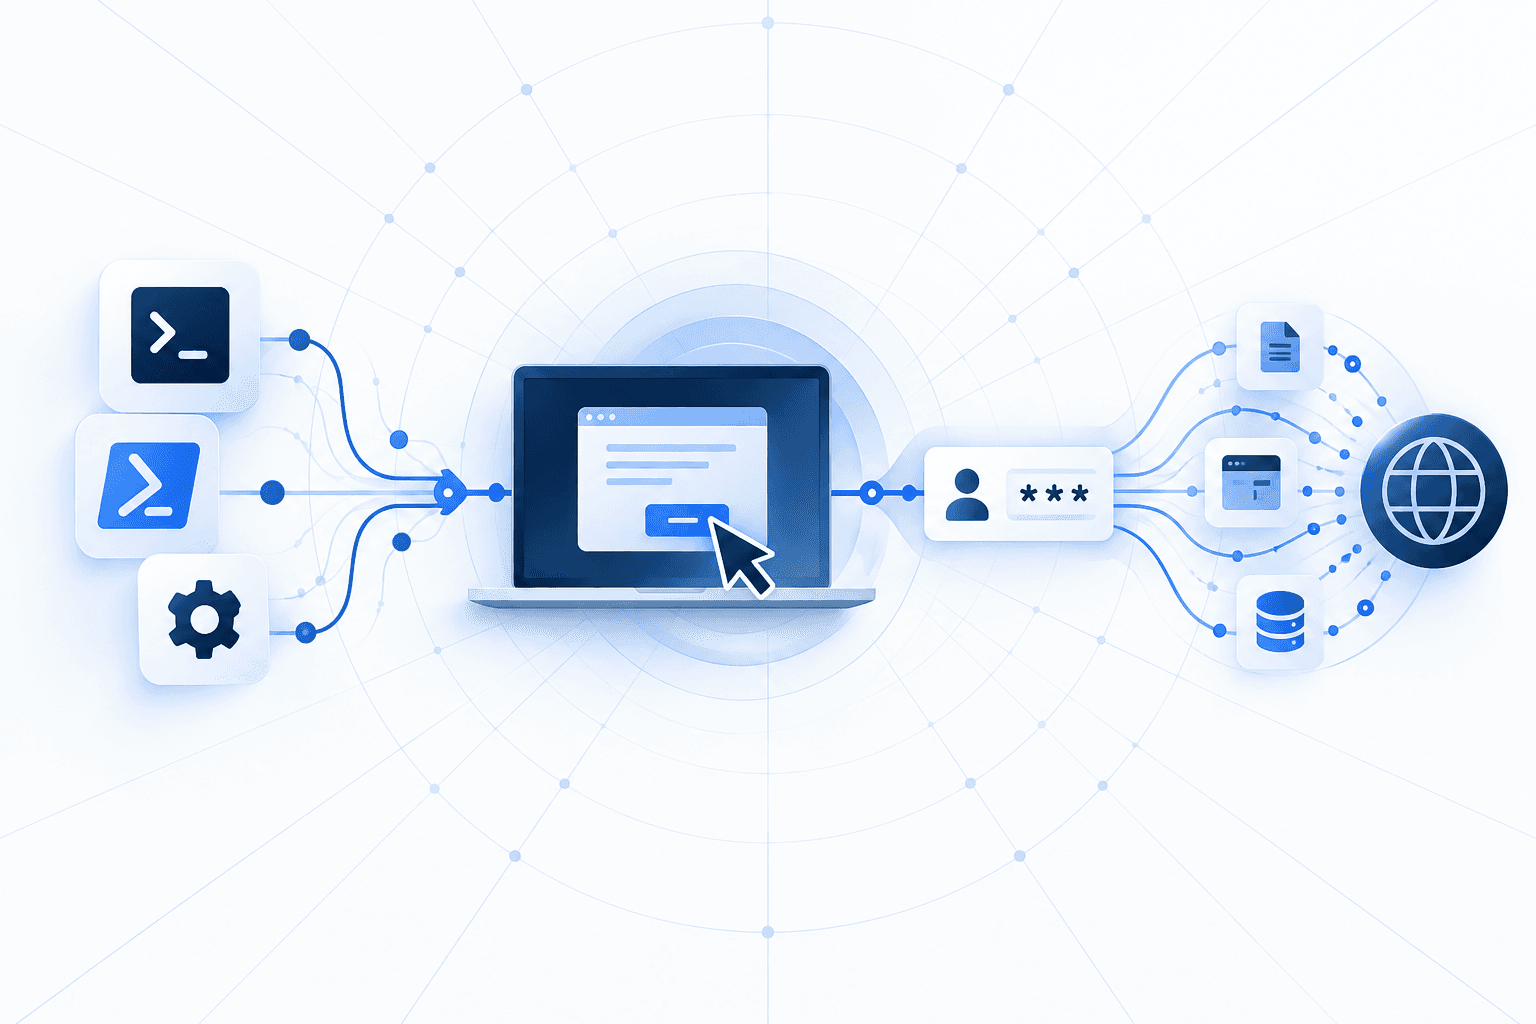
Separate Huntress research details a ClickFix campaign using fake human-verification screens and convincing full-screen Windows Update pages to persuade users to paste and execute a malicious command in the Windows Run dialog. The resulting infection chain uses the Windows utility mshta, an in-memory PowerShell stage and a .NET loader that extracts shellcode hidden in PNG pixel data, ultimately delivering infostealers including LummaC2 and Rhadamanthys. Later stages dynamically compile code and inject into processes such as explorer.exe. Defensive priorities include restricting remote access to approved tools, monitoring mailbox rules and anomalous sessions, and investigating unexpected device-code prompts and token activity. Organizations should also train users to reject web-page instructions to run commands and consider disabling the Windows Run prompt where operationally appropriate.