Fake Colombian Court Notices Deliver XWorm Through Scripts and RegAsm Injection
Social Engineering & Fraud · 2 sources · Updated 7d ago · First seen Oct 28, 2026
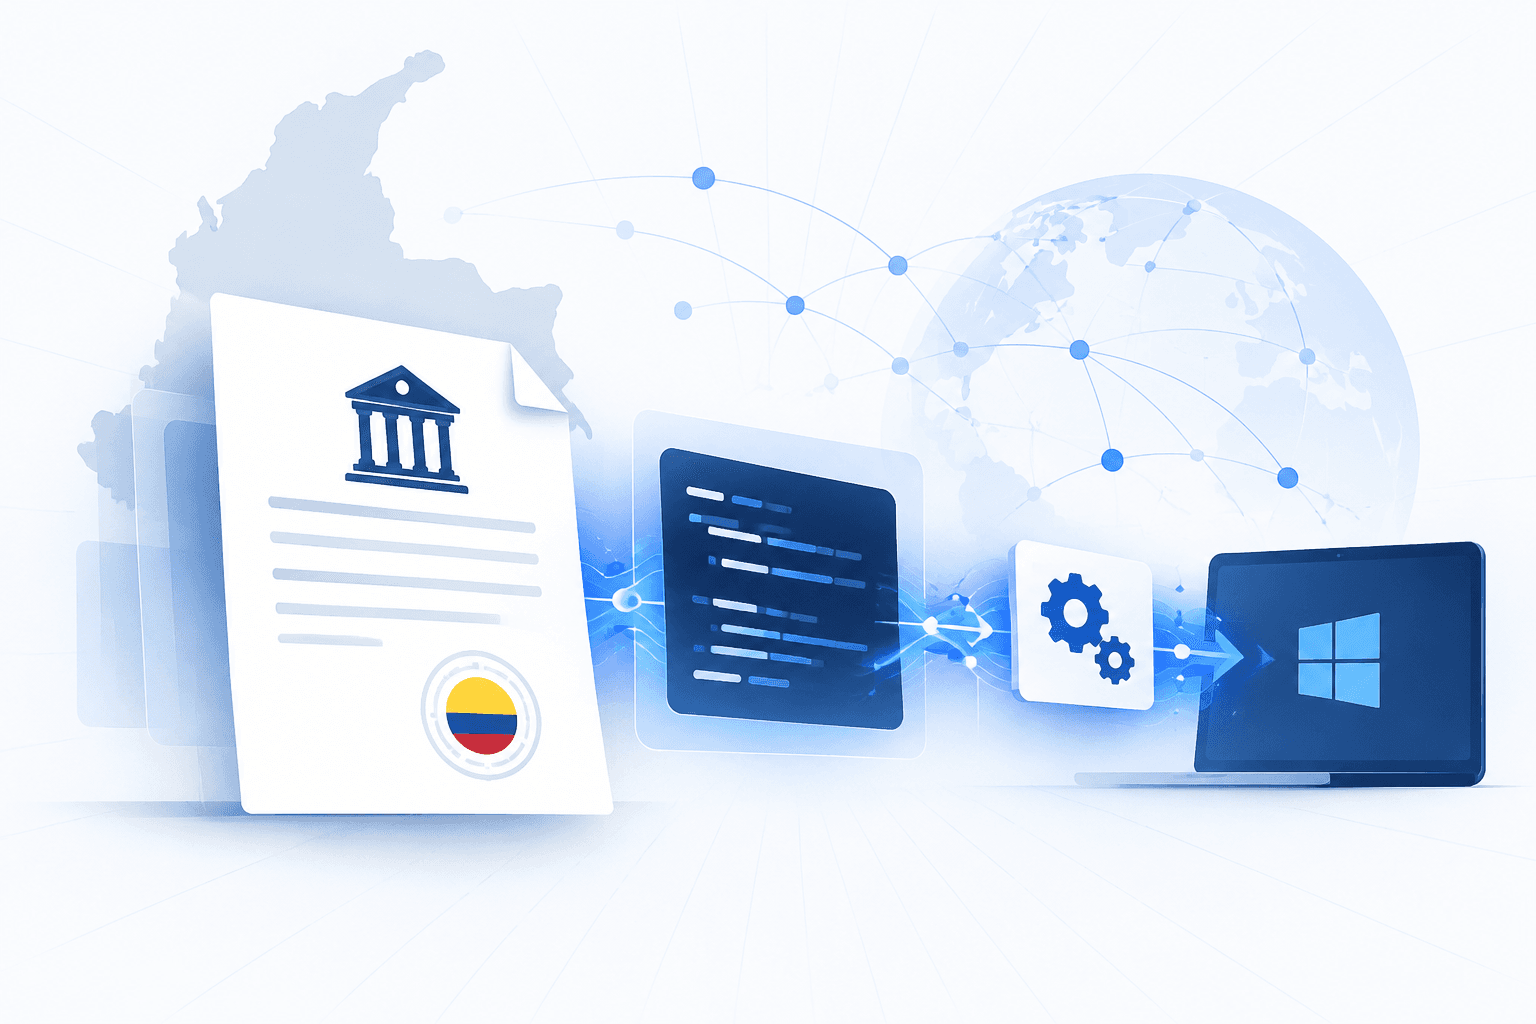
A phishing campaign is targeting Colombian organizations with Spanish-language fake court notices that deliver the XWorm remote access trojan through malicious VBScript and JavaScript attachments. The obfuscated scripts launch PowerShell to load the RSG_UnityApp .NET loader, which injects XWorm into the legitimate Windows process RegAsm.exe. XWorm collects system information and supports remote command execution, screenshots, file management, plugin loading, and distributed denial-of-service activity over encrypted command-and-control connections.
Arctic Wolf Labs identified infrastructure reuse across multiple builds and loader overlap with a September 2026 UK-linked XWorm case. The same loader also delivered DCRat in another sample, indicating tool reuse but not establishing a common operator or attribution to a named threat actor. Defenders should prioritize detection of script interpreters spawning PowerShell, investigate suspicious RegAsm.exe behavior, and monitor connections to the command-and-control infrastructure identified in the reporting.