Attacker Impersonates 32 AI Bots to Scan Websites for Exposed Credentials
Attack Tradecraft · 3 sources · Updated 2h ago · First seen Oct 28, 2026
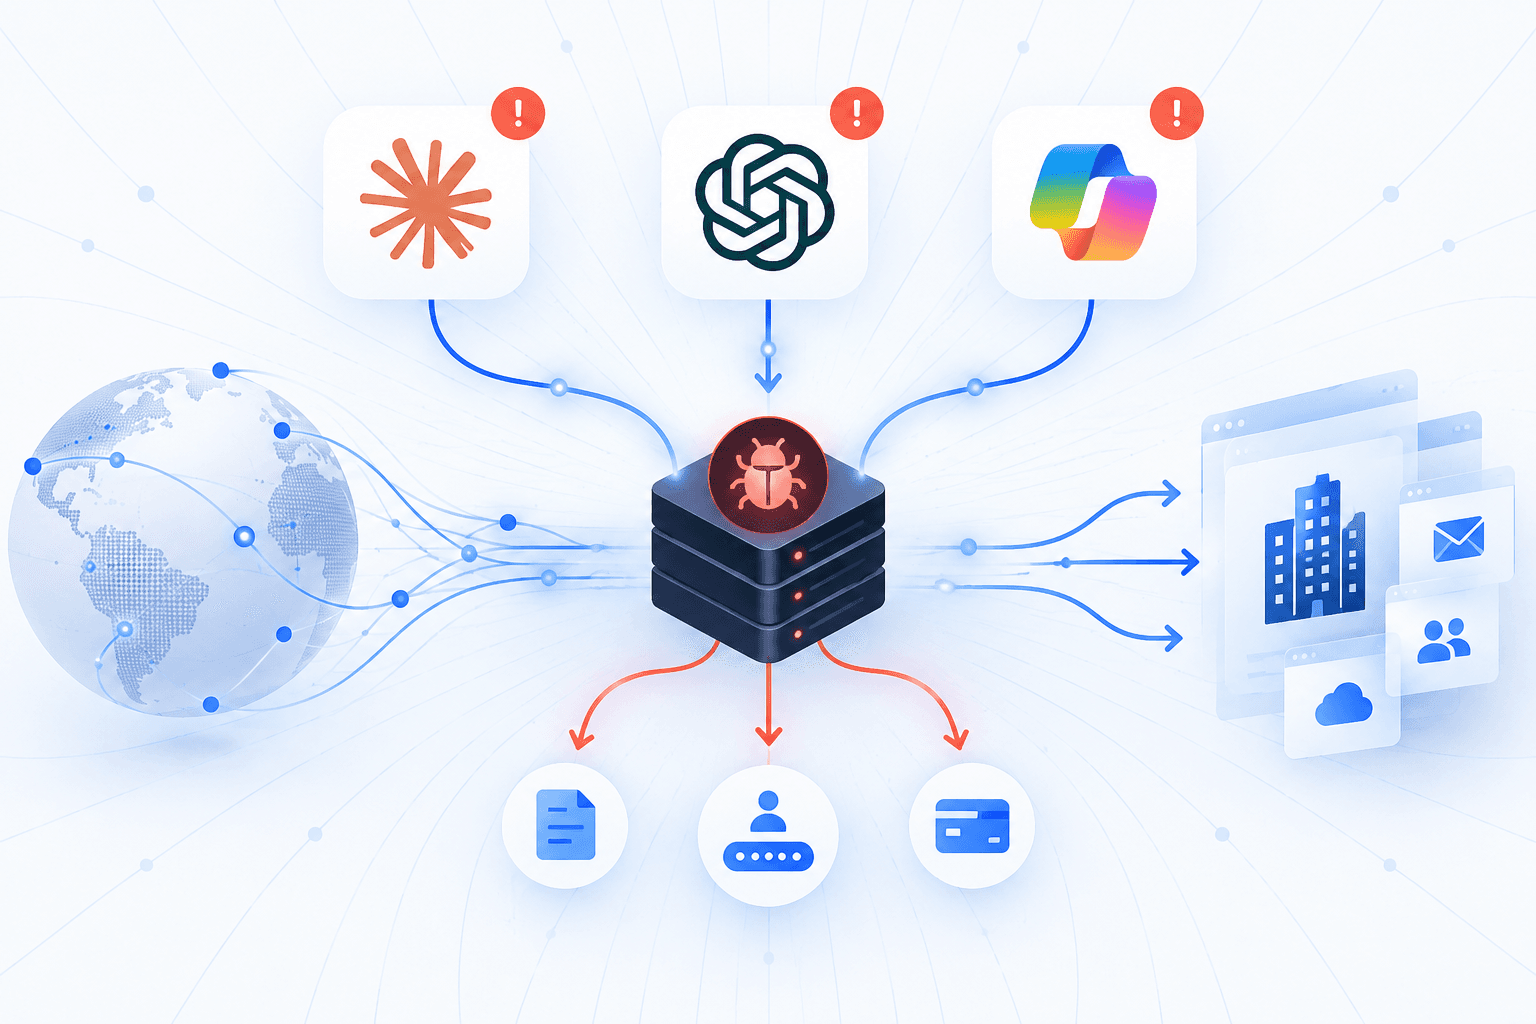
An unidentified threat actor impersonated approximately 32 AI bots, including ChatGPT, Claude and Perplexity, to scan websites for exposed credentials, according to Cequence Security. Active from at least late September through late October 2026, the campaign targeted roughly 90 file paths associated with environment configuration files, cloud credentials, private SSH keys and server environment data. On one October day, it reached 48% of Cequence-protected organizations receiving AI bot traffic, spanning financial services, retail, telecommunications, energy and software. Nearly all observed requests were blocked or failed; the reporting did not establish successful credential theft.
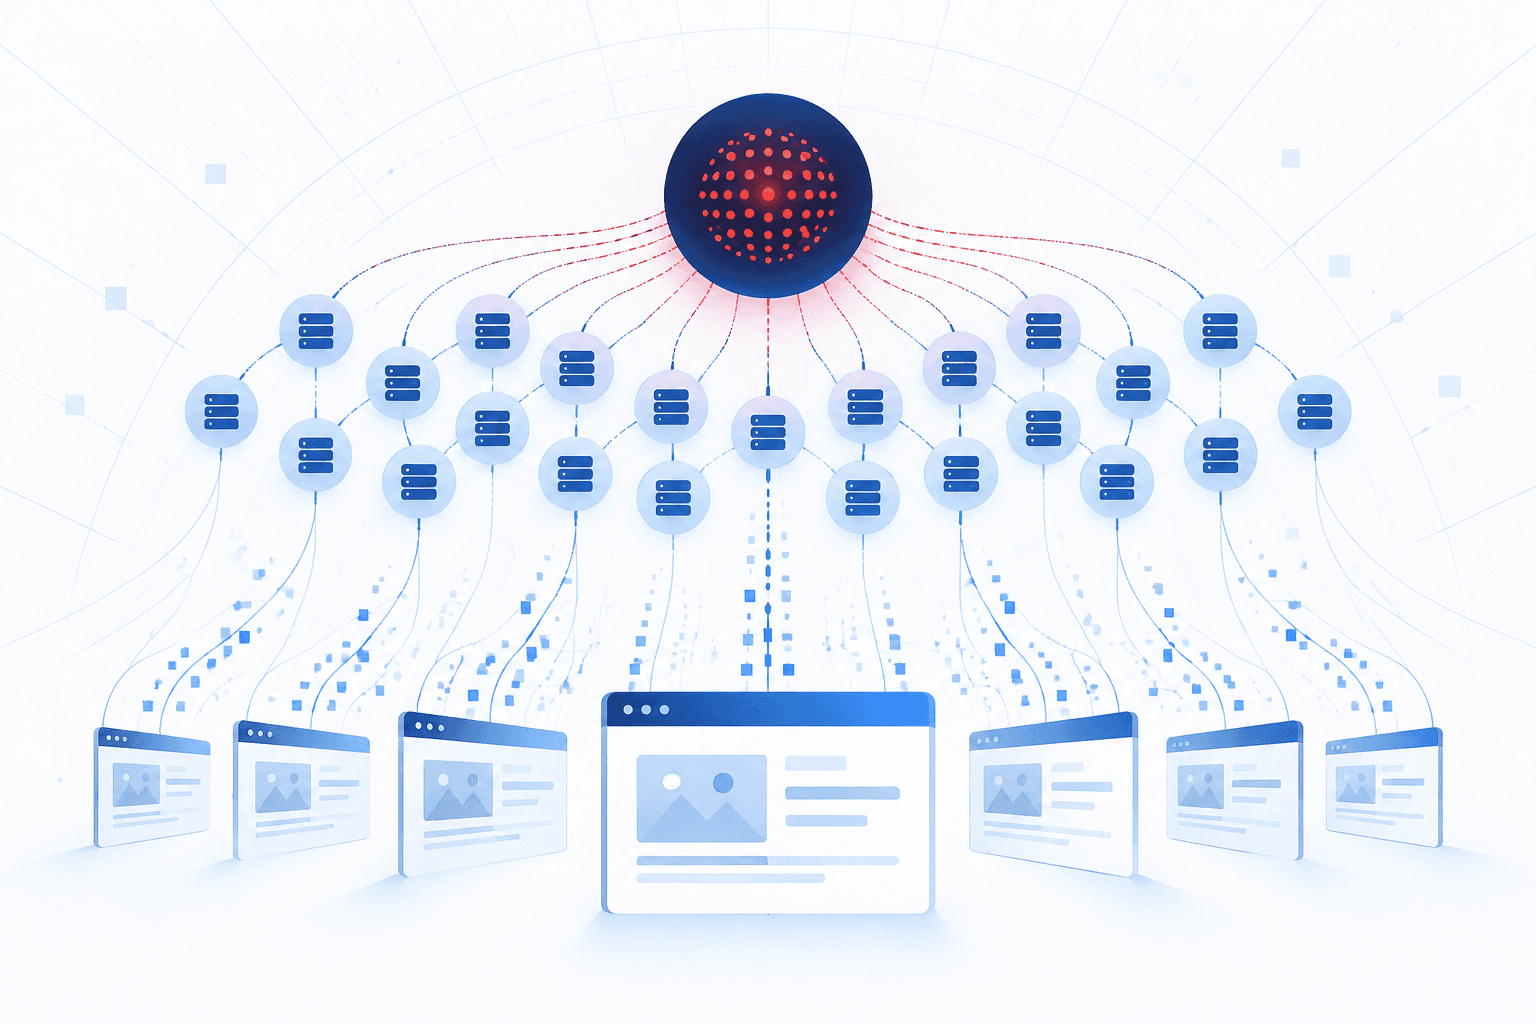
The scanner operated from a major cloud provider, rotating cloud IP addresses and bot identities while sending bursts of 50–190 requests in approximately eight seconds per address. It first requested random, nonexistent paths to identify sites that return responses for any requested location, then probed for sensitive files rather than behaving like a legitimate crawler. Separate Fastly research documented similar AI-bot impersonation activity. The findings highlight the risk of trusting self-reported bot identities: application and API security teams should independently verify purported AI agents, apply behavioral detection and prevent public access to secret-bearing files.