Volt Typhoon Used Silent Train Network to Evade Disruption and Target U.S. Infrastructure
Threat Actor Intelligence · 9 sources · Updated 2h ago · First seen Oct 28, 2026
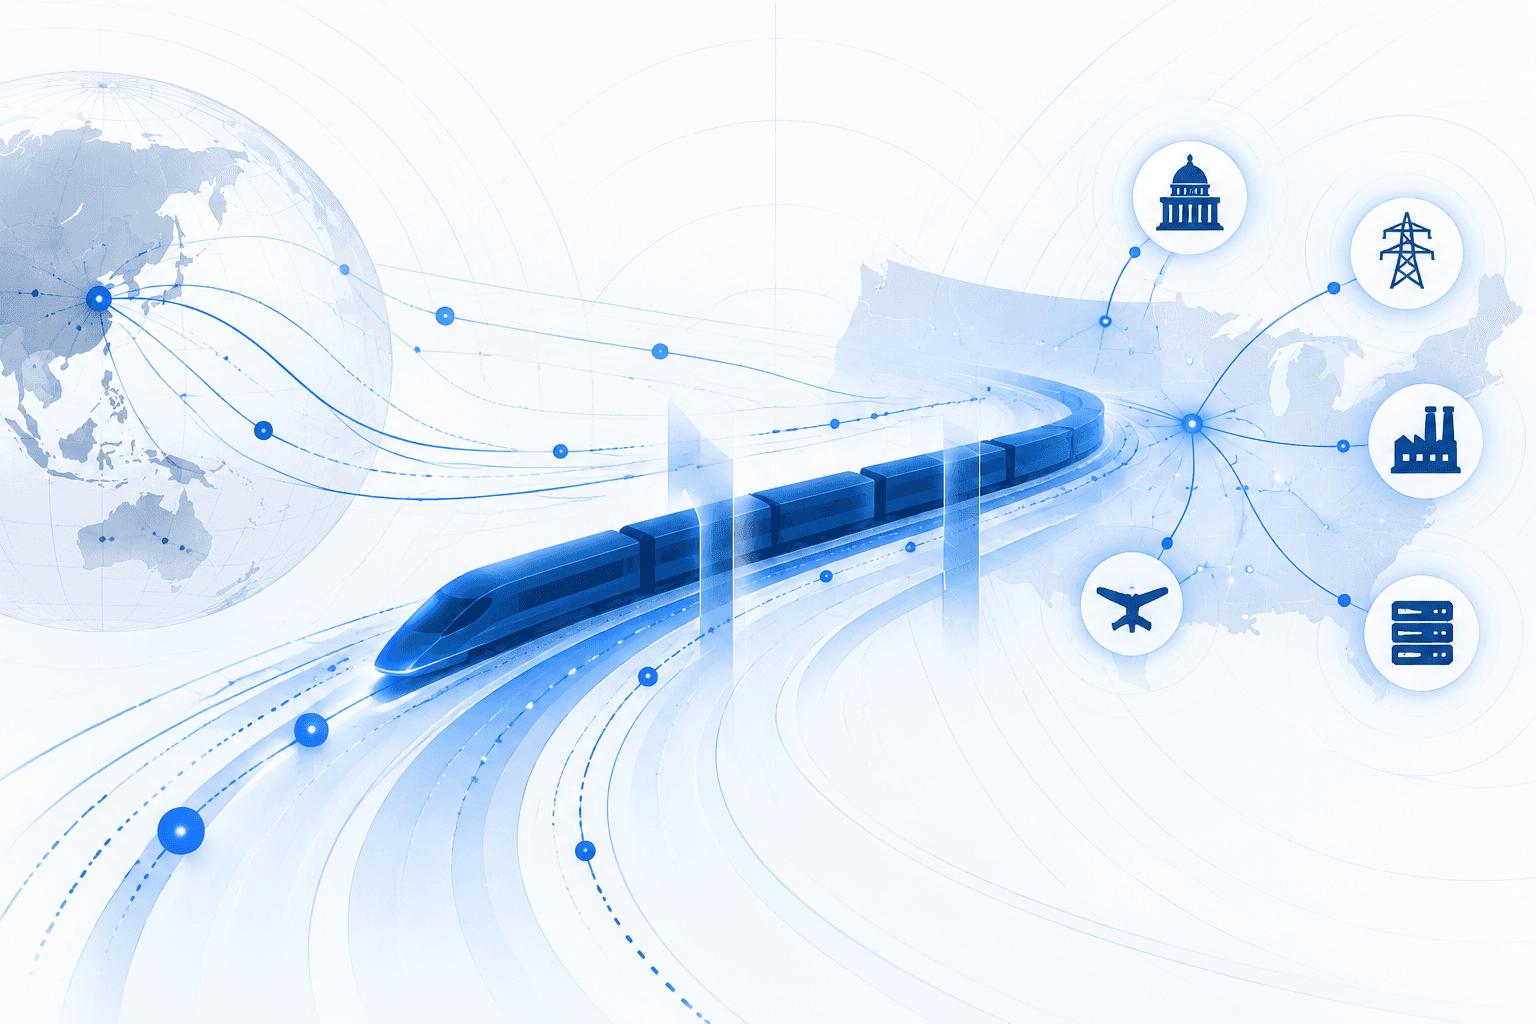
China-linked Volt Typhoon used a covert network dubbed Silent Train to sustain a three-year campaign against U.S. government agencies, defense contractors, telecommunications providers, universities, technology firms and critical infrastructure, according to Lumen Technologies’ Black Lotus Labs. Operating since late 2023, the network chained compromised routers, IoT devices and enterprise networking equipment to conceal attack origins and support targeting and confirmed compromises. The campaign continued despite the FBI’s December 2023 disruption of the group’s separate KV Botnet infrastructure. Lumen notified hundreds of victims across affected sectors.
Silent Train rapidly assembled and dismantled connection paths, with infrastructure chains rebuilt in under two minutes and sessions averaging roughly four hours. Extensive cleanup and compartmentalization limited visibility and made the operation resistant to a single network takedown. Targeting concentrated in Hawaii, California and Texas, which Lumen assessed as positioning for potential disruption of defense and infrastructure networks connected to the Indo-Pacific—not evidence that such disruption had occurred. Attackers also targeted enterprise management platforms. Some compromised devices had no known vulnerabilities, raising concerns about previously undiscovered exploits, although their use was not established.