Fake Adobe Acrobat and Signing Pages Deliver Attacker-Configured ScreenConnect Clients
Attack Tradecraft · 3 sources · Updated 10d ago · First seen Oct 2, 2026
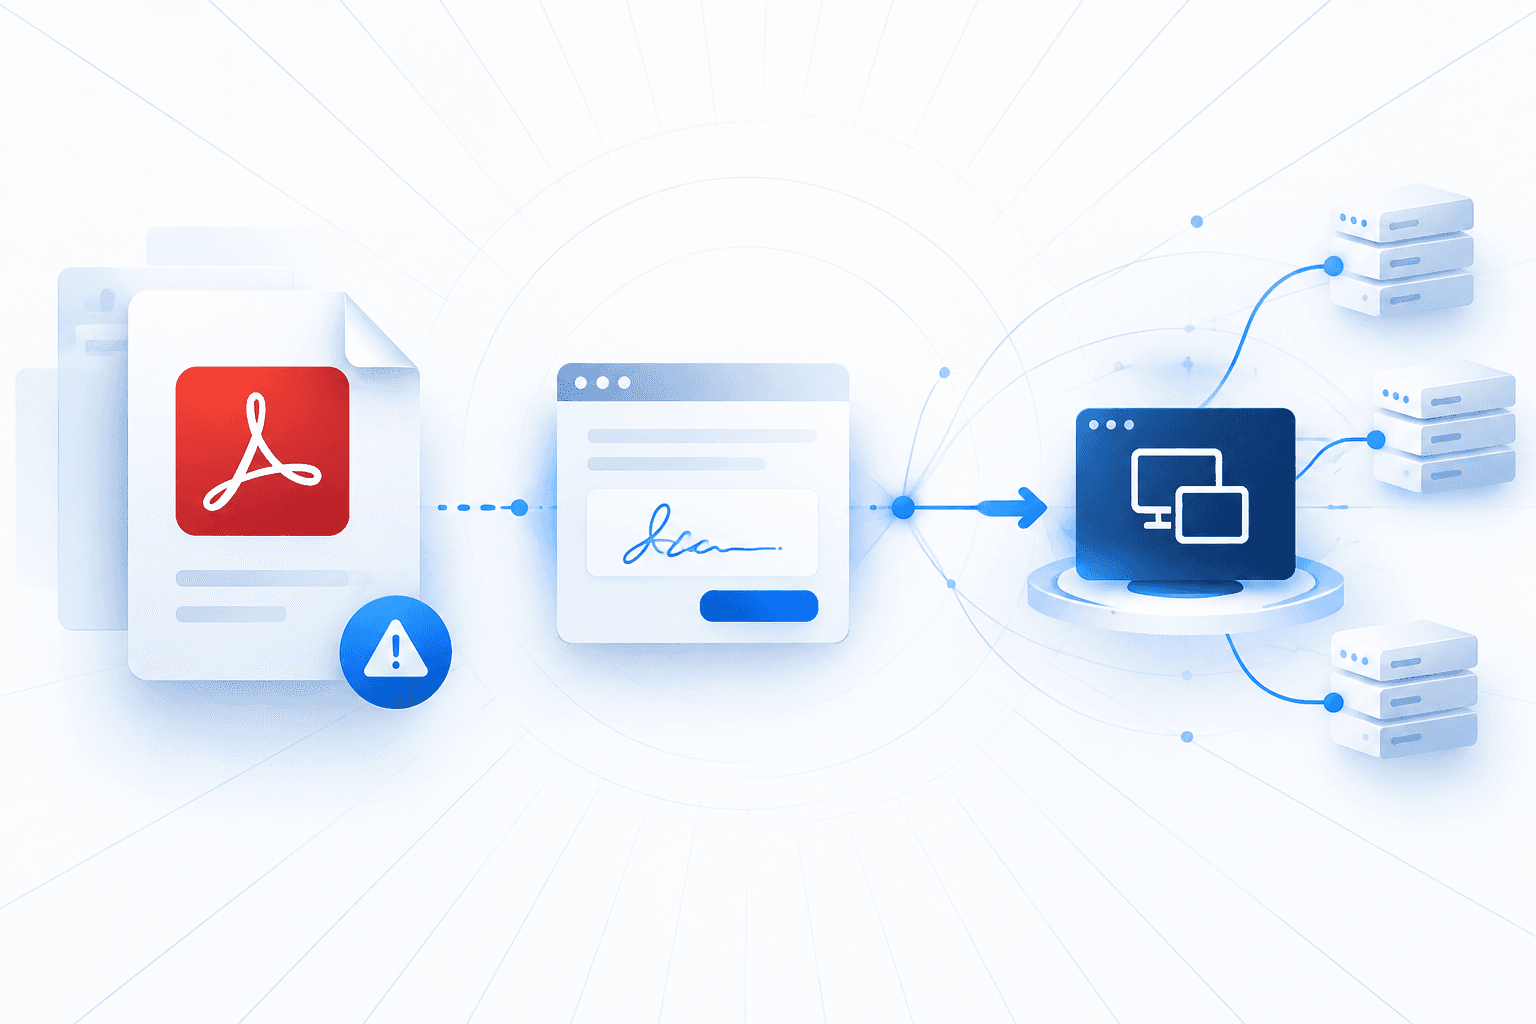
CloudSEK uncovered a campaign using fake Adobe Acrobat Reader and “View & Sign” document pages to distribute legitimate, digitally signed ConnectWise ScreenConnect clients configured for unauthorized remote-access tenants. Related pages profiled visitors by operating system, device type and ISP, sent visitor information to Telegram bots, and automatically downloaded tenant-specific clients for qualifying visitors. Researchers observed five ScreenConnect tenants, but did not establish the identity or number of operators.
Static analysis of two installers found no indication that they were trojanized, but their configurations could enable persistent remote access through automatically starting Windows services running with LocalSystem privileges. No victim compromise or credential capture was confirmed, and researchers did not execute the installers or conduct dynamic endpoint analysis. Defenders should investigate unexpected ScreenConnect services and connections, restrict installations to approved tenants, and prioritize tenant configurations over installer hashes or valid vendor signatures when assessing suspicious activity.