Eclypsium Demonstrates AI Model Tampering Through Compromised Infrastructure
Emerging Technology Risk · 10 sources · Updated 16h ago · First seen Oct 29, 2026
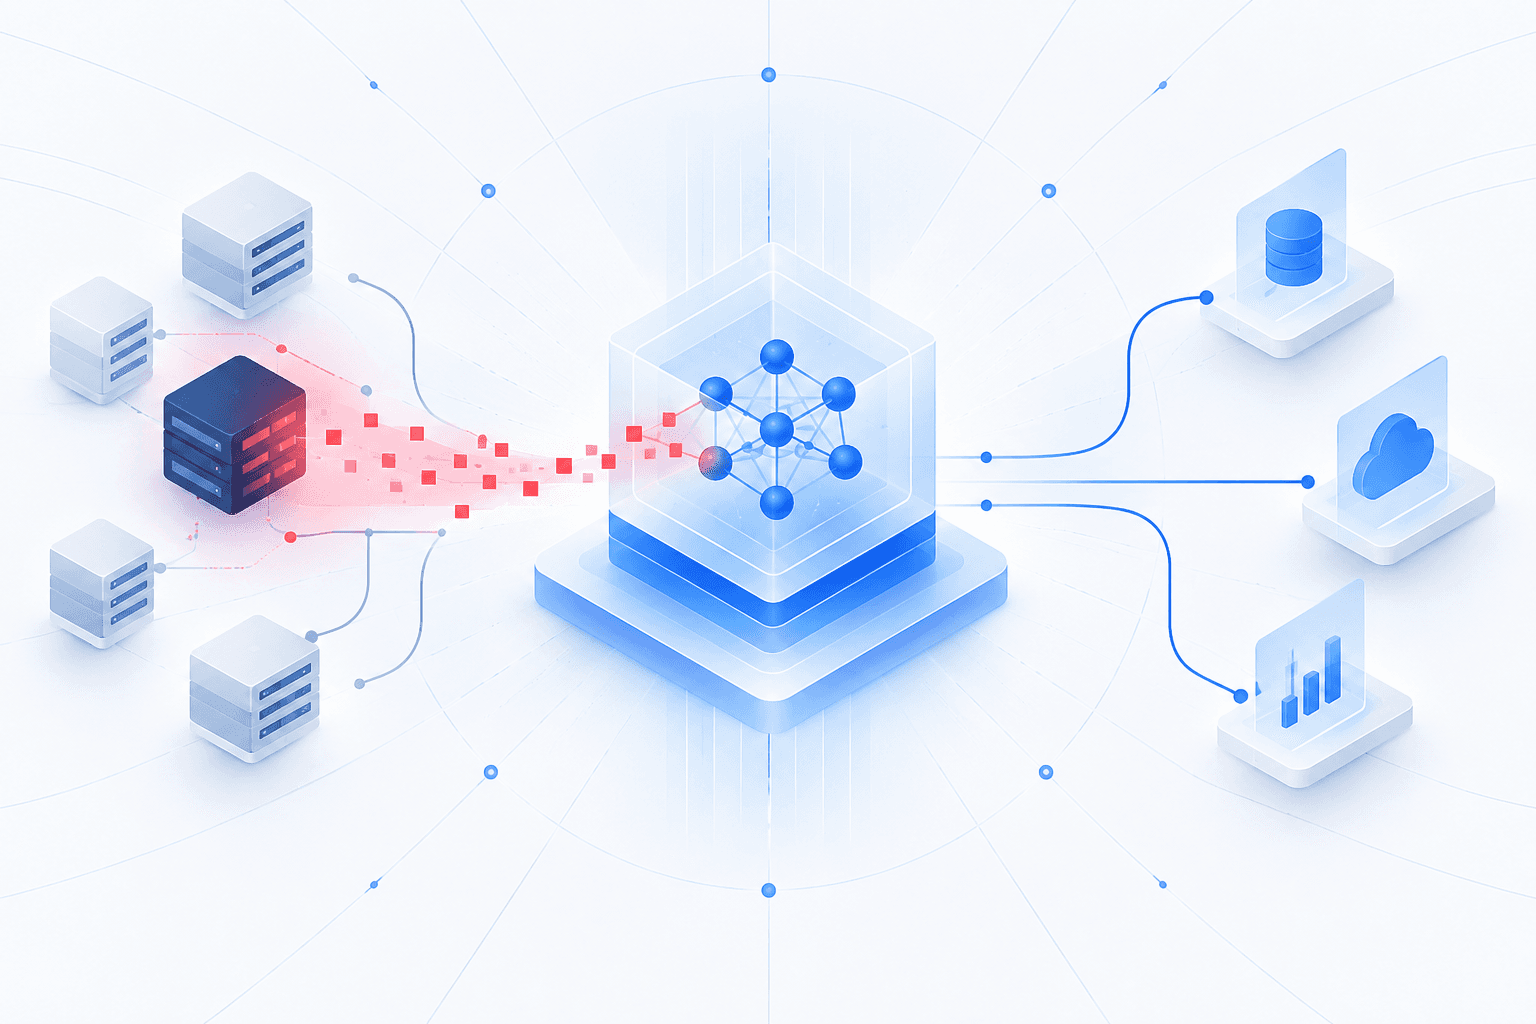
Eclypsium demonstrated that compromised AI infrastructure can alter model weights in memory and manipulate live inference outputs while leaving the stored model, its hash and signature valid. The controlled research on an NVIDIA computing platform showed models producing distorted assessments of a potential Chinese invasion of Taiwan and advising a user with chest pain to stay home rather than seek hospital care. The demonstrated attack path generally requires network access to a data processing unit or baseboard management controller, with certain security protections disabled. The research identifies no specific CVE, affected firmware version, confirmed victim or active malicious campaign.
Eclypsium and NVIDIA are collaborating to strengthen trust in AI infrastructure, emphasizing that stored-model integrity checks and secure boot alone cannot establish runtime integrity. Privileged components—including DPUs, management controllers and accelerator firmware—can expose model memory if access controls are inadequate, creating potential risks of model manipulation, theft and service disruption. NVIDIA said the demonstrations involve known industry risks and that strong memory-access protections can block the attack path; its BlueField platform provides hardware-rooted protections and configurable isolation. Organizations operating AI systems should verify memory-access restrictions, firmware integrity and infrastructure configurations continuously, and reassess those controls throughout the infrastructure lifecycle.