DPRK-Linked Contagious Interview Uses ErrTraffic Lures and Polygon-Based Malware Delivery
Attack Tradecraft · 2 sources · Updated 18d ago · First seen Sep 17, 2026
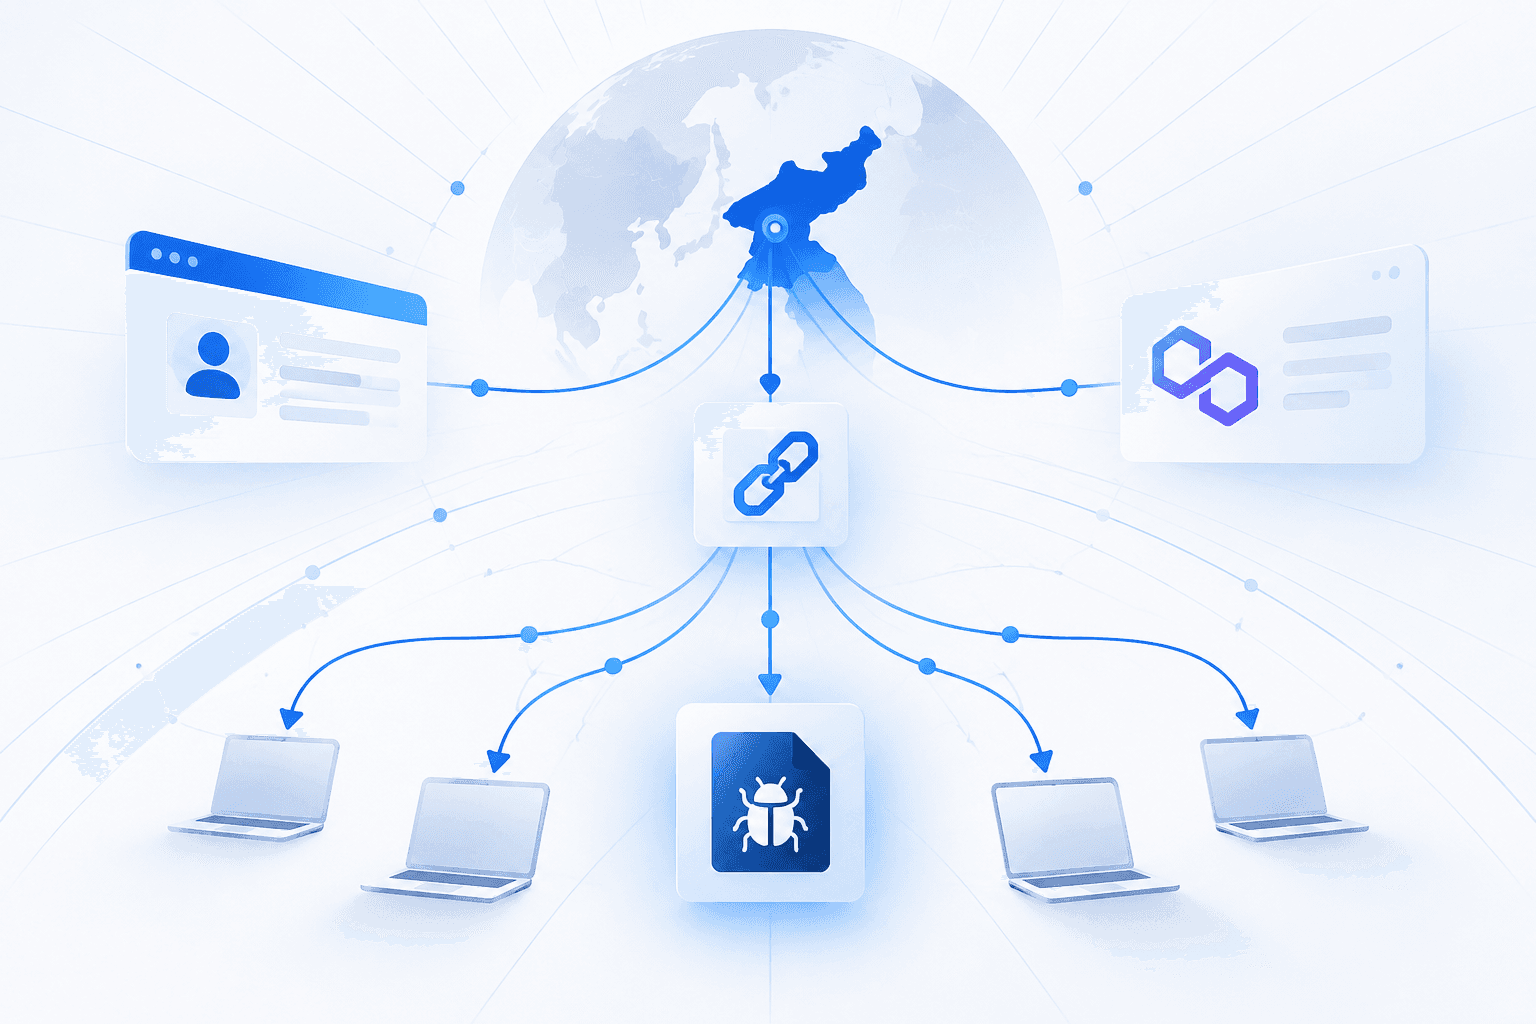
DPRK-linked Contagious Interview activity is combining fake recruitment lures with ClickFix delivery, according to research published by Newton Paul. Targets are asked to run GitHub projects or purported fixes during video interviews, while additional lures appear on compromised WordPress sites and a fake cryptocurrency company website. The WordPress overlays match Push Security’s description of ErrTraffic v3, a commercial ClickFix kit using Polygon-hosted configuration and separate Windows and macOS instructions. Shared infrastructure and delivery behavior connect multiple campaigns, suggesting the operators may be purchasing untargeted ClickFix traffic alongside their targeted recruitment operations.
The primary infection chain installs a portable Node.js runtime from the legitimate Node.js website and executes an obfuscated loader. A subsequent component retrieves its command-and-control address from a Polygon smart contract, downloads another stage and runs it in memory. The resulting remote-access trojan registers victims, deploys a keylogger labeled “Keyboard Sync Agent,” and obtains a DLL to decrypt Chrome passwords and cookies before exfiltration. Wallet analysis identified one funding wallet provisioning five contract-deployer wallets within two minutes, with contracts containing team-labeled C2 entries. A separate delivery chain distributes a full remote-control toolkit with hardcoded C2 infrastructure. Defenders should prioritize alerts for browser-to-terminal execution, unexpected Node.js installation and execution, and suspicious access to browser credential stores; blockchain-hosted configuration means static C2 blocklists alone may be insufficient.