VOLTA Infostealer Uses AI to Profile Victims and Prioritize Stolen Assets
Malware Intelligence · 4 sources · Updated 5h ago · First seen Oct 31, 2026
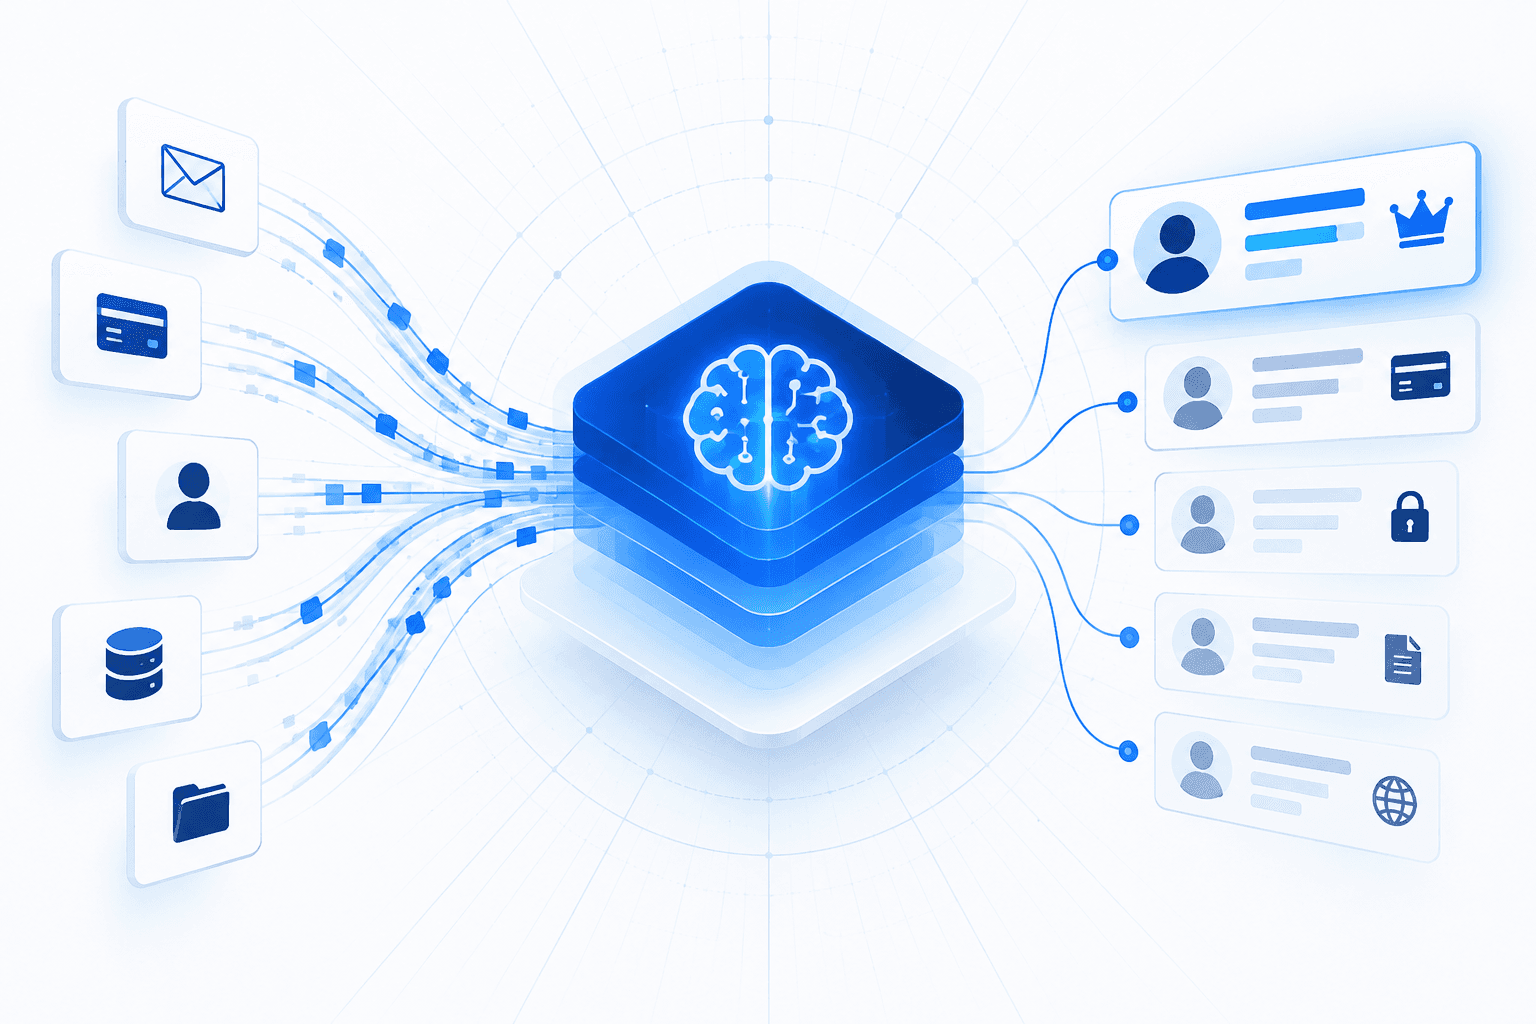
Cisco Talos identified VOLTA-AUTODOXER, a self-deleting Windows infostealer that combines credential and session theft with optional AI-assisted victim profiling. The malware collects passwords, authentication tokens, payment information, cryptocurrency wallet seed phrases, and active application sessions, then accesses compromised accounts to gather additional personal details. It submits a structured evidence bundle through OpenRouter to commercial AI models, generating citation-backed assessments of victims’ monetizable assets and security posture to help attackers prioritize targets and stolen information. A model fallback chain explicitly anticipates refusals from its preferred model.
Talos discovered the malware using its CAIRN framework but did not establish whether it had been deployed in the wild. Configurable build-time settings suggest a possible commercial malware-builder model, although that remains unconfirmed; the analyzed sample relies on third-party services rather than actor-owned infrastructure. Recommended defenses include restricting suspicious headless Chrome launches, preserving harvest logs for investigation, and revoking compromised credentials and sessions rather than relying on malware removal alone.