Mallory
← Back to News
loader-delivery-mechanismdefense-evasion-methodcredential-stealer-activitycommand-and-control-method

XLoader Campaign Uses Order-Themed Emails, LuaJIT and In-Memory Injection

Malware Intelligence · 4 sources · Updated 13d ago · First seen Nov 1, 2026
XLoader Campaign Uses Order-Themed Emails, LuaJIT and In-Memory Injection

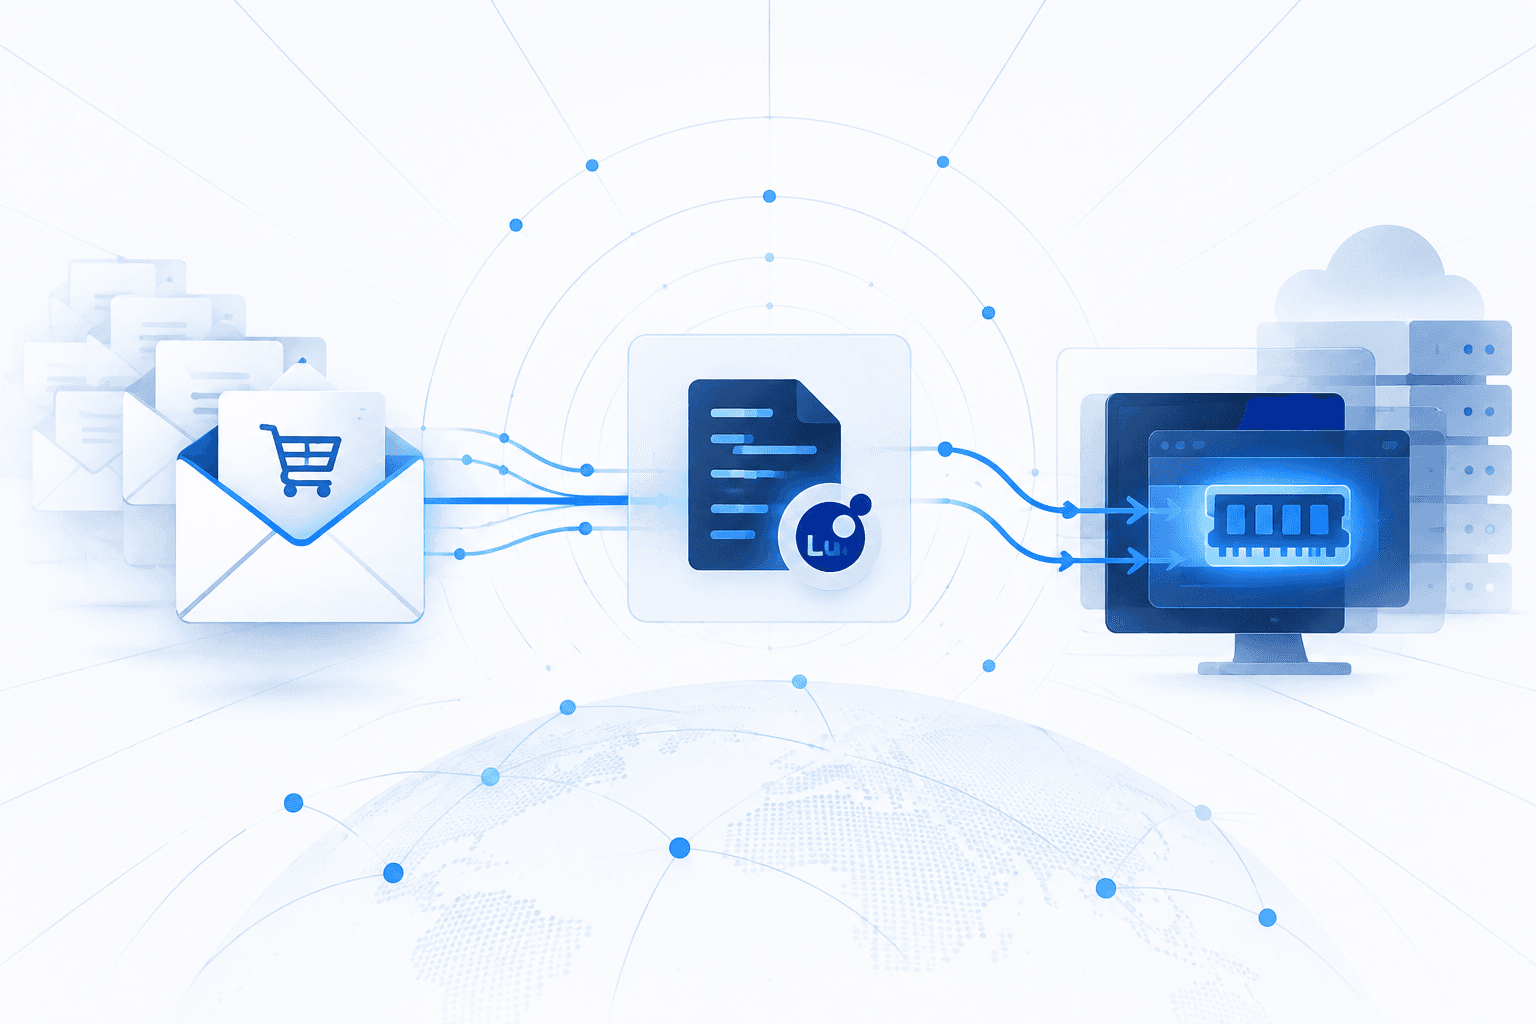
Morphisec investigated an XLoader campaign that used business order-themed emails and archives containing obfuscated JScript to deliver an embedded x86 LuaJIT interpreter, a Lua loader and an encoded native payload. The loader attempted to interfere with local security functions and manually mapped a packed executable into the LuaJIT process, where the packer decrypted and executed XLoader. The malware then transferred a cloned stage into another x86 process through shared-section mapping and thread-context redirection, rather than process hollowing. Recovered code supported network command processing, Windows Vault enumeration and cookie-record preparation. Scheduled-task persistence depended on a marker file; neither persistence creation nor successful security-function patching was confirmed in the analyzed chain.

Separate Zscaler ThreatLabz research into XLoader versions 8.1 and later documented increasingly complex runtime decryption, opaque predicates, stack-built parameters and obfuscated constants designed to frustrate analysis. The FormBook-derived malware steals credentials and sensitive data and supports follow-on payload execution, self-update and other remote commands. Its communications use plaintext HTTP carrying multiple RC4-based encryption layers, SHA-1-derived keys tied to the command-and-control URL, and Base64 encoding. ThreatLabz identified 65 runtime-decrypted C2 IP addresses, including decoys, with randomized subset selection; Morphisec likewise found decoy endpoints that prevented identifying the actual C2 server from configuration alone. Defenders should prioritize suspicious email archives, unexpected LuaJIT execution and cross-process memory activity rather than relying solely on extracted endpoint lists.
Hunt this familyPull IOCs and campaign context straight into your stack.
Get the IOCs
Event timeline

How this story unfolded

Events from the most recent confirmed update back to the earliest known activity.

4 events
  1. Reported Nov 1, 202616d ago

    Morphisec uncovers LuaJIT loading and shared-section injection in XLoader chain

    Morphisec's analysis found that the JScript dropped an embedded LuaJIT executable and Lua loader, which manually mapped a packed payload that decrypted and executed XLoader in memory. XLoader then transferred a cloned stage into another x86 process through shared-section mapping and thread-context redirection rather than process hollowing; successful security-function patching and scheduled-task persistence were not confirmed.

    From Business Emails to XLoader: An Order Lure That Led to In-Memory Injection | Morphisec Blog
  2. Reported Nov 1, 202616d ago

    Morphisec observes increased XLoader activity using business-email lures

    Morphisec observed increased XLoader activity involving order confirmations, quotation requests, and invoice-themed messages; the broader campaign also delivered Agent Tesla, Remcos, and XWorm. An analyzed Greek-language order-confirmation email carried a RAR archive containing obfuscated JScript rather than an order document, without identifying a specific targeted organization.

    From Business Emails to XLoader: An Order Lure That Led to In-Memory Injection | Morphisec Blog
  3. Reported Mar 31, 20268mo ago

    ThreatLabz documents XLoader's encryption and command protocol

    ThreatLabz analyzed XLoader versions 8.1 and later, detailing layered RC4 encryption, credential-exfiltration requests, and commands for payload execution, updates, and host control. Its investigation also documented runtime endpoint selection and decoy servers that obscure the actual command-and-control infrastructure.

    Latest Xloader Obfuscation Code & C2 Protocol | ThreatLabz
  4. Reported Mar 31, 20268mo ago

    XLoader version 8.1 introduces stronger code obfuscation

    Beginning with version 8.1, XLoader added stack-built function-decryption parameters, XOR-obfuscated function prologues, and a more heavily obfuscated data-decryption routine. These changes hindered pattern-matching tools and automated static analysis.

    Latest Xloader Obfuscation Code & C2 Protocol | ThreatLabz
Linked entities

Related entities

Vulnerabilities, threat actors, malware, products, organizations, breaches, and observables Mallory has linked to this story. Indicator values are masked here and available in full in the app.

Open in app →

Malware

1 linked

Observables

51 linked

Indicator values are masked on this page. View all 51 in Mallory Domains, IPs, hashes, and URLs are exportable to your SIEM.

Do you run this?Pull the IOCs, campaigns, and victimology behind this family, ready to push into your SIEM and EDR.
Hunt This Malware
Mallory platform

See the full picture, correlated to your attack surface.

This page covers what’s public. Mallory adds the parts that aren’t: which of your assets are affected, which threat actors are using it right now, and what to deploy next.

Exposure mappingMap indicators from this story to your assets and identify affected systems in minutes.
Threat actor evidenceEvery observed campaign, victim, and pivot linked to actors named in this story.
Associated malwareMalware, exploits, and IOCs connected to the activity described here.
Detection signaturesYARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Scheduled alertsGet matching new stories delivered to your team as they break, not the next morning.
AI threadsAsk questions about this story and take action on the answers.