Claude Dispatch Flaw Reportedly Lets Browser Extensions Execute Commands on Linked Computers
Emerging Technology Risk · 6 sources · Updated 12h ago · First seen Nov 5, 2026
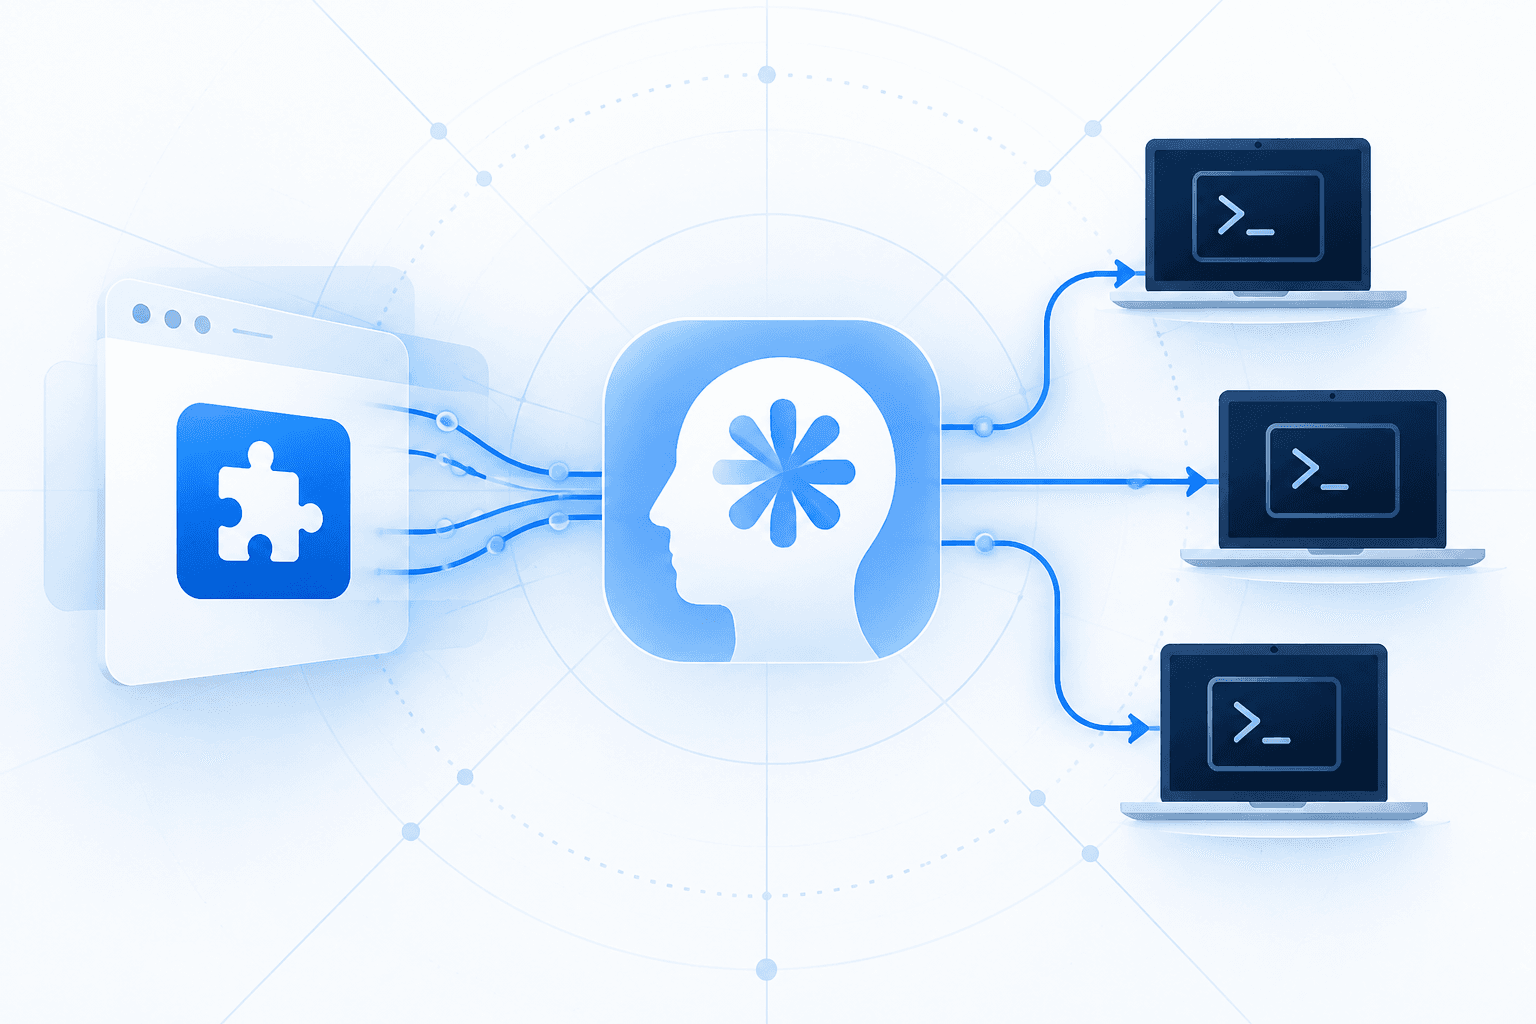
Forever Security researcher Gal Weizman disclosed ThisBash, a reported Claude Dispatch vulnerability that lets a malicious or compromised browser extension with access to claude.ai direct Claude Desktop to execute operating-system commands. Dispatch’s interface and API were accessible through an ordinary authenticated web session, allowing extension-issued commands to appear to come from the legitimate user. The demonstrated attack combined repeated prompting and automated approval clicks to install an npm package whose installation hook executed code, reportedly requiring no browser exploit and minimal user interaction.
The attack could reportedly reach another computer connected to the same Claude account, potentially bridging a personal browser and a corporate endpoint. Anthropic acknowledged the report in May as a valid duplicate vulnerability and reportedly planned to retire Dispatch, but the feature remained available to existing users as of October 30, with no fix reported. Weizman claims the underlying design weakness also affects Claude Cowork and Claude Code Remote Control, although the supplied reporting does not establish equivalent exploit demonstrations for those products. He recommends restricting web-originated access to desktop capabilities; organizations should review browser-extension permissions and Claude account connections across personal and managed devices.