Mallory
← Back to News
financial-sector-threatai-enabled-threat-activityinitial-access-methodlateral-movement-method

CRAFTY FALCON Uses AI Tools to Target Indian Fintechs and Manipulate Payments

Sector Threat Intelligence · 4 sources · Updated 12d ago · First seen Nov 5, 2026
CRAFTY FALCON Uses AI Tools to Target Indian Fintechs and Manipulate Payments

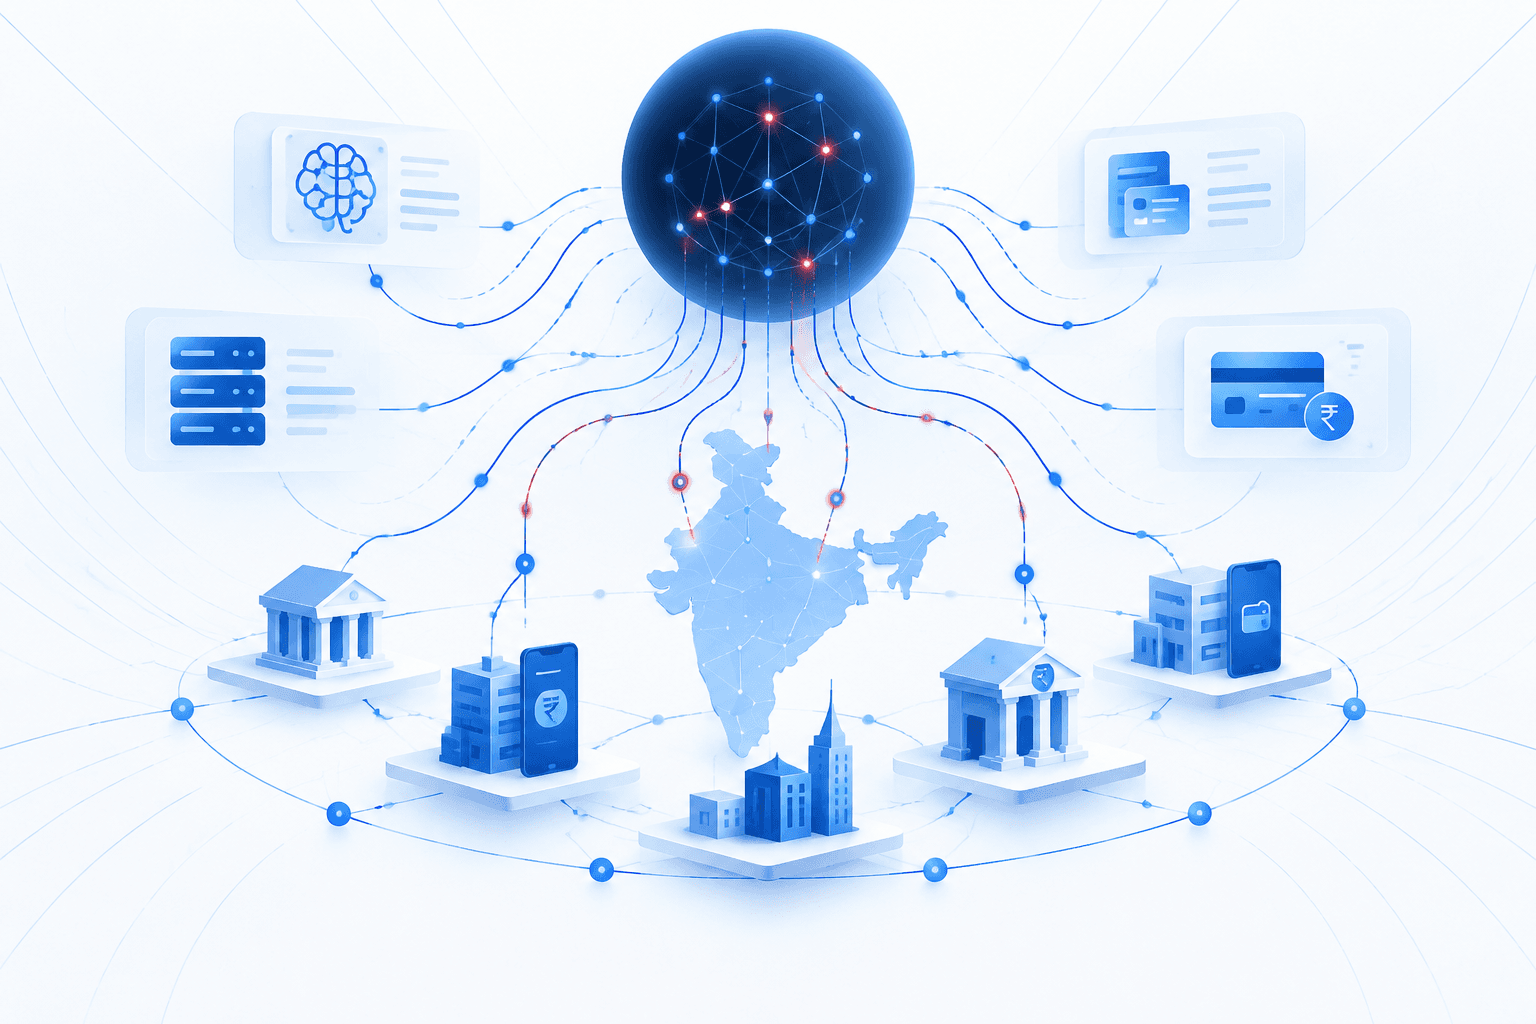
India’s Computer Emergency Response Team (CERT-In) warned of active, escalating attacks by CRAFTY FALCON against Indian fintech and financial services organizations. The financially motivated actor compromises internet-facing applications, exposed APIs and development or testing environments, then pivots into production through shared credentials or connectivity to initiate unauthorized transfers. Attackers test payment fraud with transfers of about $0.01, modify client applications, bypass IP allowlists through trusted fetcher services, abuse cloud management services and deploy web shells. Cryptocurrency businesses also face theft of wallet keys.

CERT-In and CERT-Fin observed the publicly available AI offensive tools ARTEX, CyberStrikeAI and Cairn in the attacks, alongside rapidly iterated code variants. Prior malicious use of these tools by China-based actors does not establish Chinese attribution for CRAFTY FALCON. The group targets weekends, holidays and other periods of reduced monitoring, and repeatedly attacks victims whose remediation remains incomplete. CERT-In recommended continuous monitoring and stronger logging, isolation of non-production environments, restricted cloud access, server-side API controls, rapid patching, cryptocurrency key protection and automated containment.
Who's targeting your sector?See the actors and campaigns active against you right now.
See sector threats
Event timeline

How this story unfolded

Events from the most recent confirmed update back to the earliest known activity.

4 events · Oct 2026 – Nov 4, 2026
  1. Reported Nov 5, 202612d ago

    Successful attacks continue after initial warnings and remediation

    CERT-In continued receiving reports of successful attacks after its initial advisory, including repeat compromises of previously targeted organizations. It identified incomplete remediation as a contributing factor.

    India Warns of New AI-Driven Cyber-Attacks Targeting Financial Sector - Infosecurity Magazine
  2. Nov 4, 202614d ago

    CERT-In warns of escalating AI-assisted CRAFTY FALCON attacks

    On November 4, CERT-In warned of repeated financial-sector attacks involving ARTEX, CyberStrikeAI and Cairn, with attackers pivoting from exposed testing environments into production to manipulate payment APIs and steal cryptocurrency wallet keys. The advisory detailed the actor's techniques and recommended stronger environment isolation, continuous monitoring, server-side transaction controls and automated containment.

    India Warns of New AI-Driven Cyber-Attacks Targeting Financial Sector - Infosecurity Magazine
  3. Oct 2026

    Financial organizations receive restricted advisory on payment API attacks

    Some affected organizations received a restricted-distribution advisory in early October warning that attackers were exploiting payment and disbursement APIs to conduct unauthorized transfers.

    India Warns of New AI-Driven Cyber-Attacks Targeting Financial Sector - Infosecurity Magazine
  4. Oct 2026

    CERT-In first detects attacks on Indian financial organizations

    CERT-In first detected attacks in October targeting Indian financial businesses, including digital lending platforms, fintech firms, payment service providers and wallet operators. The activity was subsequently attributed to the threat actor CRAFTY FALCON.

    Threat actor targets Indian fintechs on weekends when defenders aren’t watching
Linked entities

Related entities

Vulnerabilities, threat actors, malware, products, organizations, and breaches Mallory has linked to this story.

Open in app →

Threat actors

1 linked
Do you run this?See the adversaries and campaigns active against your sector right now, ranked by what they're exploiting.
See Your Sector's Threats
Mallory platform

See the full picture, correlated to your attack surface.

This page covers what’s public. Mallory adds the parts that aren’t: which of your assets are affected, which threat actors are using it right now, and what to deploy next.

Exposure mappingMap indicators from this story to your assets and identify affected systems in minutes.
Threat actor evidenceEvery observed campaign, victim, and pivot linked to actors named in this story.
Associated malwareMalware, exploits, and IOCs connected to the activity described here.
Detection signaturesYARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Scheduled alertsGet matching new stories delivered to your team as they break, not the next morning.
AI threadsAsk questions about this story and take action on the answers.