PhantomDOM Hijacks Microsoft 365 Sessions Through Attacker-Controlled Browsers
Social Engineering & Fraud · 2 sources · Updated 2h ago · First seen Nov 7, 2026
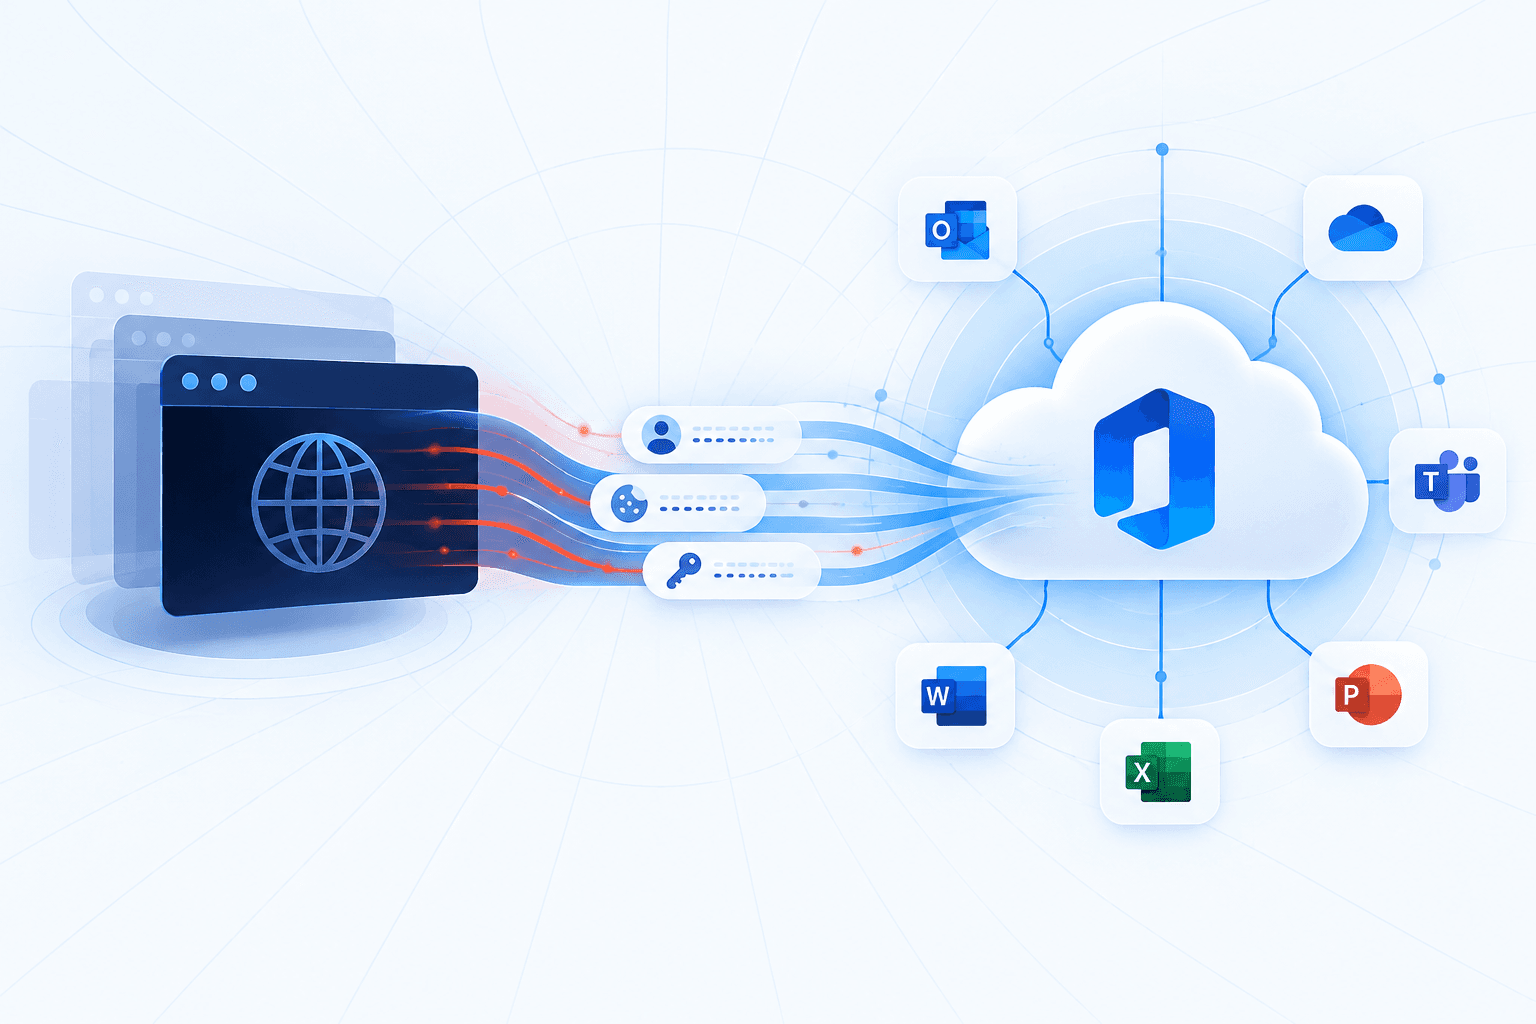
ZeroBEC uncovered PhantomDOM, a Browser-in-the-Middle phishing operation that uses SharePoint-themed PDF lures to hijack Microsoft 365 sessions. Victims interact with a locally reconstructed view of an attacker-controlled remote browser, where genuine Microsoft authentication takes place. A custom WebSocket protocol relays keystrokes, MFA input, clipboard content and other interactions, allowing attackers to retain authenticated access without endpoint malware or exploitation of a Microsoft vulnerability. Operator controls, resilient session handling and rotating infrastructure support the operation.
During a controlled investigation on November 4, researchers observed the attacker-associated session access two Outlook messages, reach Microsoft 365 Search and initialize Microsoft 365 Chat services, including OneDrive-backed Copilot Chat storage. Chat and Substrate LLM API token activity was consistent with normal application startup; researchers found no submitted Copilot prompt, staged document or completed passkey registration. The findings underscore the limits of phishable MFA for protecting business email and collaboration services. CISA’s guidance urges MFA adoption across services and prioritizes phishing-resistant MFA because weaker methods remain susceptible to phishing and other account-takeover techniques.