Critical FreeSWITCH SIP MESSAGE Flaw Reportedly Exploited to Run Server Commands
Active Exploitation · 7 sources · Updated 4d ago · First seen Nov 8, 2026
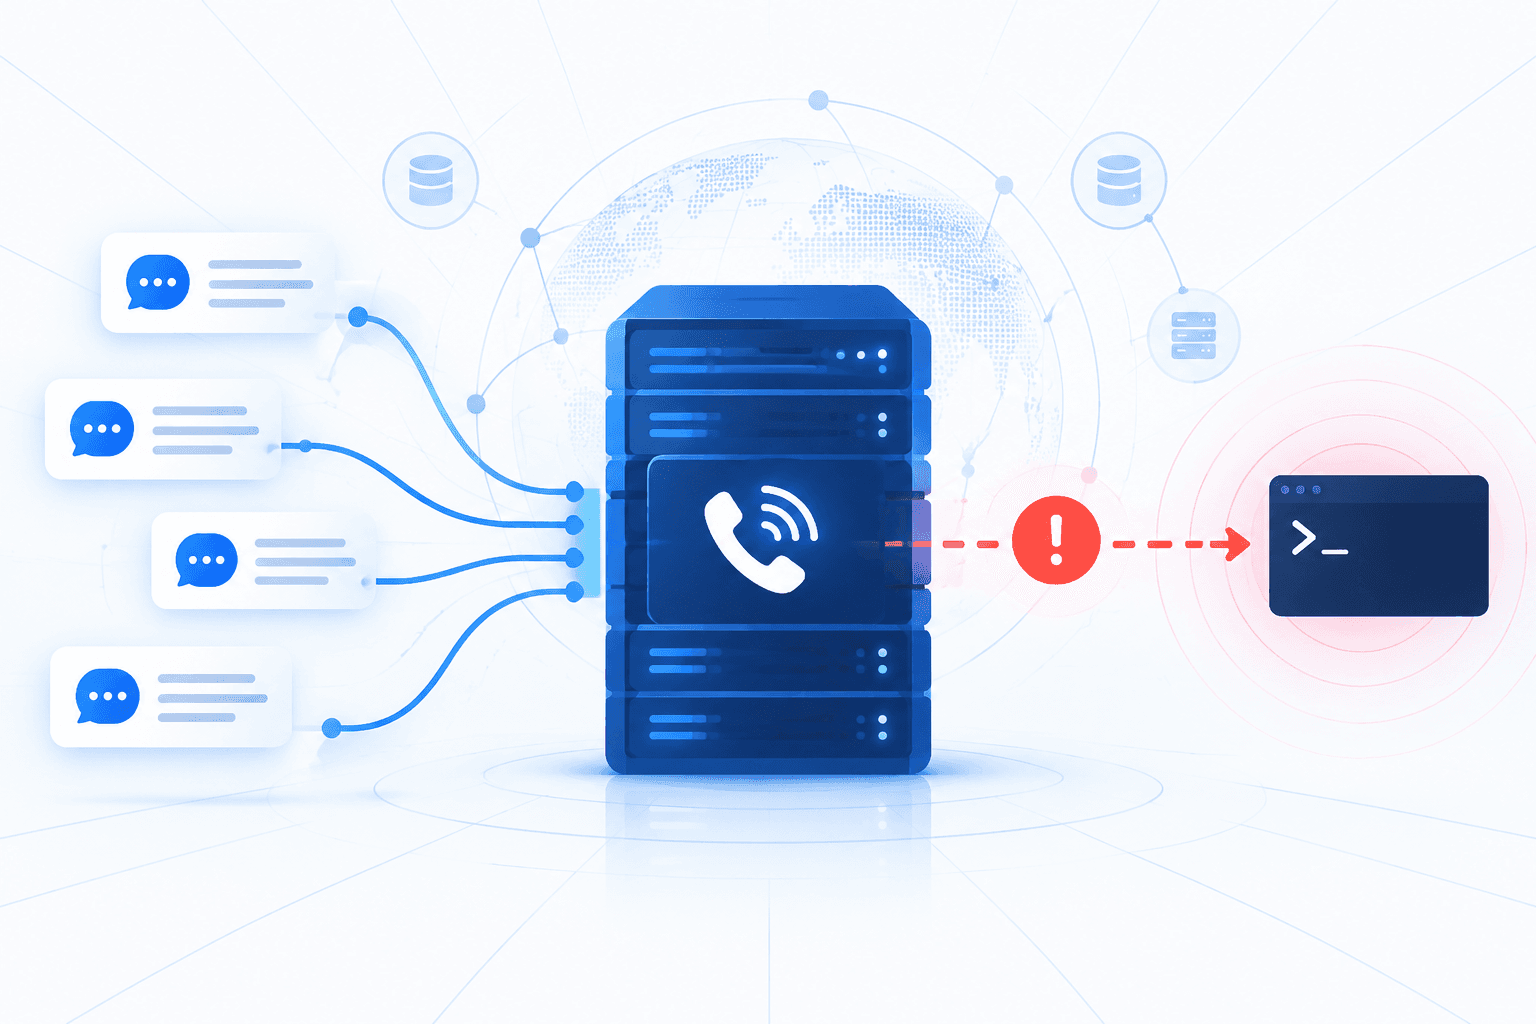
A critical FreeSWITCH vulnerability allows crafted inbound SIP MESSAGE traffic to select the API chat protocol and invoke server-side FreeSWITCH commands, potentially leading to operating-system command execution. SecurityOnline reports that attackers have exploited the flaw, identified as CVE-2026-116779 with a CVSS v3.1 score of 9.8; the supplied official advisory overview does not independently establish exploitation. SignalWire’s GitHub security page lists 10 advisories—one Critical, six High and three Moderate—published between October 26 and November 3, 2026. They cover SIP REFER channel-variable injection enabling command execution, memory-safety defects across several components, and delayed RTP/SRTP source validation that can cause one-way media starvation.
SignalWire’s FreeSWITCH 1.11.2 release announcement describes extensive hardening across the core, mod_rtmp, mod_xml_rpc and mod_sofia, including an interface allowlist, DTLS certificate verification against SDP fingerprints, stricter STUN validation and multiple memory-safety fixes. However, SecurityOnline recommends upgrading to 1.11.3 for the reported vulnerabilities and checking security settings rather than relying on an upgrade alone: it says the ICE integrity-check fix remains disabled by default. The report also identifies a WebSocket heap overflow and insufficient validation of incoming ICE connectivity checks, both rated 9.1, with potential consequences including memory corruption, audio redirection, and eavesdropping or injection on unencrypted calls. Administrators should prioritize exposed FreeSWITCH deployments and verify that the relevant protections are enabled.