
Mallory
← Back to News
phishing-campaign-intelligenceidentity-authentication-vulnerabilityai-platform-securitypersistence-method

BluePhishing Abuses Microsoft Entra Agent Blueprint Consent to Gain Tenant Access

Social Engineering & Fraud · 14 sources · Updated 6d ago · First seen Nov 9, 2026
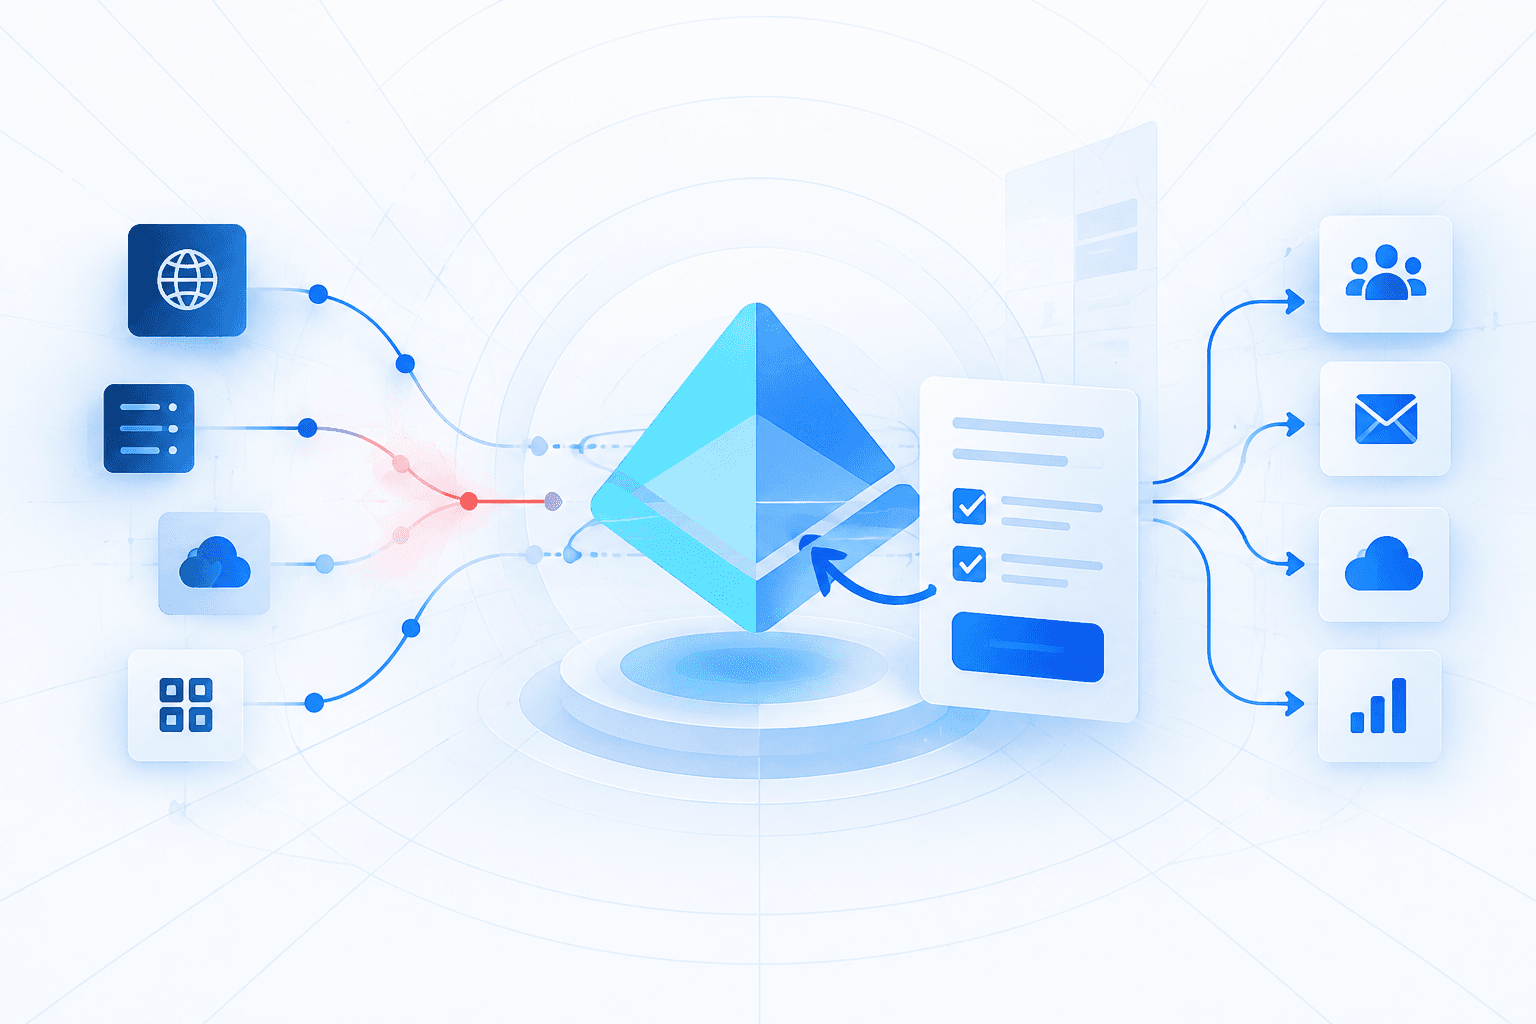
BluePhishing Abuses Microsoft Entra Agent Blueprint Consent to Gain Tenant Access

Proofpoint researchers demonstrated BluePhishing, a proof-of-concept extension of OAuth consent phishing that abuses Microsoft Entra Agent ID to gain access to a corporate tenant. The technique lures a user into consenting to a malicious third-party agent blueprint, establishing a blueprint principal in the victim’s tenant. An attacker can then use blueprint credentials and an automatically assigned identity-creation permission to create tenant-local agents and obtain tokens carrying granted permissions, enabling persistent access and further exploitation. Proofpoint notified Microsoft before publication and reported no observed in-the-wild exploitation.

A single blueprint can support up to 250 agent identities, potentially multiplying the impact of one consent decision. Limited visibility into inherited permissions complicates governance and auditing, while low awareness of agent-consent risks may leave users more willing to authorize malicious AI agents. Proofpoint recommends restricting consent, enforcing least privilege, applying agent-specific identity controls, monitoring blueprint and agent creation events, and warning employees about agent-consent risks.
Is your org in this campaign?Get the infrastructure and lures behind it.
Hunt this campaign
Event timeline

How this story unfolded

Events from the most recent confirmed update back to the earliest known activity.

2 events
  1. Reported Nov 9, 20268d ago

    Proofpoint discloses BluePhishing proof of concept targeting Entra agent consent

    Proofpoint published research demonstrating how consent to a malicious Microsoft Entra agent blueprint could enable attackers to create tenant-local agent identities and obtain tokens carrying granted permissions. A single blueprint can support up to 250 agent identities; Proofpoint reported no observed in-the-wild exploitation and outlined consent restrictions, least privilege, and monitoring as defenses.

    BluePhishing: Initial Access via Third-Party Agent Blueprint Consent | Proofpoint US
  2. Reported Nov 9, 20268d ago

    Proofpoint notifies Microsoft about BluePhishing before disclosure

    Proofpoint notified Microsoft about its BluePhishing attack technique before publishing the technical details.

    BluePhishing: Initial Access via Third-Party Agent Blueprint Consent | Proofpoint US
Linked entities

Related entities

Vulnerabilities, threat actors, malware, products, organizations, and breaches Mallory has linked to this story.

Open in app →

Affected products

3 linked
Microsoft Entra IdMicrosoft 365Entra
Do you run this?Get the infrastructure, lures, and IOCs behind this campaign, ready to push into your email and identity stack.
Hunt This Campaign
Mallory platform

See the full picture, correlated to your attack surface.

This page covers what’s public. Mallory adds the parts that aren’t: which of your assets are affected, which threat actors are using it right now, and what to deploy next.

Exposure mappingMap indicators from this story to your assets and identify affected systems in minutes.
Threat actor evidenceEvery observed campaign, victim, and pivot linked to actors named in this story.
Associated malwareMalware, exploits, and IOCs connected to the activity described here.
Detection signaturesYARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Scheduled alertsGet matching new stories delivered to your team as they break, not the next morning.
AI threadsAsk questions about this story and take action on the answers.