Google Ads Deliver Browser-Locking Fake Security Scams
Social Engineering & Fraud · 6 sources · Updated 1mo ago · First seen Sep 24, 2026
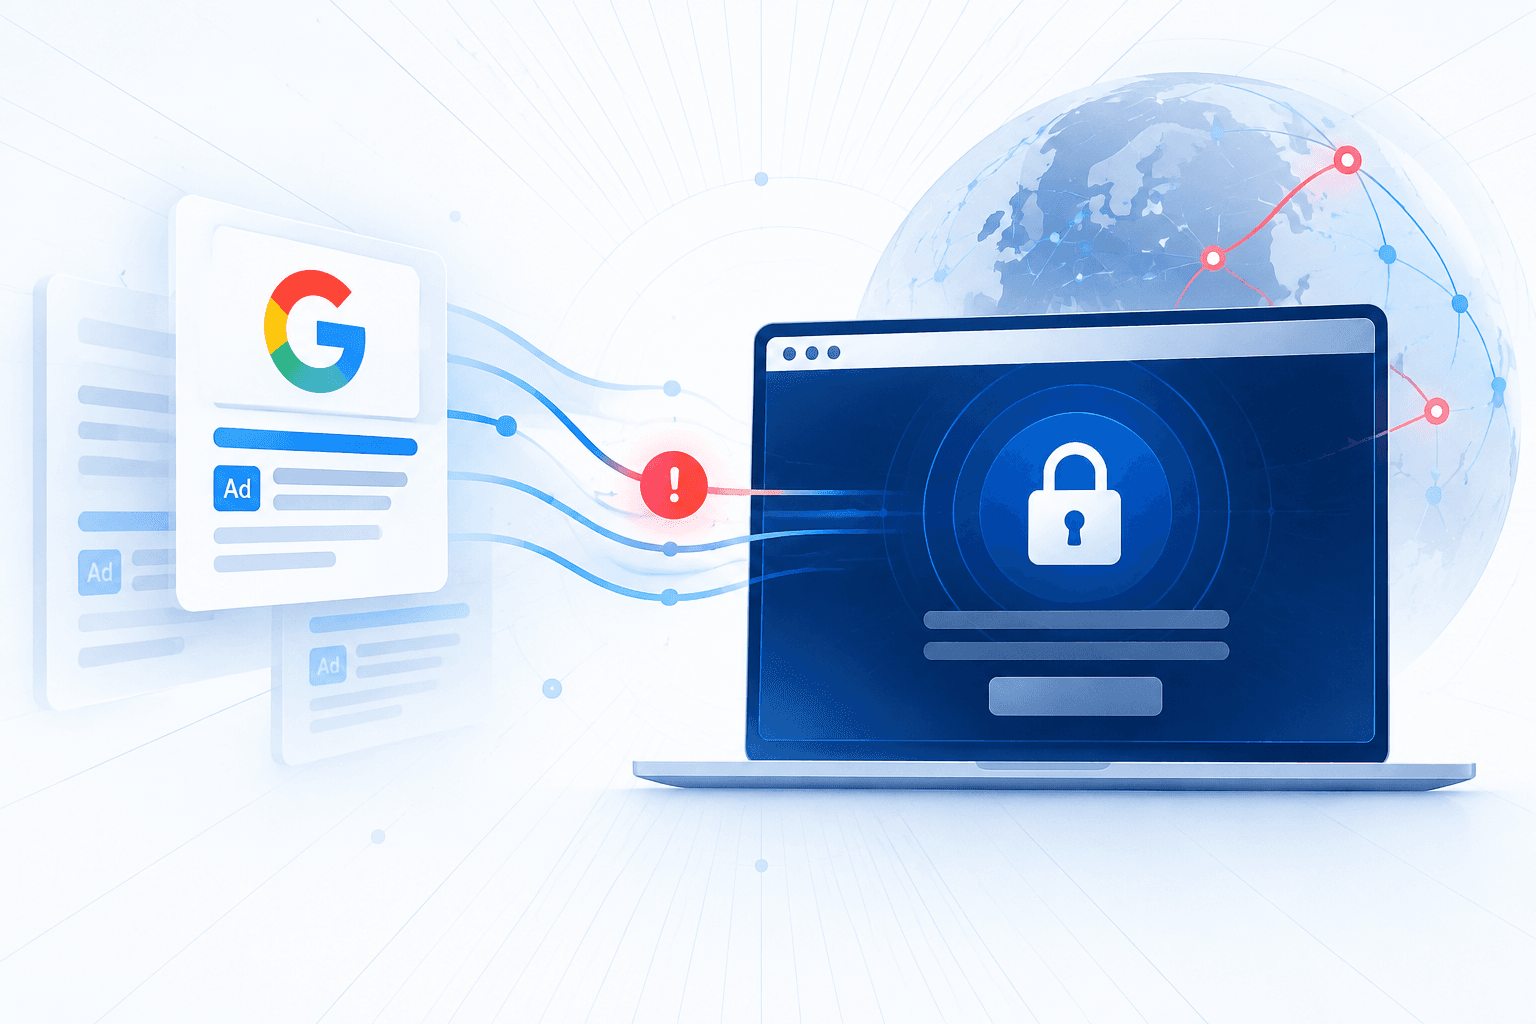
A cloud-hosted tech-support scam campaign used more than 250 Google Ads campaign IDs to route users through a benign-looking fake “ShopEase” storefront before presenting operating-system-specific security lockers impersonating Microsoft Defender on Windows and Apple on macOS. Between August 31 and September 14, it affected at least 619 organizations, chiefly in the United States, Japan, and Australia, with ads appearing across at least 284 legitimate publisher sites. Victims were pressured to call a fraudulent support number through full-screen browser takeovers, keyboard locking, hidden cursors, warning audio, and intentional browser-performance degradation.
The campaign reflects advanced browser-based scareware techniques also documented in CypherLoc, which uses encrypted JavaScript loaders to validate, decrypt, and execute concealed payloads before replacing the initial page with a fake security warning. Such lockers evade automated inspection through interaction checks such as required mouse movement and staged AES decryption of command-and-control details and payloads, while assembling the malicious interface entirely in browser memory. They can further heighten credibility by displaying a victim’s public IP address and fake login forms, while repeatedly relocking the browser when users attempt to recover control.