Mallory
← Back to News
credential-stealer-activityinitial-access-methodloader-delivery-mechanismcryptocurrency-platform-risk

Macfinger ClickFix Campaign Delivers DownTheDRAIN macOS Infostealer and Wallet Drainer

Malware Intelligence · 2 sources · Updated 3d ago · First seen Nov 13, 2026
Macfinger ClickFix Campaign Delivers DownTheDRAIN macOS Infostealer and Wallet Drainer

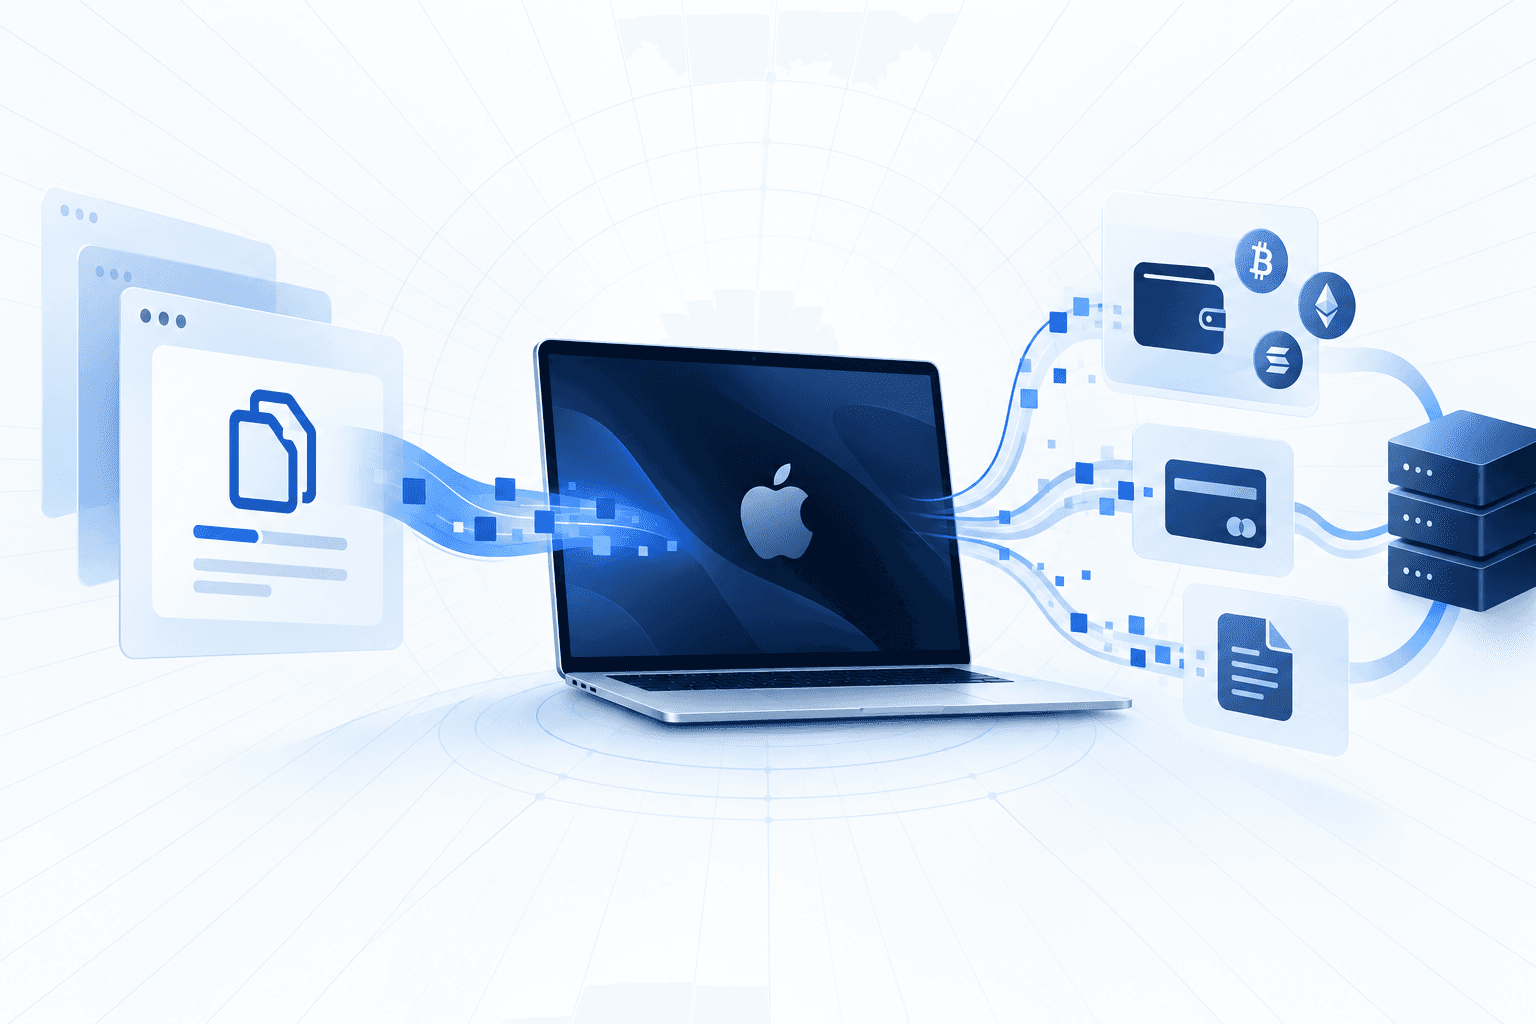
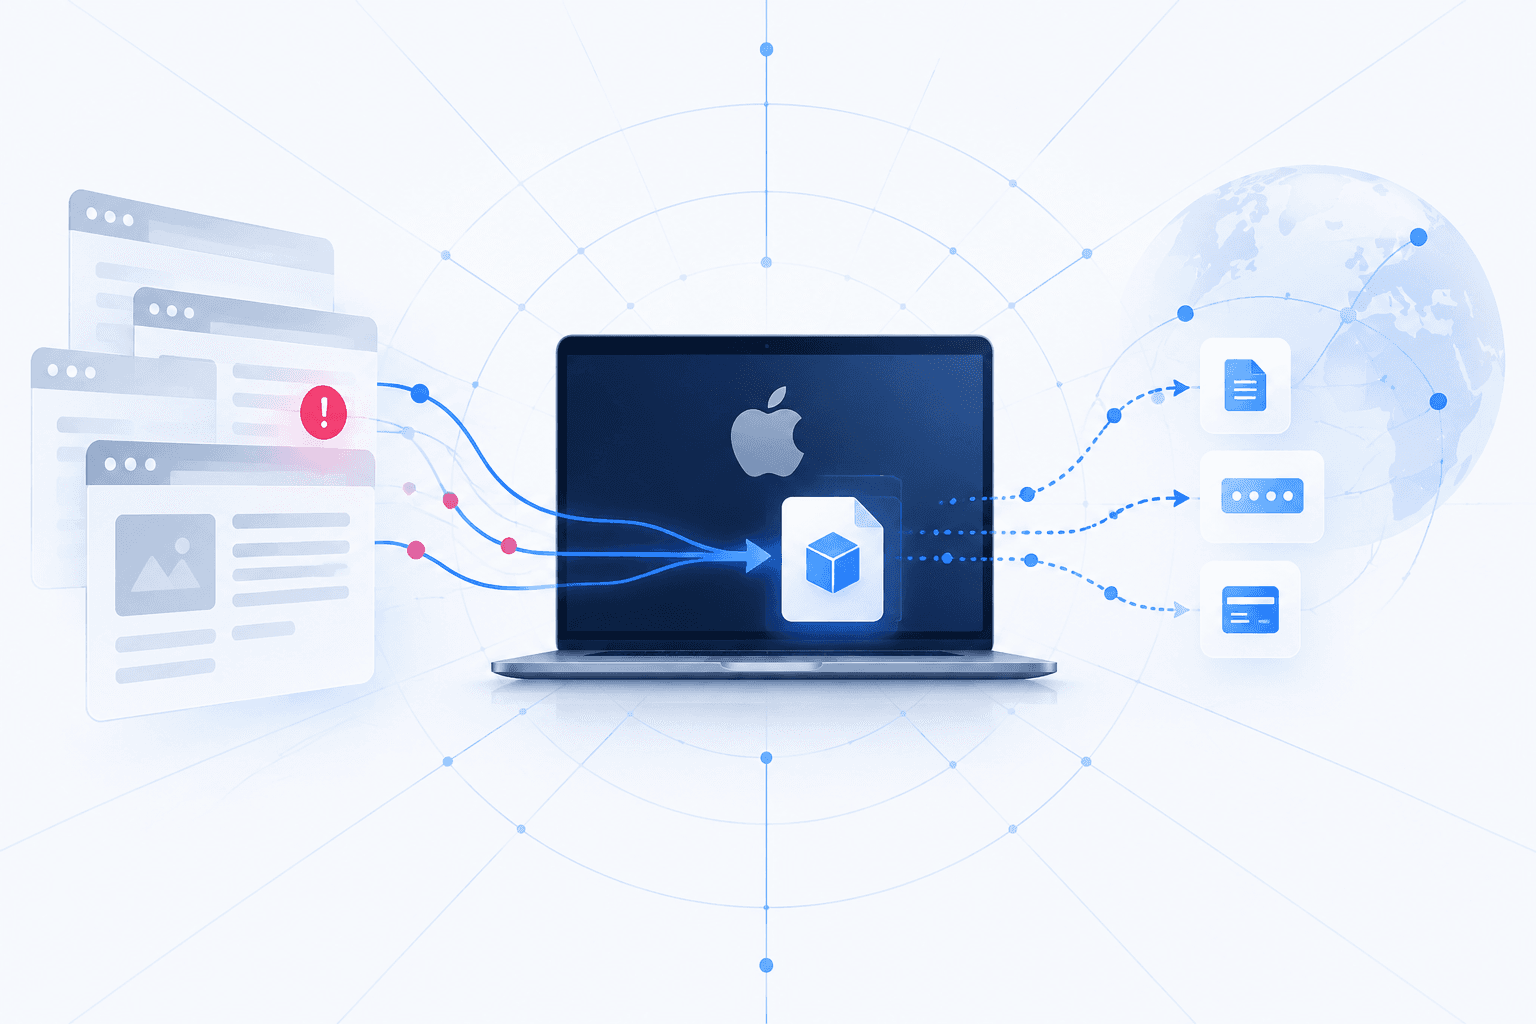
The Macfinger social-engineering campaign uses fake CAPTCHA pages to trick macOS users into pasting malicious commands into Terminal, delivering an infostealer nicknamed DownTheDRAIN. Bradley Duncan’s analysis found that the commands download a shell script that installs an ARM64 Mach-O binary; a related report identifies its destination as $HOME/Library/Caches/com.apple.update. The malware harvests sensitive local data and targets cryptocurrency wallets. Its nickname refers to a DRAIN function described by Huntress as identifying cryptocurrency wallet addresses and redirecting funds to an attacker-controlled wallet.

In Duncan’s test, macOS 26.7.3 blocked the malware and moved it to Trash before sensitive data could be exfiltrated, although four HTTP POST requests were observed before the block. Related reporting states that updated Apple XProtect protections block known builds, while outdated protections and repackaged binaries remain concerns. Defenders should keep XProtect current, monitor suspicious Terminal execution and executables in user cache directories, and consider restricting executable launches from user-writable locations.
Hunt this familyPull IOCs and campaign context straight into your stack.
Get the IOCs
Event timeline

How this story unfolded

Events from the most recent confirmed update back to the earliest known activity.

4 events · Aug 2026 – Nov 11, 2026
  1. Nov 11, 20267d ago

    DownTheDRAIN test shows macOS blocking the payload before sensitive-data exfiltration

    Bradley Duncan analyzed a Macfinger infection example that used a Bash installer to deliver an ARM64 Mach-O infostealer, naming it DownTheDRAIN after the function described by Huntress. In the reported test, the malware generated four HTTP POST requests before macOS 26.7.3 blocked it and moved it to Trash, preventing sensitive-data exfiltration.

    Macfinger ClickFix campaign sends DownTheDRAIN infostealer for macOS
  2. Sep 25, 20262mo ago

    Duncan examines malware delivered by Macfinger

    Bradley Duncan examined malware distributed through the Macfinger ClickFix campaign.

    Macfinger ClickFix campaign sends DownTheDRAIN infostealer for macOS
  3. Sep 22, 20262mo ago

    Duncan documents the Macfinger ClickFix campaign

    Bradley Duncan documented the Macfinger ClickFix campaign, which uses fake CAPTCHA pages to persuade macOS users to paste malicious commands into Terminal.

    Macfinger ClickFix campaign sends DownTheDRAIN infostealer for macOS
  4. Aug 2026

    Huntress publishes analysis of cryptocurrency-draining DRAIN function

    Andrew Brandt published a Huntress analysis describing a DRAIN function and its associated code. Huntress reported that the function identifies cryptocurrency wallet addresses and can redirect funds to an attacker-controlled wallet.

    Macfinger ClickFix campaign sends DownTheDRAIN infostealer for macOS
Linked entities

Related entities

Vulnerabilities, threat actors, malware, products, organizations, breaches, and observables Mallory has linked to this story. Indicator values are masked here and available in full in the app.

Open in app →

Malware

1 linked

Affected products

1 linked
Macos

Observables

8 linked

Indicator values are masked on this page. See the values in Mallory Domains, IPs, hashes, and URLs are exportable to your SIEM.

Do you run this?Pull the IOCs, campaigns, and victimology behind this family, ready to push into your SIEM and EDR.
Hunt This Malware
Mallory platform

See the full picture, correlated to your attack surface.

This page covers what’s public. Mallory adds the parts that aren’t: which of your assets are affected, which threat actors are using it right now, and what to deploy next.

Exposure mappingMap indicators from this story to your assets and identify affected systems in minutes.
Threat actor evidenceEvery observed campaign, victim, and pivot linked to actors named in this story.
Associated malwareMalware, exploits, and IOCs connected to the activity described here.
Detection signaturesYARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Scheduled alertsGet matching new stories delivered to your team as they break, not the next morning.
AI threadsAsk questions about this story and take action on the answers.