Retadup Worm Revived Through Old USB Drives and Re-Registered Domains to Deliver CoffeeLoader
Malware Intelligence · 15 sources · Updated 40m ago · First seen Nov 16, 2026
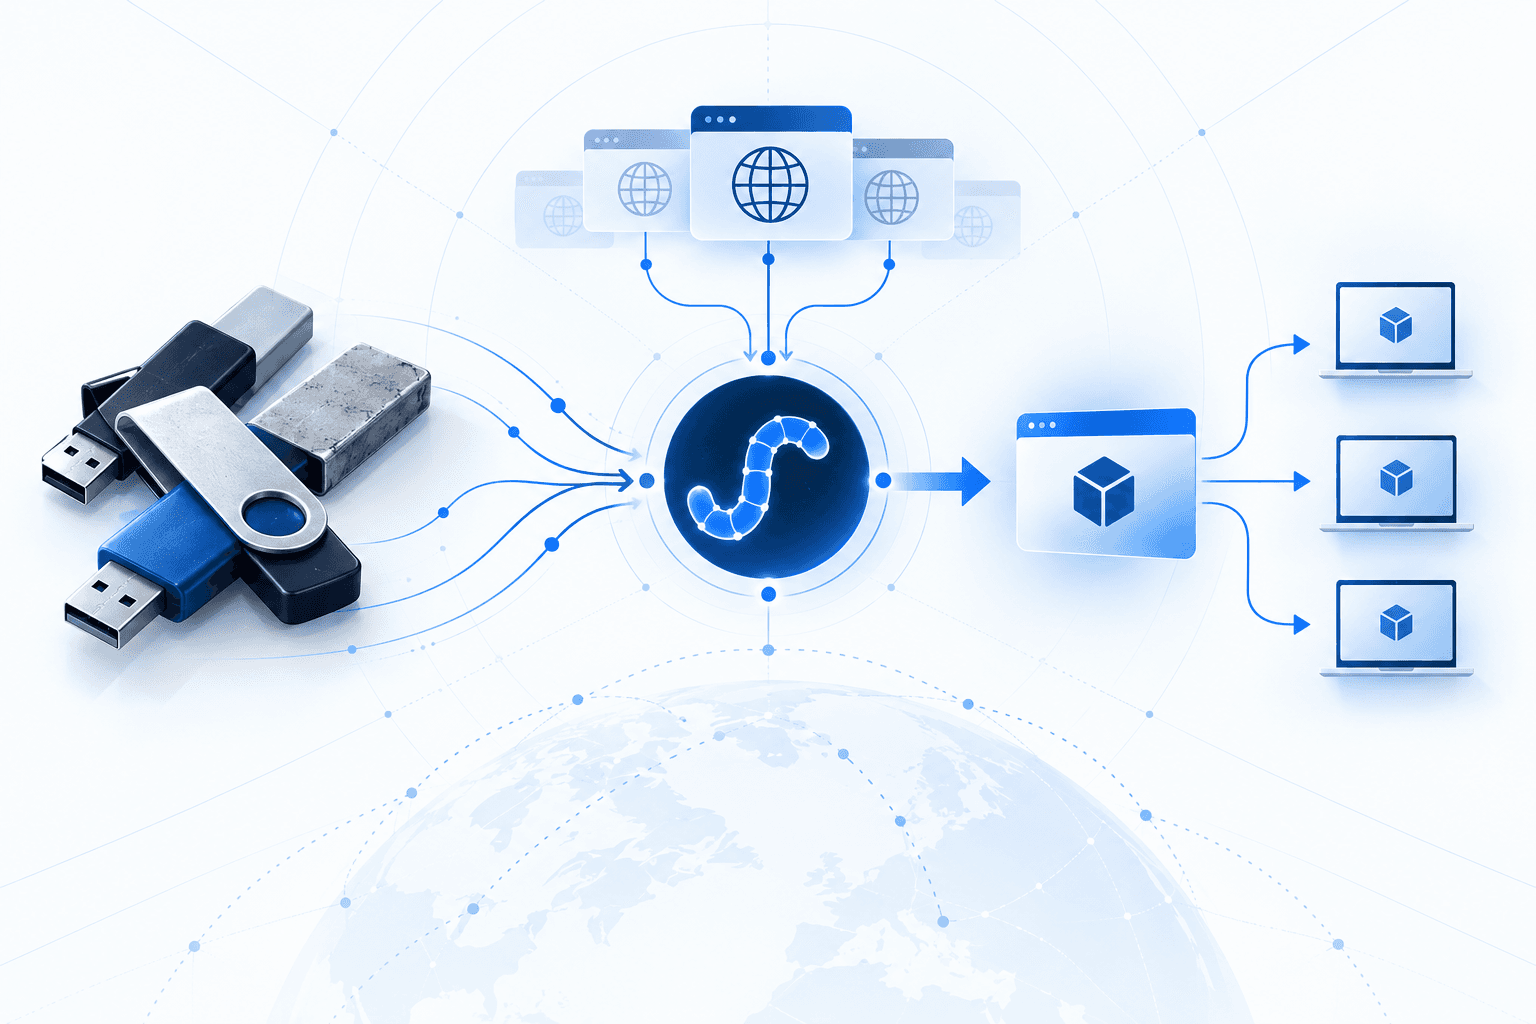
Surviving copies of the Retadup worm are distributing CoffeeLoader after attackers re-registered former command-and-control domains beginning in 2024, according to Kaspersky. French law enforcement dismantled the original botnet in 2019 and disinfected more than 850,000 computers, but the worm could persist on infected removable drives and computers that remained offline during the operation. Kaspersky reported blocking approximately 15,000 Retadup infection attempts during the first nine months of 2026, with detections concentrated in Peru, Angola, and Russia.
The revived infrastructure directs remaining Retadup infections to download CoffeeLoader, which uses encrypted code fragments and GPU-assisted decryption to hinder sandbox analysis. The loader establishes startup persistence and accepts encrypted, digitally signed commands to retrieve additional payloads. Organizations should scan old USB drives and previously offline computers before reconnecting them, avoid suspicious shortcuts, maintain updated endpoint protection, and keep offline backups. The resurgence highlights the lasting risk from dormant malware and abandoned command infrastructure.