Conficker Variant Revived Botnet and Spread via MS08-067, SMB, and Removable Media
Malware Intelligence · 4 sources · Updated 3mo ago · First seen Apr 9, 2009

A new Conficker variant, also known as Kido or Downadup, reactivated infected hosts through peer-to-peer communications and resumed worm behavior by spreading between systems and downloading additional malware. Kaspersky reported that compromised machines pulled down a rogue antivirus detected as FraudTool.Win32.SpywareProtect2009.s and the Waledac email worm, detected as Email-Worm.Win32.Iksmas.atz, which added spam-sending and data-theft capabilities to already infected endpoints.
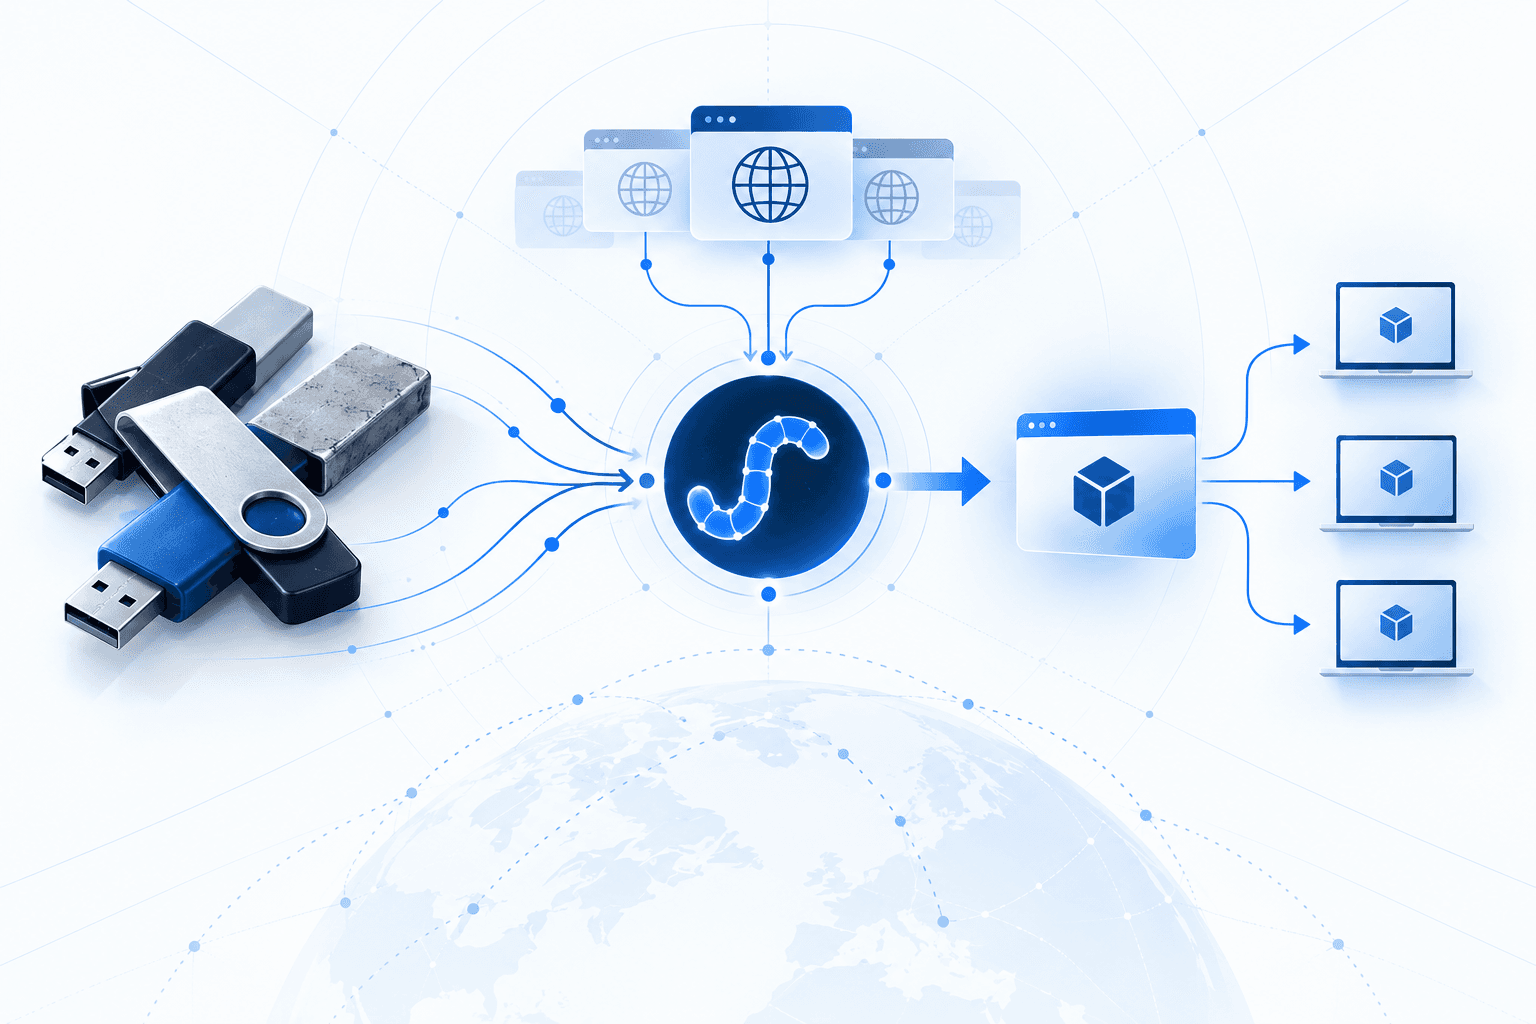
Technical analysis and sample listings show the malware propagated through multiple channels, including exploitation of MS08-067, SMB brute forcing, and removable media using autorun.inf and disguised DLL files. The worm established persistence, injected into processes such as Explorer.exe and Svchost.exe, blocked DNS access to security resources, altered TCP settings, disabled protections and services, deleted restore points, and used a domain generation algorithm to maintain resilience on legacy Windows systems, particularly older Windows XP environments.