
Mallory
← Back to News
ai-platform-securitystandards-framework-updateinternet-exposed-serviceembedded-device-vulnerability

OWASP Incubator Project Maps Security Risks in GPU Clouds and AI Data Centers

Emerging Technology Risk · 2 sources · Updated 1d ago · First seen Nov 16, 2026
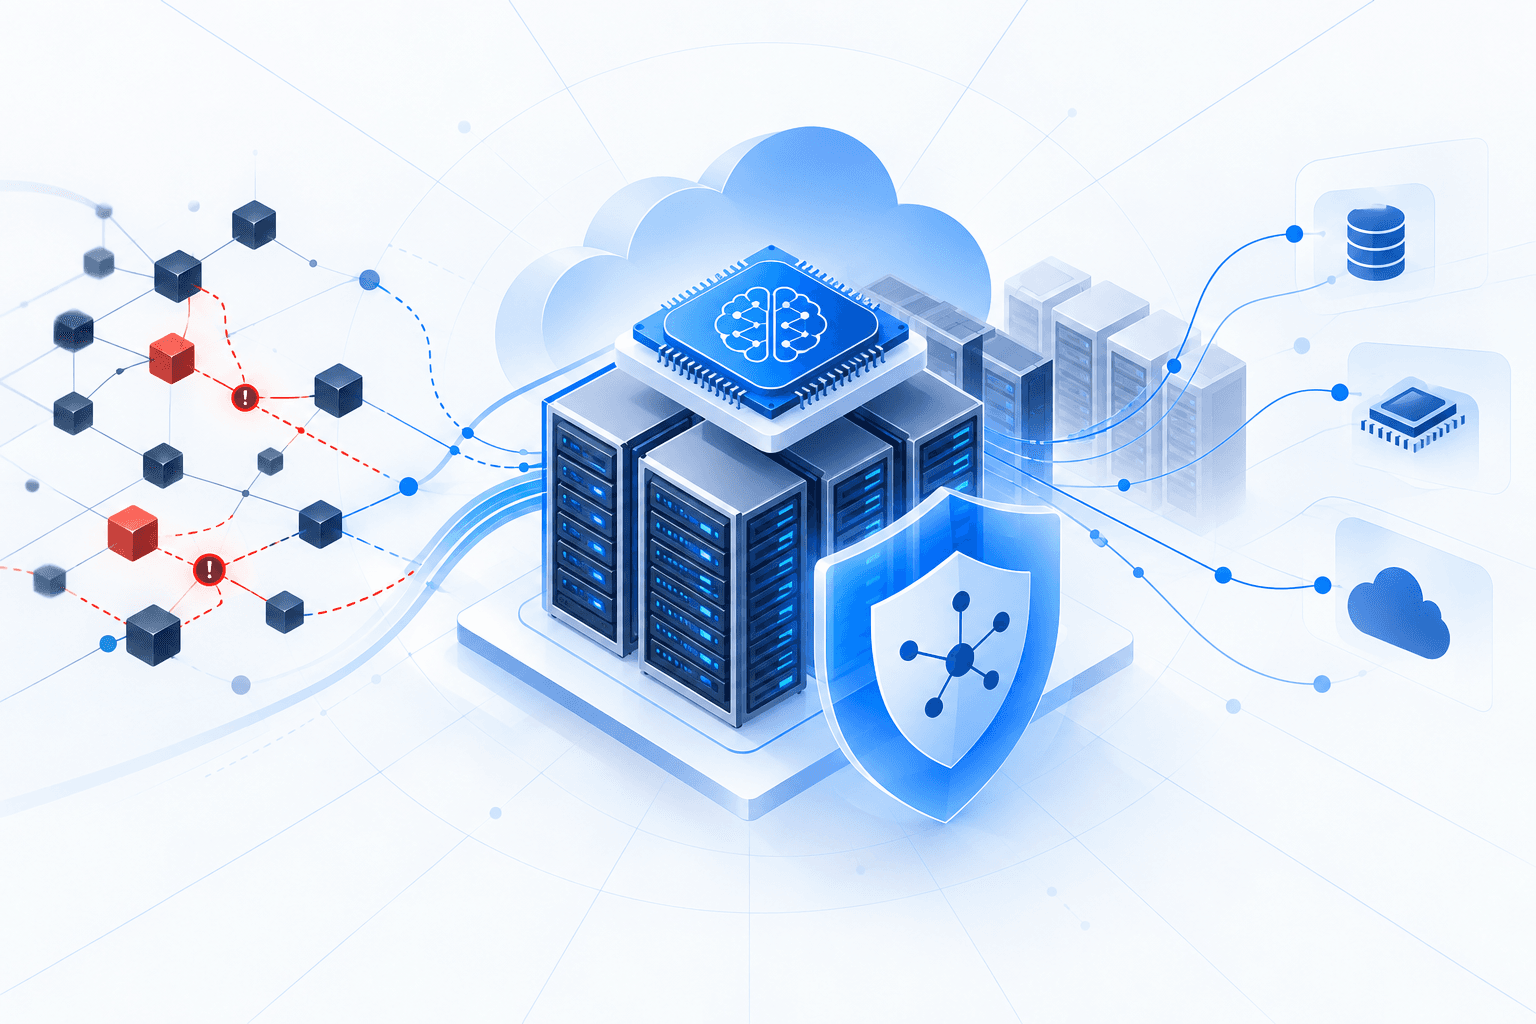
OWASP Incubator Project Maps Security Risks in GPU Clouds and AI Data Centers

OWASP’s new Top 10 Neocloud and AI Data Center Security Risks Incubator Project addresses infrastructure weaknesses beneath AI models, applications, and agents. Its five highest-ranked risks are hardware and firmware compromise, insecure GPU interconnects, inadequate tenant isolation, insecure out-of-band management, and supply chain compromise. The framework highlights how shared GPU infrastructure adapted from trusted high-performance computing environments can expose multiple customers to attacks that conventional security monitoring may miss.

Supporting examples include internet-exposed IPMI management interfaces, the AMI MegaRAC authentication-bypass vulnerability CVE-2024-54085, and the NVIDIAScape container-escape vulnerability CVE-2025-23266. Compromised baseboard management controllers (BMCs) can provide persistent access outside normal operating-system visibility. Recommended defenses include isolating management networks, keeping BMCs off the public internet, restricting administrative access, and promptly patching firmware. Organizations buying GPU capacity should also verify whether provider audits cover GPU infrastructure and resold capacity, rather than assuming general cloud assurances extend to those environments.
New surface, new adversariesTrack how attackers are adapting to this technology.
Track this risk
Event timeline

How this story unfolded

Events from the most recent confirmed update back to the earliest known activity.

1 event
  1. Reported Nov 16, 20261d ago

    OWASP introduces Top 10 security risks for neoclouds and AI data centers

    OWASP introduced an Incubator Project led by Lava’s Michael Katchinskiy and Yakir Kadkoda to assess infrastructure risks for neocloud providers, customers, and AI data center operators. The framework ranks ten risks, rating hardware and firmware compromise, insecure interconnects, inadequate tenant isolation, insecure out-of-band management, and supply chain compromise as critical.

    New OWASP Top 10 Exposes Hidden Security Weaknesses in Neocloud and AI Infrastructure | Cryptika Cybersecurity
Linked entities

Related entities

Vulnerabilities, threat actors, malware, products, organizations, and breaches Mallory has linked to this story.

Open in app →

Organizations

1 linked
Open Worldwide Application Security Project
Do you run this?Follow how adversaries are adapting to this technology, and where it touches your stack today.
Track This Risk
Mallory platform

See the full picture, correlated to your attack surface.

This page covers what’s public. Mallory adds the parts that aren’t: which of your assets are affected, which threat actors are using it right now, and what to deploy next.

Exposure mappingMap indicators from this story to your assets and identify affected systems in minutes.
Threat actor evidenceEvery observed campaign, victim, and pivot linked to actors named in this story.
Associated malwareMalware, exploits, and IOCs connected to the activity described here.
Detection signaturesYARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Scheduled alertsGet matching new stories delivered to your team as they break, not the next morning.
AI threadsAsk questions about this story and take action on the answers.